
Hackers Use MiningDropper to Deliver Infostealers, RATs, and Banking Malware on Android
A fast growing Android malware campaign is using a framework called MiningDropper to push far more dangerous threats onto phones disguised as normal apps. Researchers describe it as a multi stage delivery system that can lead to infostealers, remote access trojans, banking malware, or even cryptocurrency mining activity on infected devices. The campaign reaches victims […]
Vercel Confirms Data Breach Hackers Claim Access to Internal Systems
Vercel has disclosed a significant security incident after threat actors gained unauthorized access to internal systems, with a hacker group reportedly attempting to sell stolen data for $2 million on underground forums. Vercel, one of the most widely used frontend cloud platforms powering millions of developer deployments, confirmed the breach in an official security bulletin […]
OpenAI Expands Cyber Defense Program With GPT-5.4-Cyber Access for Trusted Organizations
OpenAI has officially launched the expanded phase of its Trusted Access for Cyber program. Granting select organizations access to its specialized GPT-5.4-Cyber model to strengthen digital defenses across critical infrastructure, financial services, and open-source security communities. The program operates on a tiered trust model advanced AI cyber capabilities are made broadly available to defenders, but access scales based on […]
Apple Works on Fix for iPhone Passcode Bug Linked to Missing Czech Keyboard Character
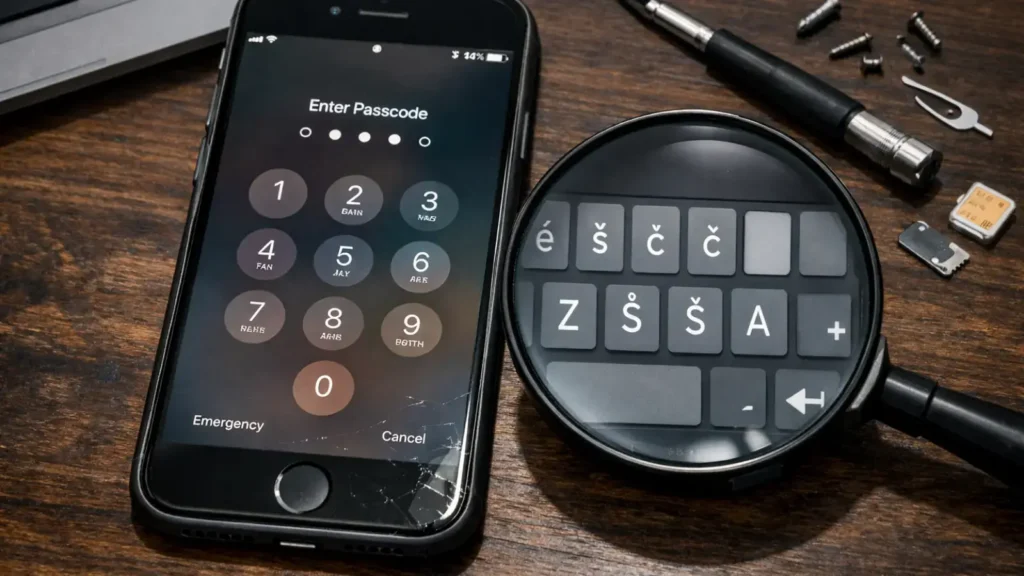
Apple is reportedly developing a software fix for a frustrating iOS 26 bug that has left some users entirely locked out of their iPhones for months. According to a recent report by The Register, Cupertino’s software engineers are scrambling to patch a keyboard interface flaw that inadvertently removed a specific special character necessary for unlocking […]
Researcher Uses Claude Opus to Build a Working Chrome Exploit Chain
Amidst the heated debate surrounding Anthropic’s recent announcement of its Mythos and Project Glasswing models, a security researcher has demonstrated the tangible cybersecurity implications of frontier AI. Moving beyond theoretical warnings, the researcher successfully utilized Claude Opus to construct a fully functional exploit chain targeting Google Chrome’s complex V8 JavaScript engine. The experiment highlights a […]
Fiverr Allegedly Leaks User Information to Google Indexing, Researchers Say
Freelance service platform Fiverr is facing a significant privacy incident after researchers discovered that sensitive customer files are publicly accessible and indexed by Google search. According to a recent disclosure on Hacker News, an insecure file-hosting configuration has exposed personal identifiable information (PII), including completed tax forms, that were exchanged between freelancers and clients. The […]
Nearly 6 Million Internet-Facing FTP Servers Still Exposed in 2026, Censys Warns
According to a recent April 2026 report by security researcher Himaja Motheram at Censys, just under 6 million internet-facing hosts are still running the File Transfer Protocol (FTP). While this marks a significant 40% decline from the 10.1 million servers observed in 2024, the presence of this decades-old protocol continues to pose an exposure risk […]
Hackers Target TP-Link Routers With Mirai Malware in CVE-2023-33538 Exploitation Attempts
A known security flaw in several end-of-life TP-Link Wi-Fi routers is being actively targeted by hackers trying to install Mirai-based botnet malware on vulnerable devices. The vulnerability, tracked as CVE-2023-33538, affects multiple TP-Link models that no longer receive vendor updates, leaving users with no official patch to apply. The affected routers include the TL-WR940N (versions […]
Payouts King Rises as New Ransomware Threat Linked to Former BlackBasta Affiliates
A relatively unknown ransomware group called Payouts King has emerged as a serious cybersecurity threat, carrying the torch of the now-defunct BlackBasta operation. Since its appearance in April 2025, the group has quietly carried out targeted attacks while remaining largely under the radar, combining aggressive data theft with selective file encryption. BlackBasta was one of […]
EUs New Age Verification App Can Be Hacked Within 2 Minutes, Researchers Claim
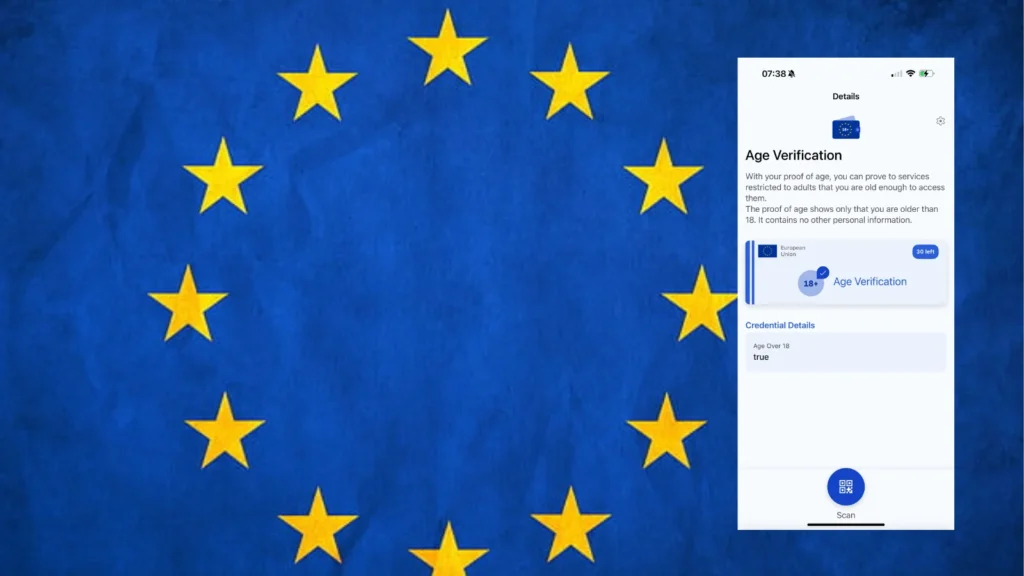
The European Commission’s newly launched Digital Age Verification App, unveiled on April 14, 2026, to protect minors from harmful online content, has already been compromised, with UK-based security consultant Paul Moore demonstrating a full authentication bypass in under two minutes. During app setup, users are prompted to create a PIN. The app then encrypts this […]