
Hackers Actively Exploiting AI Deployments 91,000+ Attack Sessions Observed
Security researchers have identified over 91,000 attack sessions targeting AI infrastructure between October 2025 and January 2026, exposing systematic campaigns against large language model deployments. GreyNoise’s Ollama honeypot infrastructure captured 91,403 attack sessions during this period, revealing two distinct threat campaigns. The findings corroborate and extend previous research from Defused on AI system targeting. The […]
ChatGPT Health A Dedicated Space for Health Queries With Strong Privacy and Security
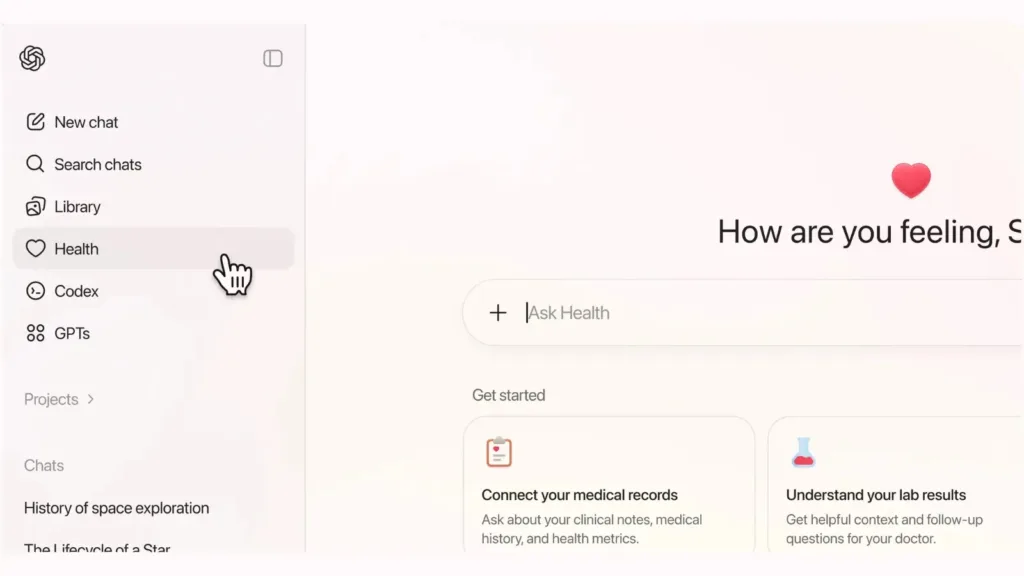
OpenAI has launched ChatGPT Health, a specialized platform that helps users securely manage their health information and receive intelligent support for wellness-related questions. With over 230 million people using ChatGPT weekly for health inquiries, the company recognized the need for a dedicated, secure space to handle sensitive medical data. What Is ChatGPT Health? ChatGPT Health operates […]
BlueDelta Hackers Attacking Microsoft OWA, Google, and Sophos VPN Users to Steal Logins
BlueDelta, a Russian state-sponsored threat group linked to the country’s military intelligence agency known as the GRU, has expanded its credential-stealing operations significantly throughout 2025. Between February and September, the group launched multiple phishing campaigns designed to deceive users of Microsoft Outlook Web Access, Google, and Sophos VPN services into surrendering their login information. This […]
Hackers Using Malicious Imageless QR Codes to Render Phishing Attack Via HTML Table
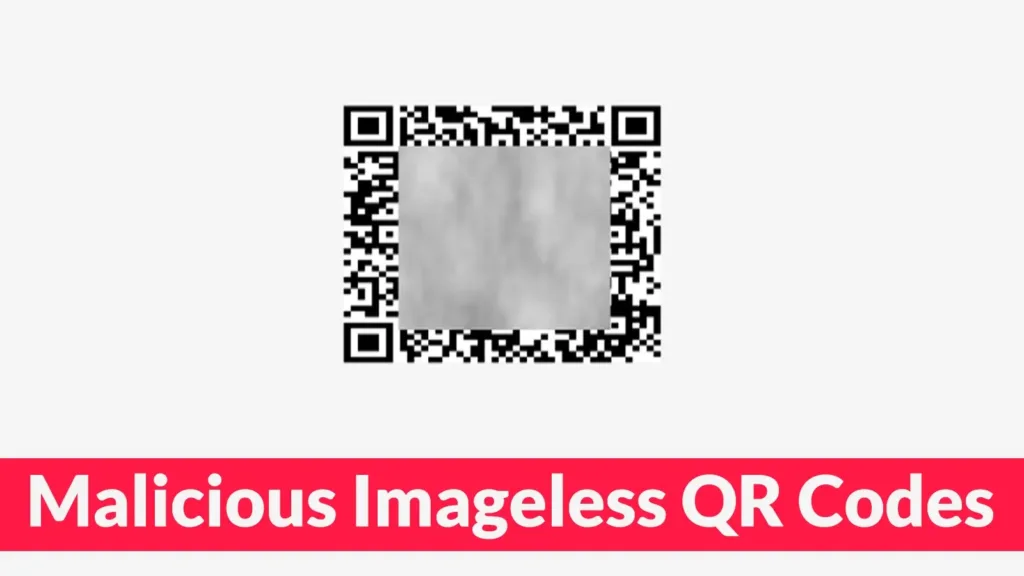
A recent phishing campaign is abusing QR codes in a new way, turning simple HTML tables into working codes that redirect users to malicious sites. Instead of embedding a QR image in the email body, the attackers build the code from hundreds of tiny table cells, each styled as black or white. The result still […]
GoBruteforcer Botnet brute-forces Passwords for FTP, MySQL, and phpMyAdmin on Linux Servers
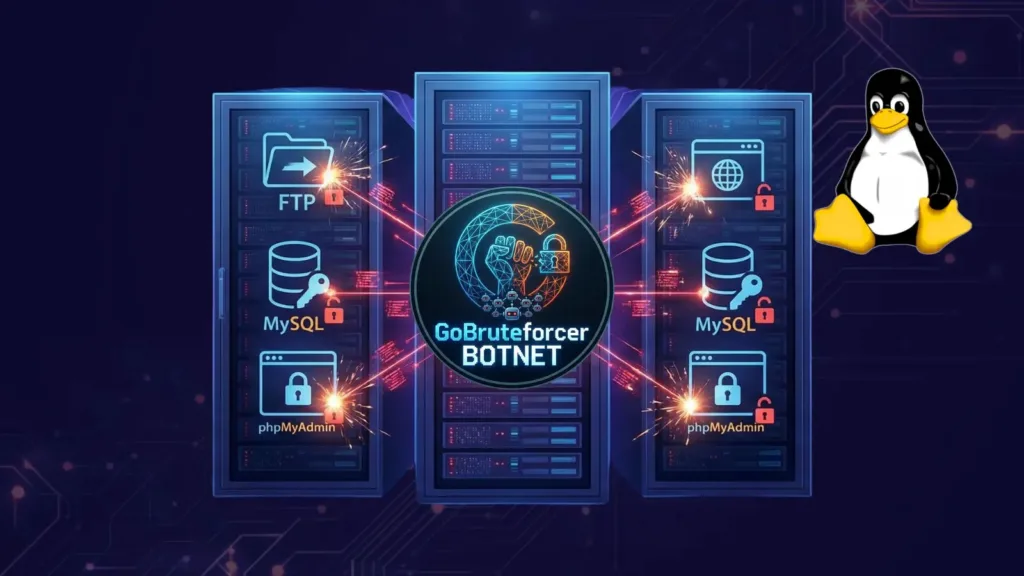
A sophisticated Go-based botnet dubbed GoBruteforcer is aggressively targeting Linux servers worldwide, brute-forcing weak passwords on internet-exposed services including FTP, MySQL, PostgreSQL, and phpMyAdmin. Check Point Research recently documented a new 2025 variant of the malware that demonstrates significant technical improvements over previous versions and has successfully compromised tens of thousands of servers. The botnet […]
Sedgwick confirms Data Breach Following TridentLocker Ransomware Gang Claim
Sedgwick has confirmed a cybersecurity incident at its government-focused subsidiary after the TridentLocker ransomware gang claimed responsibility for stealing 3.4 gigabytes of data. The breach highlights ongoing risks to federal contractors handling sensitive U.S. agency data. Claims administration giant Sedgwick acknowledged on January 4, 2026, that Sedgwick Government Solutions (SGS) experienced unauthorized access to an […]
Critical AdonisJS Vulnerability Allow Remote Attacker to Write Files On Server
A critical path traversal vulnerability in AdonisJS has been discovered that could allow remote attackers to write arbitrary files to server filesystems, potentially leading to complete system compromise. The vulnerability, tracked as CVE-2026-21440, affects the bodyparser module of the popular TypeScript-first web framework and carries a critical CVSS v4 severity rating. The security flaw resides in […]
Threat Actors Allegedly Promoting New Brutus Brute-Force Tool Targeting Fortinet Services
A threat actor operating under the moniker “RedTeam” has begun advertising a new brute-force attack tool, “Brutus,” designed to target Fortinet services, according to recent dark web intelligence. The tool is priced at $1,500, signaling growing interest in automated credential-stuffing attacks against enterprise infrastructure. Brutus is engineered to attack multiple remote access protocols, making it […]
WhatsApp Vulnerabilities Leaks Users Metadata Including Devices Operating System
WhatsApp’s multi-device encryption protocol has long leaked metadata, allowing attackers to fingerprint users’ device operating systems, aiding targeted malware delivery. Recent research highlights partial fixes by Meta, but transparency issues persist. Meta’s WhatsApp, with over 3 billion monthly active users, uses end-to-end encryption (E2EE) for message security; however, its multi-device feature reveals device information. In […]
Gmail to Discontinue POP3 Mail Fetching for External Email Accounts
Google has announced that Gmail will discontinue support for two key features regarding third-party email accounts. Starting in January 2026, the platform will drop support for “Gmailify” and the widely utilized “Check mail from other accounts” feature via POP3 fetching. For over a decade, power users have relied on Gmail not just as an email […]