
CISA and NIST Release Technical Checklist for Safeguarding Identity Tokens From Theft and Misuse
The Cybersecurity and Infrastructure Security Agency (CISA) and the National Institute of Standards and Technology (NIST) have released final technical guidance to stop attackers from forging, stealing, replaying, or misusing identity and access tokens. Published as NIST Interagency Report 8587 on September 15, 2026, it gives federal agencies and cloud service providers a roadmap for […]
Hackers Exploit WooCommerce Plugin Bug to Take Over WordPress Sites Without Login
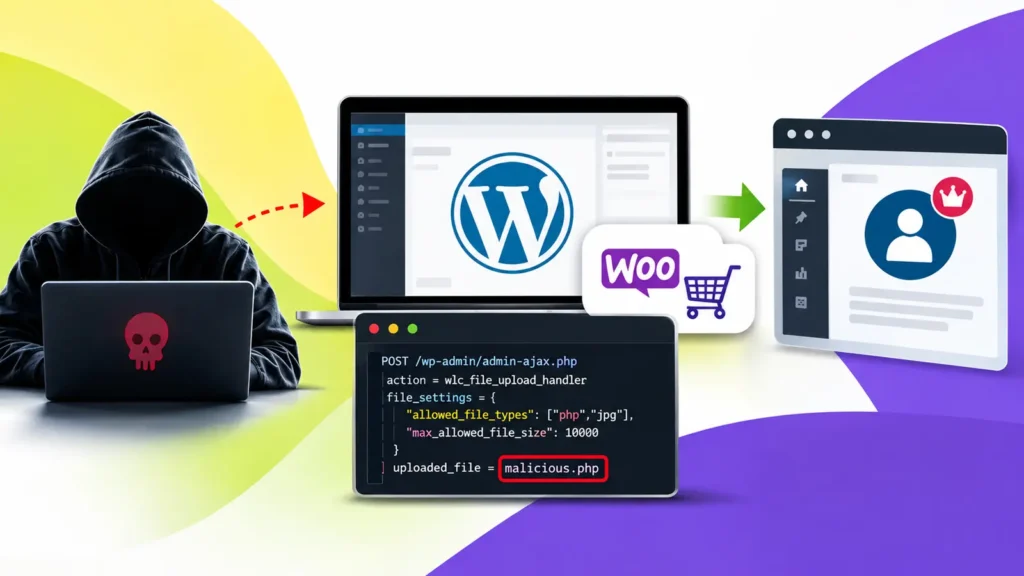
Attackers are actively exploiting a critical flaw in a WooCommerce extension to seize control of WordPress sites without a username or password. The issue affects Wholesale Lead Capture and turns a routine file-upload feature into a direct path to server access. The vulnerability, tracked as CVE-2026-27540, has a CVSS severity score of 9.8 and affects […]
Revolut Data Breach Via Fake Government Requests What We Know So Far
British fintech Revolut has confirmed a data breach in which an unauthorized third party obtained sensitive customer records by submitting fraudulent information requests through an email address using a legitimate government agency’s domain. Unlike a conventional intrusion, the attacker did not have to exploit Revolut’s app or penetrate its core banking infrastructure. Instead, the operation […]
Hackers Exploit FortiGate SSL-VPN Vulnerability to Attack Broadband Provider
Researchers have uncovered an exposed attacker-controlled staging server containing evidence of a wide-ranging intrusion targeting 3BB, the consumer brand operated by Thailand’s Triple T Broadband. The investigation links the operation to the exploitation of a critical SSL-VPN vulnerability, followed by privilege escalation, credential theft, internal reconnaissance, lateral movement, and persistent remote access. FortiGate SSL-VPN Vulnerability […]
Hackers Leverage Claude to Exfiltrate Secrets from 1.8M Android apps
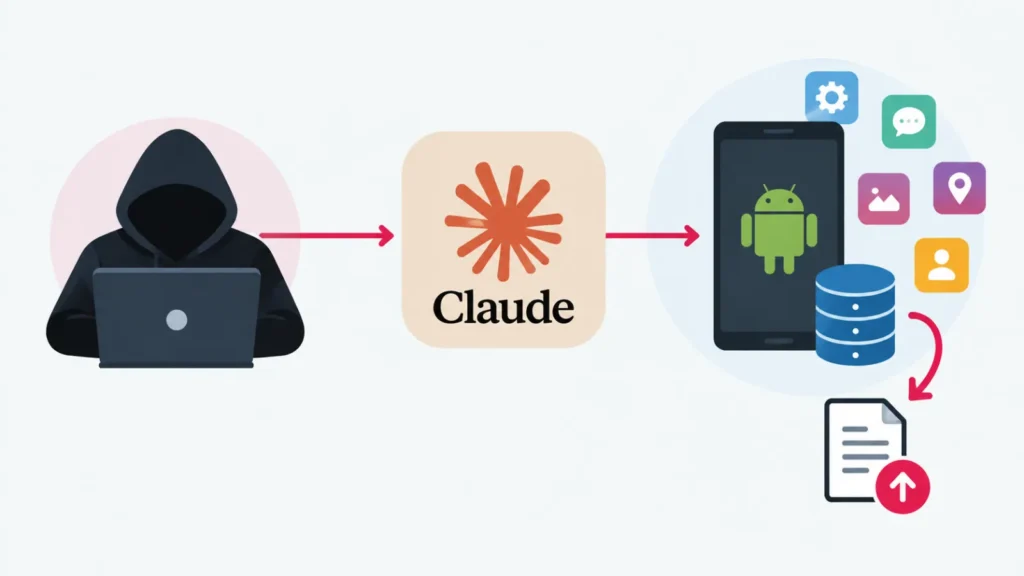
Cybercriminals linked to the ShinyHunters ecosystem used Claude to support a large-scale credential theft operation that downloaded, decompiled, and scanned 1.8 million Android applications for hardcoded secrets. The campaign shows how AI-assisted workflows can turn exposed mobile-app credentials into a rapid initial-access pipeline for enterprise breaches. According to Anthropic’s September 2026 threat intelligence report, a […]
Weekly Cybersecurity Newsletter Bulletin Microsoft 0-day, FortiOS, PAN-OS Flaw, Revolut Data Breach, and 20+ Stories
This week’s roundup covers a massive Microsoft Patch Tuesday with two exploited zero-days, active FortiGate exploitation, a critical PAN-OS root-level RCE flaw, the Revolut KYC data breach, and more than 20 other stories spanning AI-driven cyberattacks, browser and firewall zero-days, and enterprise breach disclosures. Massive Microsoft Patch Tuesday September 2026 Microsoft’s September 2026 Patch Tuesday […]
Critical Dell ObjectScale Vulnerabilities Allows Malicious Users to Compromise the Affected system
Dell Technologies released a security advisory about multiple vulnerabilities affecting Dell ObjectScale and Elastic Cloud Storage (ECS) deployments. Including a critical remote code execution flaw that could let an unauthenticated attacker compromise vulnerable systems. The advisory, tracked as DSA-2026-393, was published on September 10, 2026. The most severe issue is CVE-2026-70416, a critical untrusted-data deserialization […]
Revolut Data Breach Exposes Customers Passport Copies and Full Transaction Histories to Hackers
Revolut has disclosed a data-security incident in which sensitive customer information was released after the financial technology company received a fraudulent request that appeared to originate from a legitimate government agency. The incident reportedly exposed highly sensitive Know Your Customer (KYC) documentation and detailed financial records belonging to a limited number of users, including passport […]
Multiple VLC Media Player Vulnerabilities Allow Attackers to Corrupt or Read Heap Memory
Two security vulnerabilities in VLC Media Player could allow attackers to corrupt heap memory or disclose sensitive data from a victim’s memory. The flaws, tracked as CVE-2026-56711 and CVE-2026-73324, affect VLC Media Player versions 3.0.0 through 3.0.23 and require a victim to open a specially crafted media file or playlist entry. Fabian Wahle of Hap […]
Russia-Aligned Hackers Use GuardBreaker Prompt Injection to Disrupt AI Malware Analysis
Russia-aligned operators are testing a new way to make artificial intelligence overlook malicious code. The technique, called GuardBreaker, hides a safety-sensitive request inside an otherwise ordinary script comment, hoping that an AI code scanner refuses to continue its work. The activity was observed during an early-stage intrusion against a target in Ukraine. The VBScript was […]