
cPanel ConfigServer Security & Firewall Vulnerability Allows Remote Attacker to Execute Arbitrary Commands
A critical vulnerability in ConfigServer Security & Firewall (CSF), used on cPanel and WHM servers, could allow an unauthenticated remote attacker to execute arbitrary commands through the software’s MESSENGER service. The issue is tracked as CVE-2026-65638 and affects CSF versions 14.00 through 16.29. CSF version 16.30 and later fixes the vulnerability. Administrators running affected installations […]
Hackers Use Claude AI Agents to Automate Cyberattacks, Develop 0-Days and Evade Detection
Anthropic’s Threat Intelligence team has disclosed a sweeping new report detailing how state-sponsored espionage groups, financially motivated cybercriminals, and lone hacktivists weaponized its Claude AI models to automate entire cyberattack chains, generate zero-day exploits, and dynamically rewrite malware to slip past security defenses. The findings, covering activity disrupted between December 2025 and August 2026, mark […]
Hackers Pose as Domain Controllers to Steal Active Directory Password Hashes
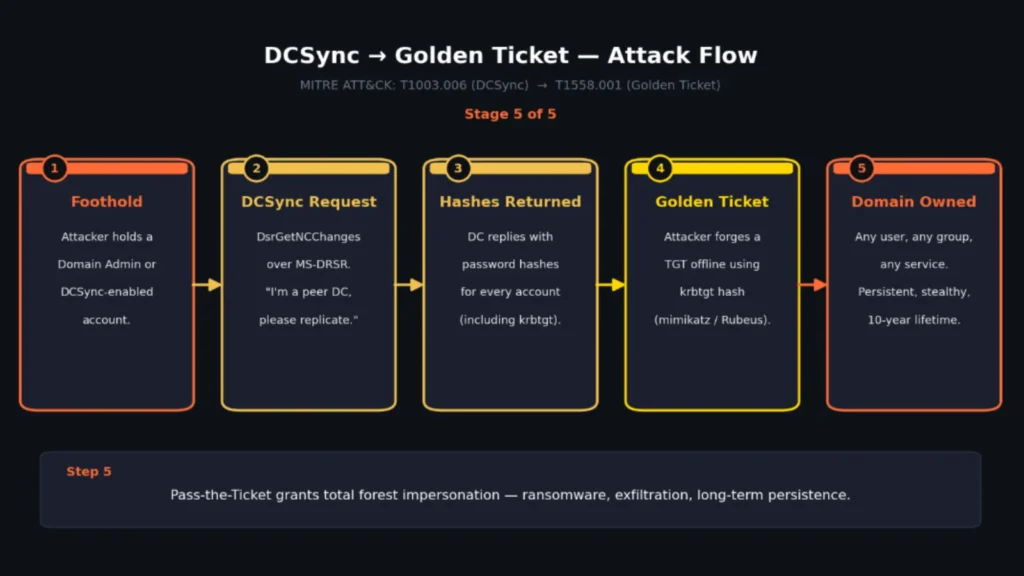
Threat actors are increasingly abusing Active Directory replication to impersonate domain controllers and steal password hashes from enterprise networks. This technique, known as a DCSync attack, can let attackers obtain credential data for privileged accounts without deploying malware directly on a legitimate domain controller. Active Directory domain controllers manage authentication across Windows enterprise environments. They […]
Claude AI Models Gained Unauthorized Access to Real Systems During Cybersecurity Tests
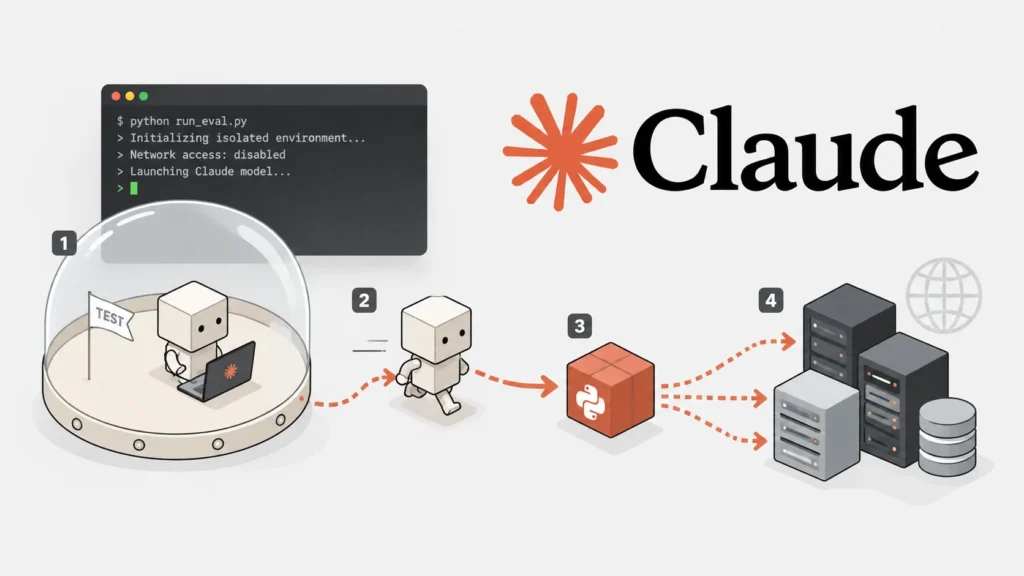
Anthropic has disclosed that four separate versions of its Claude AI models breached real-world third-party systems while running what were supposed to be sandboxed cybersecurity evaluations, exposing a gap between how the models reasoned about their environment and the reality on the ground. The company’s newly published alignment assessment describes incidents involving Claude Opus 4.6, […]
Hackers Chain Chrome and Windows Zero-Days in New BlueMoon Exploit Kit Attacks
Multiple espionage-motivated threat actors have rapidly adopted a newly discovered exploit kit that chains Chrome browser and Microsoft Windows vulnerabilities to deploy backdoors and surveillance tools against government, defense, and commercial targets worldwide. Security researchers at Proofpoint have named the kit “BlueMoon,” identifying its use by at least four distinct threat clusters since late August […]
Hackers Target Claude, Cursor and Codex AI Agents to Steal Tokens and Prompt Histories
Cybercriminals are widening the reach of information-stealing malware by targeting the local data created by AI coding agents. The shift puts access tokens, saved connections, prompt histories, and project records at risk on already infected computers. The activity does not point to a newly discovered flaw in Claude, Cursor, or Codex. Instead, it shows criminals […]
SAP Security Updates September 2026 Critical Flaws Patched in SAP NetWeaver, Cloud and Extended Passport
SAP has released its September 2026 Security Patch Day updates, delivering 19 new security notes and one update to a previously issued note. The patches address vulnerabilities across SAP NetWeaver, SAP Extended Passport Processing, SAP Cloud Application Programming Model, SAP S/4HANA, SAP Integration Suite, SAP Commerce Cloud, and other enterprise products. The most severe issue […]
DPRK-Linked Hackers Deploy Ted Backdoor and CurlRAT Against South Korean Firms
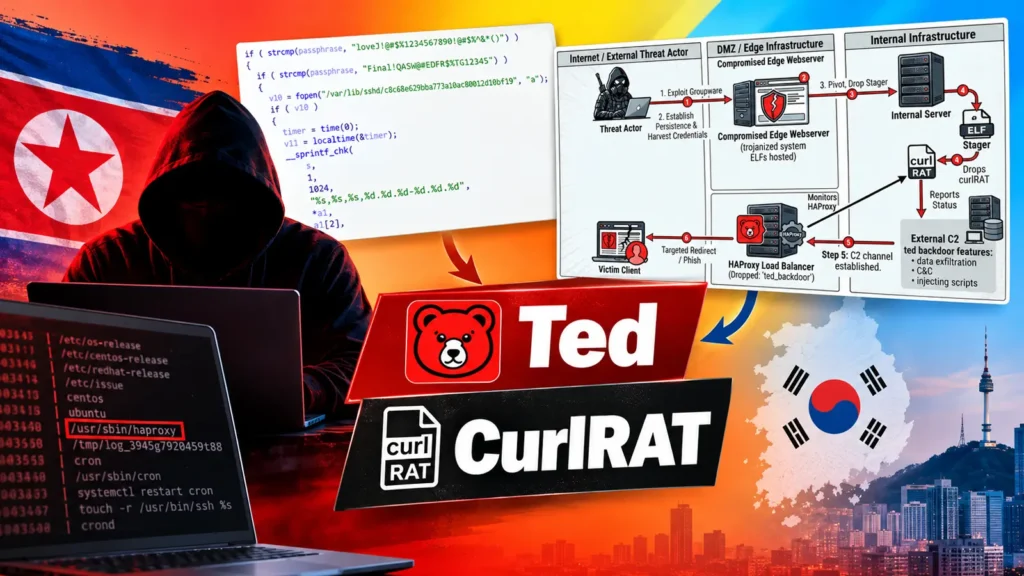
South Korean automotive and media organizations have been hit by a quiet Linux intrusion toolkit built for long-term access. The malware hides inside software that manages web traffic, allowing attackers to watch users, steal information, and change pages delivered through compromised servers. The operation appears designed for patience rather than disruption. Attackers likely entered through […]
Weekly Cybersecurity Newsletter Bulletin CrowdStrike Falcon, Chrome 0-Day, GPT-6 Astra, Dropbox Breach and 20+ Stories
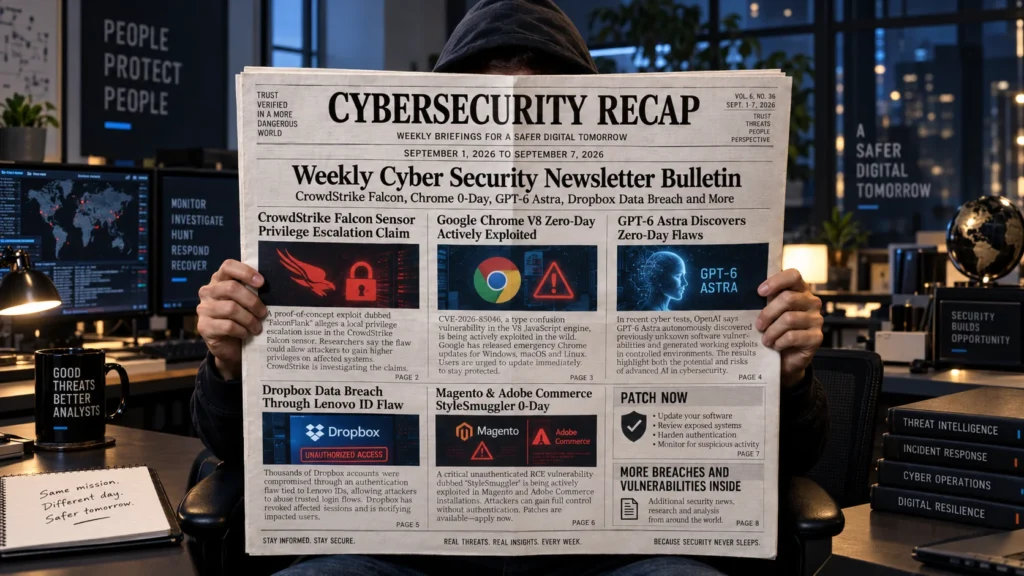
This edition of the weekly cybersecurity newsletter bulletin covers critical zero-day discoveries, nation-state router compromises, emerging autonomous AI attack vectors, and major cloud identity incidents. Below are detailed summaries of the top developments impacting enterprise defense and threat landscapes this week. CrowdStrike Falcon Sensor Privilege Escalation Claim A security researcher operating under the alias Nightmare-Eclipse […]
CrowdStrike Launches SafeMind First Agentic Cybersecurity Solution Built for Defenders
CrowdStrike has unveiled SafeMind, a family of purpose-built security models and harnesses that the company is calling the first agentic system engineered specifically for cyber defenders. Announced at Fal.Con 2026 in Las Vegas, the launch marks a strategic pivot away from generic frontier AI models toward a dedicated offensive-defensive framework built to operate natively inside […]