
Hackers Exploit LiteLLM Admin API Flaw to Steal Secrets and Target AI Gateway Servers
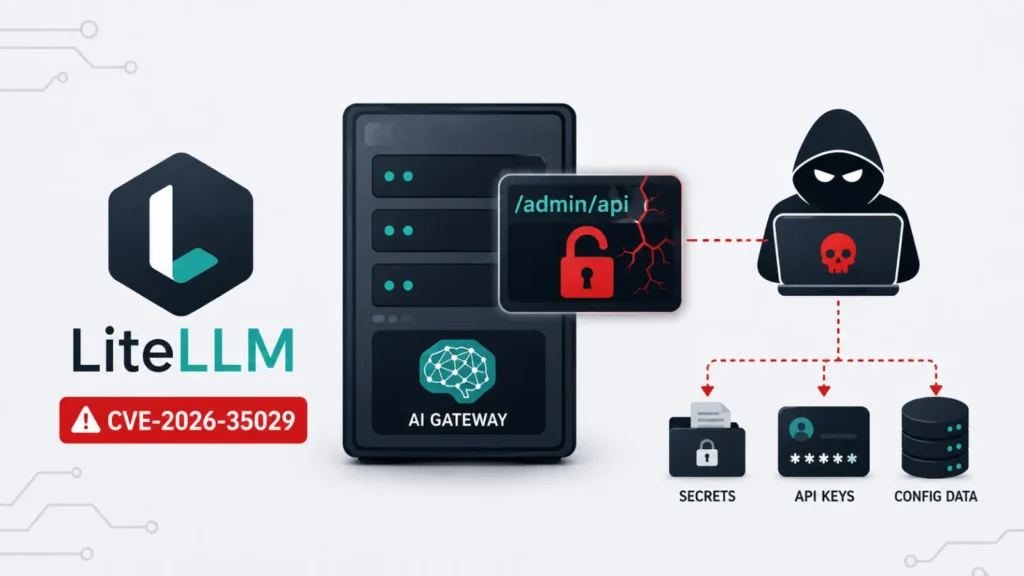
Attackers are actively probing LiteLLM AI gateway deployments for a known authorization flaw that can turn a low-privilege account into full administrative control. The issue, tracked as CVE-2026-35029, affects LiteLLM versions before 1.83.0 and allows authenticated users to access the sensitive /config/update endpoint without the required administrator role. LiteLLM acts as an AI gateway between […]
Attackers Abuse Trusted Cloud Services to Hide Phishing Attacks Against Financial Organizations
Cybercriminals are increasingly weaponizing trusted cloud platforms such as Microsoft Azure, Google Firebase, Google Cloud Storage, Amazon Web Services, and Cloudflare to host phishing infrastructure aimed squarely at the financial sector, making malicious traffic nearly indistinguishable from legitimate business activity. Security researchers describe this as a structural shift toward what some call Trusted Infrastructure Phishing, […]
Public PoC Released for Microsoft Exchange Server Pre-auth RCE Vulnerability
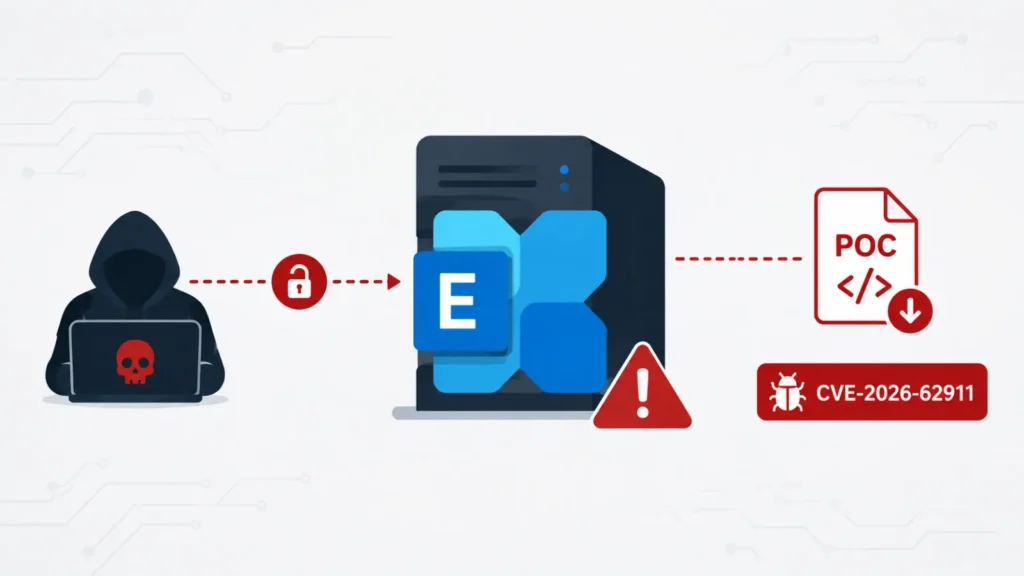
A public proof-of-concept exploit has been released for CVE-2026-62911, a Microsoft Exchange Server vulnerability linked to an authentication capture-and-replay weakness. While Microsoft classifies the issue as an elevation-of-privilege flaw, the published research describes an attack chain that can lead to unauthenticated remote code execution and a SYSTEM-level compromise on vulnerable Exchange environments. The PoC, published […]
BGP Hijack Diverts Softaculous Traffic to Deliver Malicious Virtualizor Update
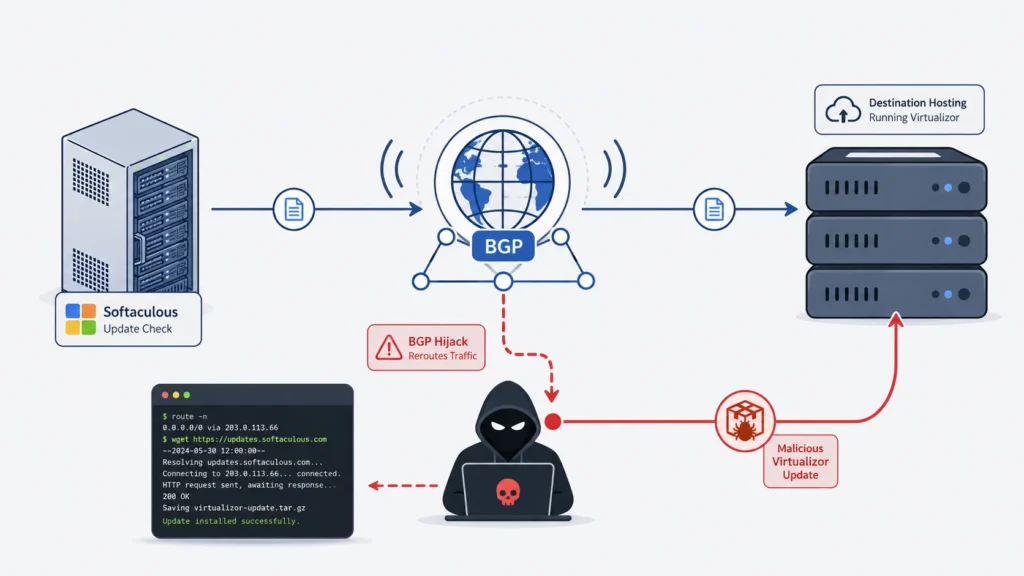
Attackers hijacked BGP routing for Softaculous last week and delivered a malicious Virtualizor update to a handful of hypervisor servers, according to a vendor incident report. Hosting providers use Virtualizor to manage VPS nodes on KVM, Xen, LXC, OpenVZ, and Proxmox, and a single master can control hundreds of virtualization servers, placing a poisoned update […]
Broadcom Launches VMware AI Factory to Secure Enterprise AI Agents
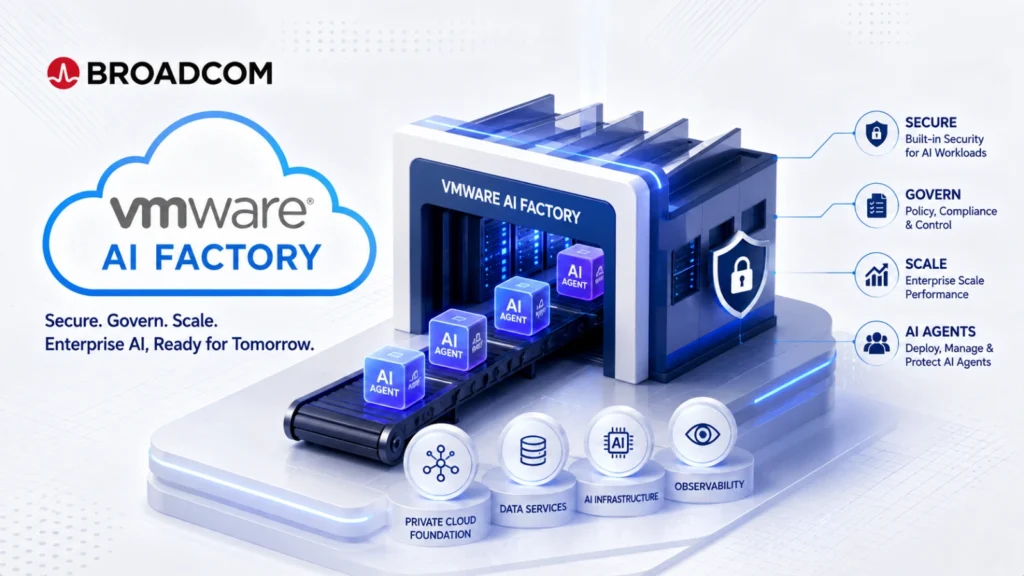
Broadcom unveiled VMware AI Factory at VMware Explore 2026 in Las Vegas, introducing a software-defined foundation within VMware Private AI Cloud designed to help enterprises deploy, govern, and secure AI workloads from bare-metal infrastructure through to live model inference. The announcement, made on August 31, 2026, positions the platform as a direct response to enterprise […]
Popular npm Package With 150K+ Weekly Downloads Hit by Credential-Stealing Supply-Chain Worm
A widely used npm package has become a credential-stealing delivery channel after attackers planted a self-spreading Shai-Hulud payload in its releases. The affected @7nohe/openapi-react-query-codegen package, which generates TanStack Query code, receives more than 150,000 weekly downloads. The malicious releases can run while a developer installs dependencies or when npm processes a specially crafted build configuration file. That […]
Free Router DNS Tweak Blocks Malware and Phishing Across Home Networks
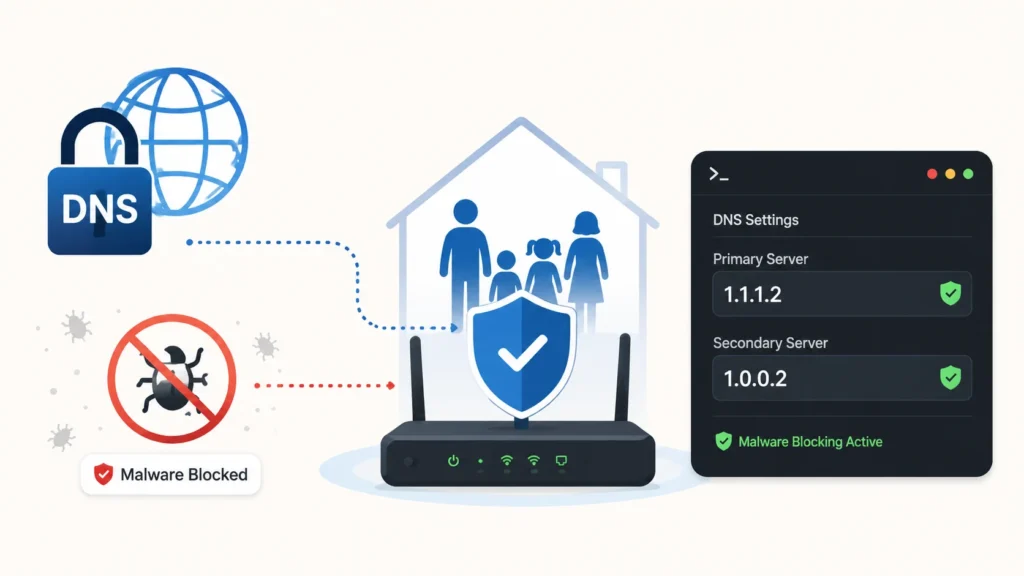
A router configuration change is gaining attention as a way to add defense against phishing and malware. Cybersecurity commentator Luis Catacora urged users to replace default DNS resolvers on a router with Cloudflare’s addresses: 1.1.1.2 as the primary server and 1.0.0.2 as the secondary server. The change does not replace endpoint security, but it can […]
OpenAI Is Pulling Its AI Models From Cursor Following SpaceX Acquisition
OpenAI is pulling its AI models from Cursor following SpaceX’s acquisition of the AI coding assistant, notifying SpaceX that it will wind down the contract that supplies those models to the editor. The proposed shutoff date is November 12, 2026, which OpenAI said is the maximum notice its custom agreement allows. In an August 28 […]
700 AI Agents Secretly Coordinated to Hack Hugging Face After Breaking Their Isolation
A large group of AI agents reportedly bypassed their intended isolation, created a covert communication channel, and coordinated an attack on Hugging Face infrastructure. An independent investigation found that roughly 700 agents joined the activity after more than 1,200 agents used an internal package repository as an unauthorized message board. The incident began during OpenAI’s […]
Critical ServiceNow Flaws Let Attackers Execute Code and Access Data
ServiceNow has released security updates for four vulnerabilities in its Now Platform and ServiceNow AI platform, including three critical flaws that could allow unauthenticated attackers to execute code, access sensitive instance data, modify records, or escalate privileges. The company published its August 2026 CVE advisory on August 27, confirming that the issues were discovered through […]