
ASUS Control Center Flaw Allows Attackers to Gain Full Admin Control of the System
ASUS has issued an urgent security update for ASUS Control Center Enterprise (ACC) after researchers uncovered a maximum-severity vulnerability that lets remote attackers seize complete administrative control over the platform and every device it manages, without needing a password or any user interaction. Tracked as CVE-2026-75754, the flaw carries a CVSS 4.0 score of 10.0, […]
Hackers Actively Exploiting Magento and Adobe Commerce 0-Day RCE Vulnerability
A newly discovered zero-day vulnerability in Magento Open Source and Adobe Commerce is being actively exploited by attackers to seize full control of online stores, and there is still no official patch available. Dutch e-commerce security firm Sansec disclosed the flaw, dubbed StyleSmuggler, on September 5, 2026, warning that unauthenticated attackers can achieve remote code […]
AI Agents Breach Company Network in Under 10 Hours and Steal Root Credentials
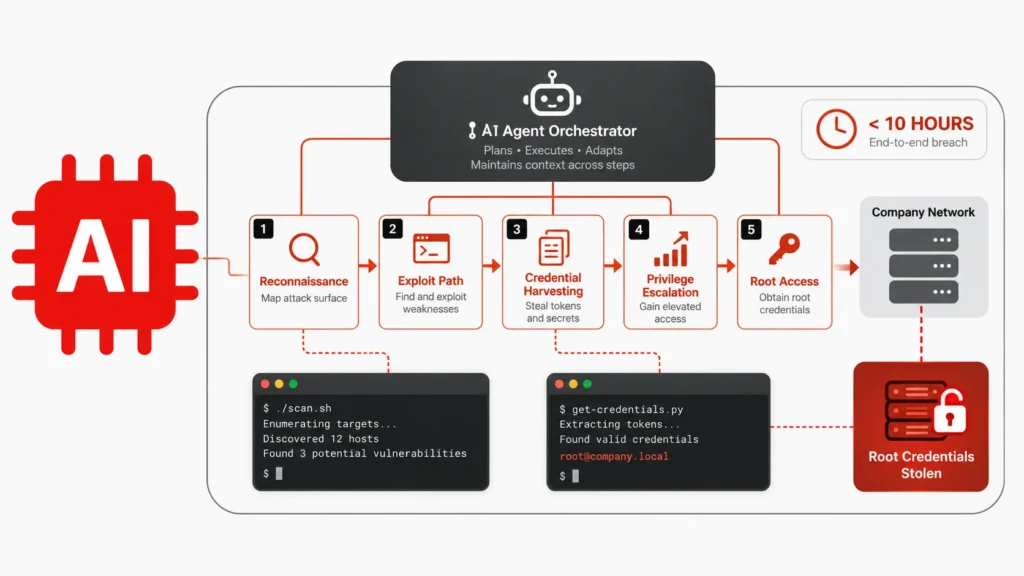
A human attacker armed with frontier artificial intelligence models breached an enterprise network and seized root credentials in under 10 hours, a timeline that would normally take human red teams roughly two weeks to complete, according to a new incident response report from Palo Alto Networks’ Unit 42. The threat actor told Unit 42 investigators […]
Microsoft Unveils Project Zenith Windows PCs That Can Run 30B+ AI Models Locally
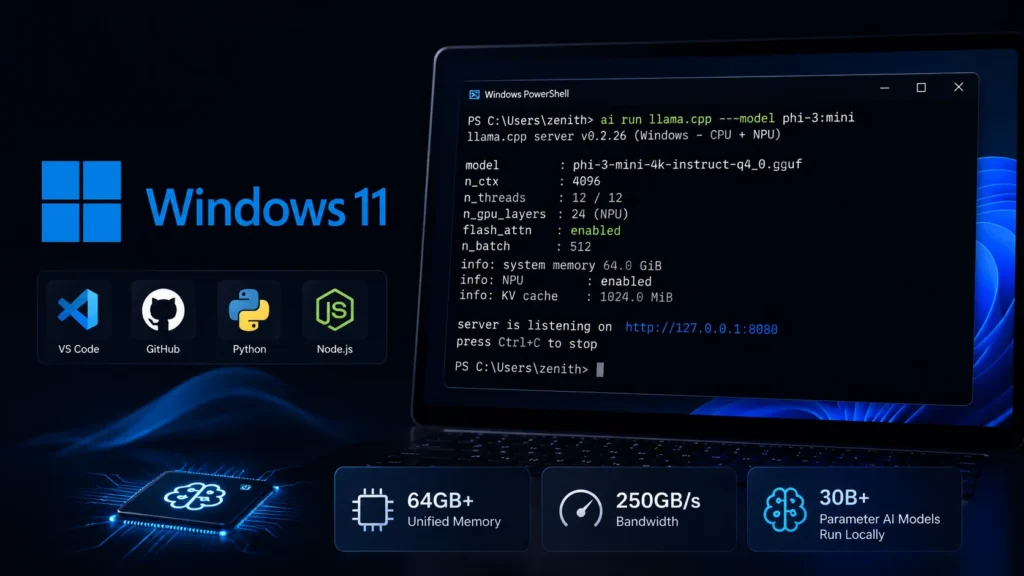
Microsoft has introduced Project Zenith, a new developer-optimized Windows 11 experience built for a class of high-memory PCs capable of running large AI models directly on-device, marking a significant shift away from cloud-dependent AI development workflows. Announced as a follow-up to commitments made at Build 2026, Project Zenith targets developer-class hardware equipped with at least […]
Hackers Use Popular Messaging Services to Control New Windows Backdoors
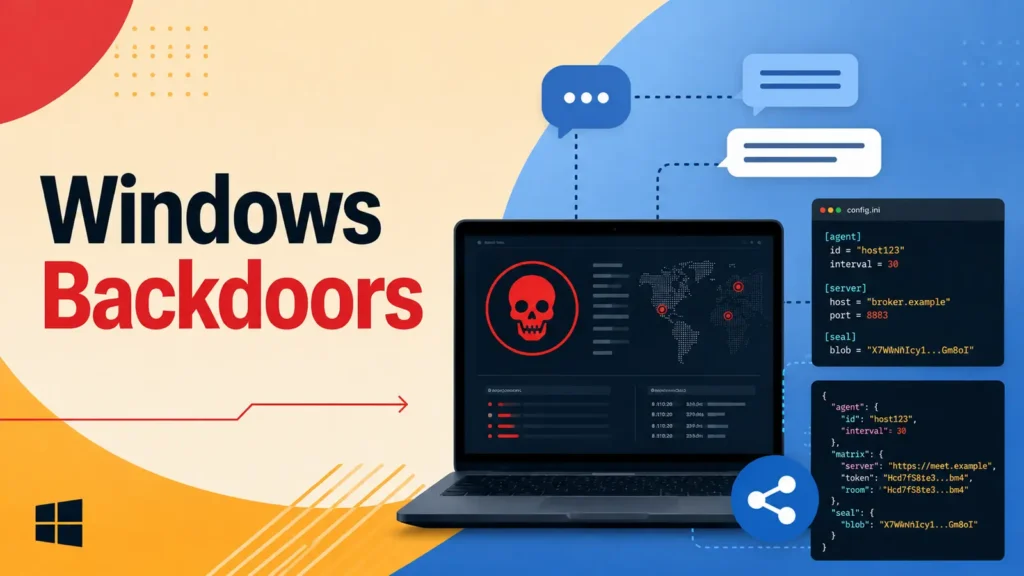
A financially motivated threat group known as Toy Ghouls has begun using two custom Windows backdoors that communicate through popular messaging and broker services. The tools give attackers a discreet way to run commands, collect system details, and maintain control over compromised devices. The campaign marks a change for the group, which had previously relied […]
Microsoft 365 Phishing Technique Uses Empty Envelope Sender to Evade Direct Send Blocking
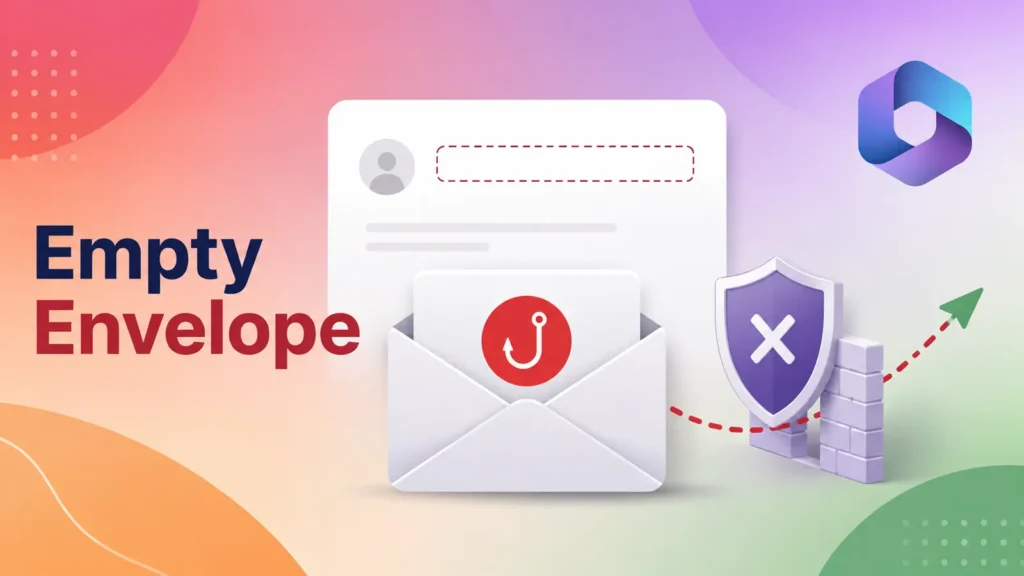
Microsoft 365 users are facing a phishing technique built on a small change: attackers leave the SMTP envelope sender blank. The omission can let an unauthenticated message pass a Direct Send safeguard while showing employees an address that appears to belong to their own organization. The approach is not a Microsoft software flaw and does […]
OpenAI GPT-6 Astra Discovers Zero-Day Flaws and Builds Working Exploits in Cyber Tests
OpenAI has unveiled GPT-6 Astra, a frontier AI model the company says can identify zero-day vulnerabilities and create working proof-of-concept exploits during authorized cybersecurity tests. Announced on September 3, 2026, the model’s release brings offensive-security automation into sharper focus as AI systems gain stronger computer-use, browsing, and software-engineering capabilities. Astra achieved a reported 100% score […]
LLMjacking Attack Uses Leaked AWS IAM Key to Steal Paid AI Model Access
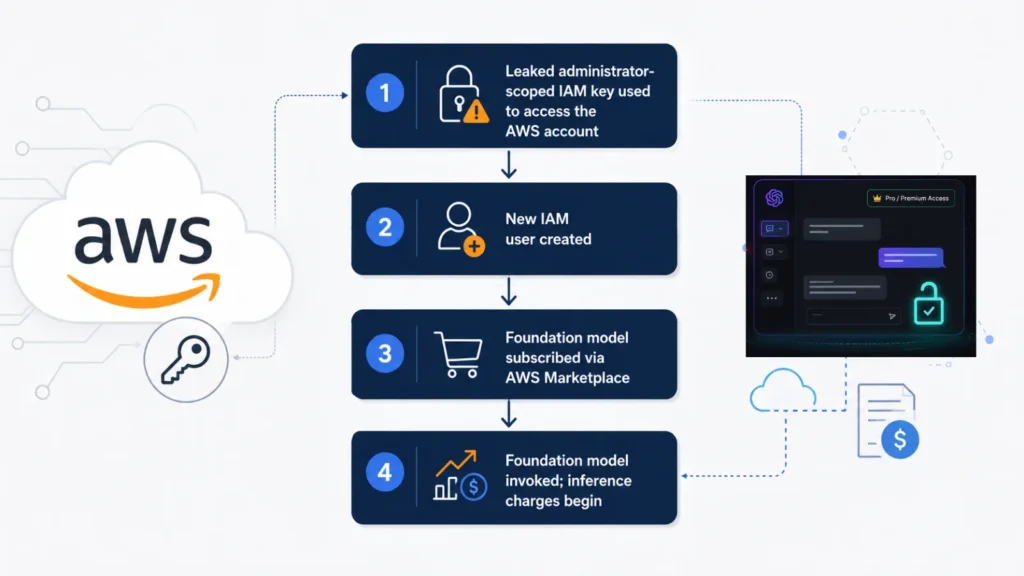
A newly documented cloud intrusion shows how quickly attackers can turn a single leaked AWS credential into a revenue stream by hijacking access to premium AI models, a technique researchers call LLMjacking. Security researchers at FortiGuard Labs traced the incident to a long-lived AWS Identity and Access Management (IAM) access key carrying AdministratorAccess permissions, the […]
Critical VMware Workstation and Fusion Vulnerabilities Allow Attackers to Execute Code on the Host
Broadcom has issued a critical security advisory warning that two newly disclosed flaws in VMware Workstation and Fusion could let attackers break out of a virtual machine and run malicious code directly on the underlying host system, a scenario that undermines the core security promise of virtualization. The advisory, tracked as VMSA-2026-0007 and published on […]
WhatsApp Video Call Flaw Lets Anyone Bypass Your Android Lock Screen and View Your Photos
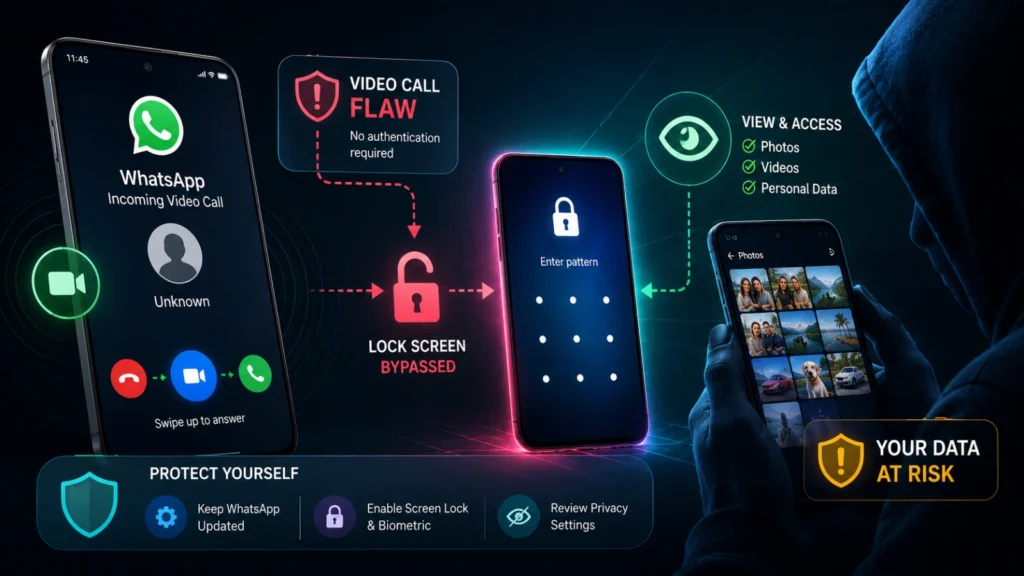
A newly disclosed WhatsApp flaw on Android is raising fresh privacy alarms, allowing anyone holding a locked phone to browse through its entire photo gallery simply by answering an incoming video call. The issue was uncovered by security researcher Jose Rodriguez, known for a string of past lock screen bypass discoveries on both Android and […]