
Scammers Use WhatsApp Groups to Coordinate Millions in Victim Trades and Pump Real Stocks
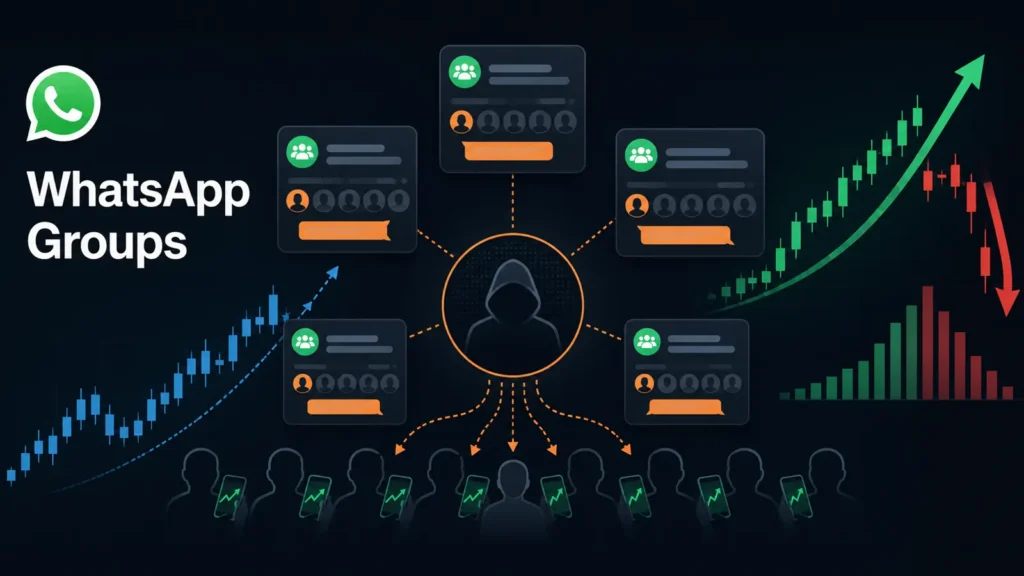
Scammers are using WhatsApp groups to turn ordinary investors into an unwitting buying force. The operation does not need a hacked trading account or a stolen card. Instead, it persuades people to place real trades through legitimate brokerages, then leaves them carrying the losses when the price collapses. The campaigns pair short-lived deepfake advertisements with […]
DOJ Charges 17 Iranian Hackers in IRGC-Linked Campaign That Stole 31.5TB of Research Data
The U.S. Department of Justice has unsealed a 14-count superseding indictment against 17 alleged members of the Iran-based Mabna Institute, accusing them of conducting a long-running cyber espionage campaign that stole at least 31.5TB of research data and intellectual property. According to the indictment, the operation began around 2013 and continued through at least December […]
CRLF-Powered Desync Lets Attackers Poison CDN Cache and Serve XSS to Live Users
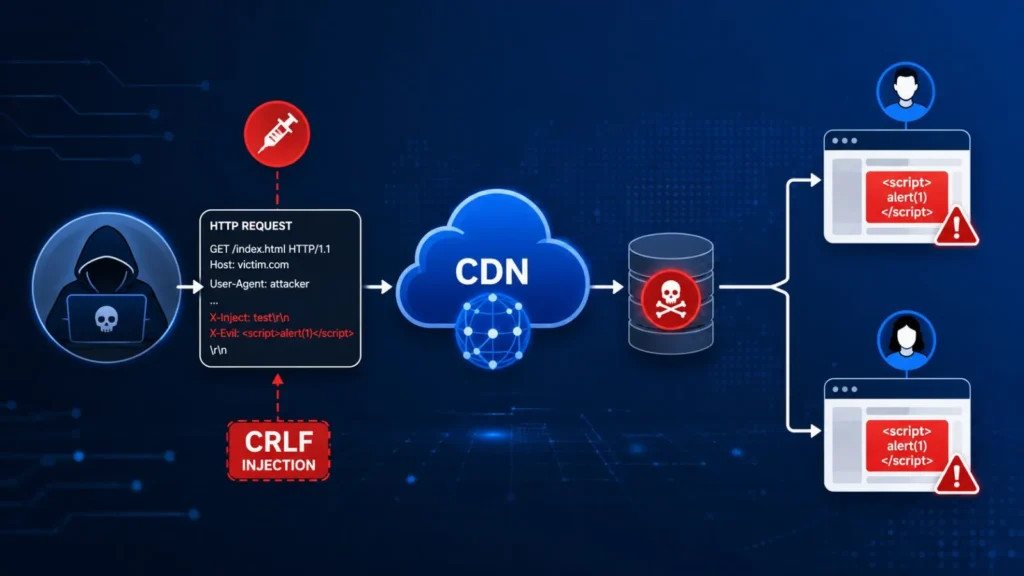
A limited CRLF injection flaw can be escalated into a severe HTTP desynchronization attack, poisoning CDN caches and delivering XSS payloads to users on legitimate websites. The attack, called CRLF-Powered Desync, begins when an application incorrectly handles encoded carriage return and line feed characters, commonly represented as %0d%0a. These characters mark new lines in HTTP messages. […]
Claude AI Finds SAML Security Flaws That Can Let Attackers Take Over Accounts
Security researchers have used Anthropic’s Claude AI to uncover serious flaws in Security Assertion Markup Language (SAML) implementations that could allow attackers to bypass authentication and take over user accounts. The findings highlight the persistent security risks created by XML signature processing, inconsistent parser behavior, and custom SAML code. A researcher at Oblique Security built […]
Critical Citrix NetScaler Flaw Lets Remote Attackers Bypass Authentication Without Credentials
Cloud Software Group has issued a critical security bulletin warning customers of two serious vulnerabilities affecting NetScaler ADC (formerly Citrix ADC) and NetScaler Gateway (formerly Citrix Gateway). Tracked as CVE-2026-19489 and CVE-2026-19490, the flaws could allow attackers to trigger denial-of-service conditions or bypass authentication entirely on unpatched appliances, putting enterprise remote access infrastructure at significant […]
BeyondTrust Windows EPM Vulnerabilities Allows Attackers to Escalate Privileges
BeyondTrust has disclosed two high-severity vulnerabilities in its Endpoint Privilege Management (EPM) product for Windows that could allow attackers with local access to elevate privileges or bypass anti-tamper controls. Tracked as CVE-2026-40144 and CVE-2026-40145, the flaws affect all versions of BeyondTrust Endpoint Privilege Management (Windows Deployment) released before version 26.1.2. The company published the advisory, […]
Critical Microsoft Copilot CoSnitch Vulnerability Lets Attackers Steal Sensitive Data With One Click
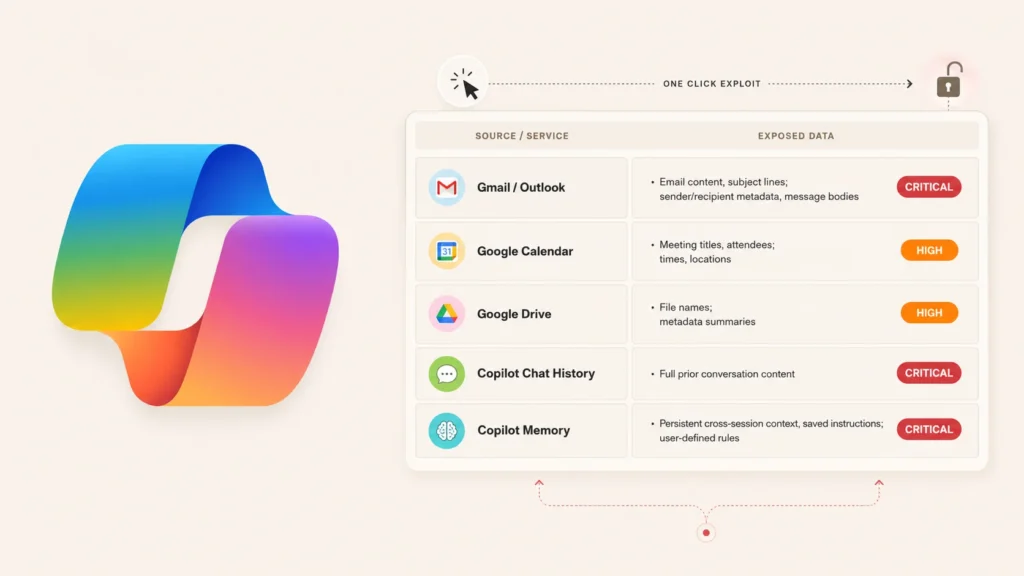
A critical vulnerability in Microsoft Copilot Personal, tracked as CVE-2026-24301 and nicknamed CoSnitch, lets attackers silently siphon sensitive data from a victim’s connected accounts with nothing more than a single click on a malicious link. The flaw discovered by Varonis Threat Labs has already been patched by Microsoft as of August 18, 2026, but the […]
CISA Warns Medusa Ransomware Hackers Steal Data, Kill Security Tools, and Encrypt Entire Networks
The Cybersecurity and Infrastructure Security Agency (CISA), the Federal Bureau of Investigation (FBI), and the U.S. Department of Health and Human Services (HHS) have jointly released an updated security advisory warning that Medusa ransomware threat actors are actively infiltrating enterprise environments, disabling security tools, exfiltrating sensitive files, and encrypting entire networks. The updated alert (AA25-071A) […]
CISA Warns of Ray-Project Ray Code Injection Vulnerability Exploited in Attacks
CISA has added a critical Ray-Project Ray vulnerability, tracked as CVE-2025-62593, to its Known Exploited Vulnerabilities catalog after confirming exploitation in the wild. The flaw can allow remote code execution on systems where vulnerable Ray development environments are running. Ray is an open-source distributed computing framework widely used by Python developers and AI teams for […]
Pokémon Center Confirms Data Breach Hackers Stole Customers Personal Data
Pokémon Center has begun notifying customers in the United Kingdom and Germany that their personal information was exposed in a third-party data breach, and that the incident has forced the company to cancel a batch of pending orders. The retailer confirmed that the exposure did not originate on its own website but instead traced back […]