
Pokémon Center Confirms Data Breach Hackers Stole Customers Personal Data
Pokémon Center has begun notifying customers in the United Kingdom and Germany that their personal information was exposed in a third-party data breach, and that the incident has forced the company to cancel a batch of pending orders. The retailer confirmed that the exposure did not originate on its own website but instead traced back […]
Microsoft SCCM Vulnerability Chained to Execute Malicious Code Remotely
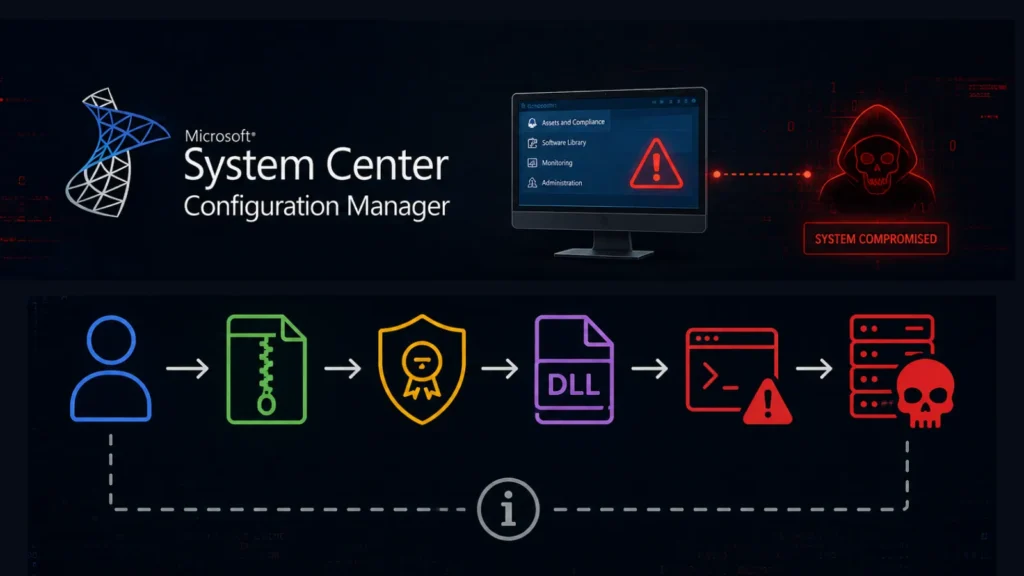
Security researchers have disclosed a serious attack chain affecting Microsoft System Center Configuration Manager, commonly known as SCCM or Configuration Manager. The flaws could allow an attacker to execute malicious code remotely on an SCCM primary site server, potentially taking control of an organization’s managed Windows environment. The attack is especially concerning because a standard […]
Apple Screen Sharing Vulnerability Exploited to Execute Command as Root
A newly disclosed logic flaw in macOS Screen Sharing shows how a feature meant only to grant screen-viewing access can be twisted into a path for full root command execution. The issue, tracked as CVE-2026-43760, affects the screensharingd service and its file-copy helpers, SSFileCopySender and SSFileCopyReceiver, on macOS systems where Screen Sharing or Remote Management […]
Cyber Security Weekly Newsletter Outlook RCE, Palo Alto, Cisco 0-day and Windows 0-Day Flaws +20 Stories
This week’s roundup covers a record-setting Microsoft Patch Tuesday, an actively exploited Cisco firewall zero-day, a Lazarus-linked Windows kernel bug, and critical flaws across TP-Link, Palo Alto Networks, Fortinet, and VMware — plus a first-of-its-kind autonomous AI agent “hack” and a DEF CON in-flight Wi-Fi scare. Ransomware & Threat Actor Campaigns Gunra Ransomware Exploits Fortinet […]
Hackers Started to Exploit Critical SAP Commerce Cloud, Still No Public PoC
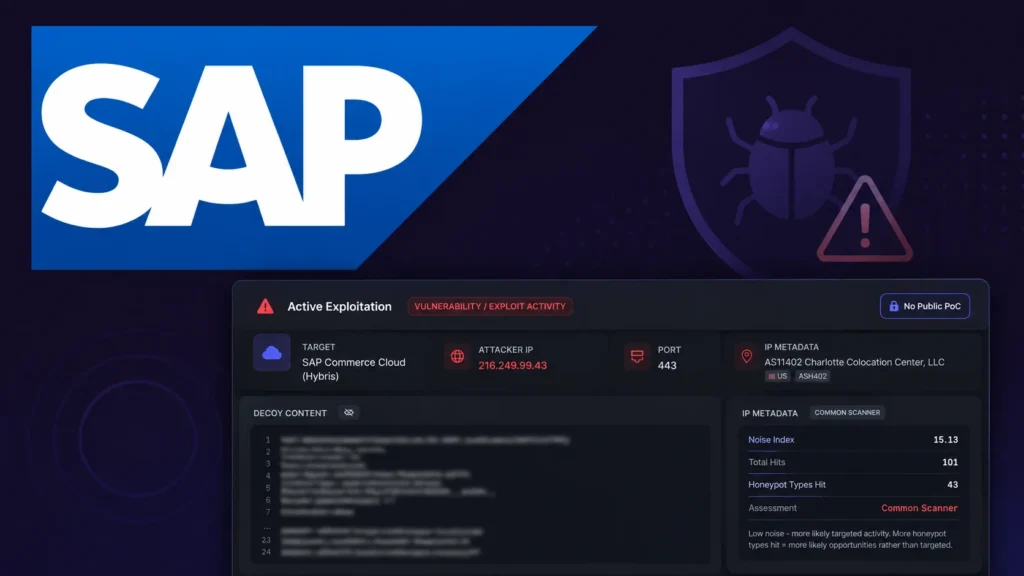
Threat actors have begun actively probing and attempting to exploit a maximum-severity flaw in SAP Commerce Cloud, just three days after official security fixes were released. Defused honeypot telemetry captured the first wave of unauthenticated remote-execution traffic circulating across the web, despite the complete absence of a public proof of concept. Tracked as CVE-2026-58231, the […]
Shell Investigating Data Breach Following Cl0p Ransomware Group Claim
Multinational energy giant Shell has launched an active investigation after the notorious Cl0p ransomware syndicate claimed responsibility for exfiltrating sensitive internal data. Security researchers and enterprise defenders are closely monitoring the situation as forensic teams work to assess the legitimacy and operational scope of the cyberattack. The extortion collective listed Shell on its dark web […]
Microsoft to Make Passkeys Default in Entra ID and Retires SMS and Voice Authentication
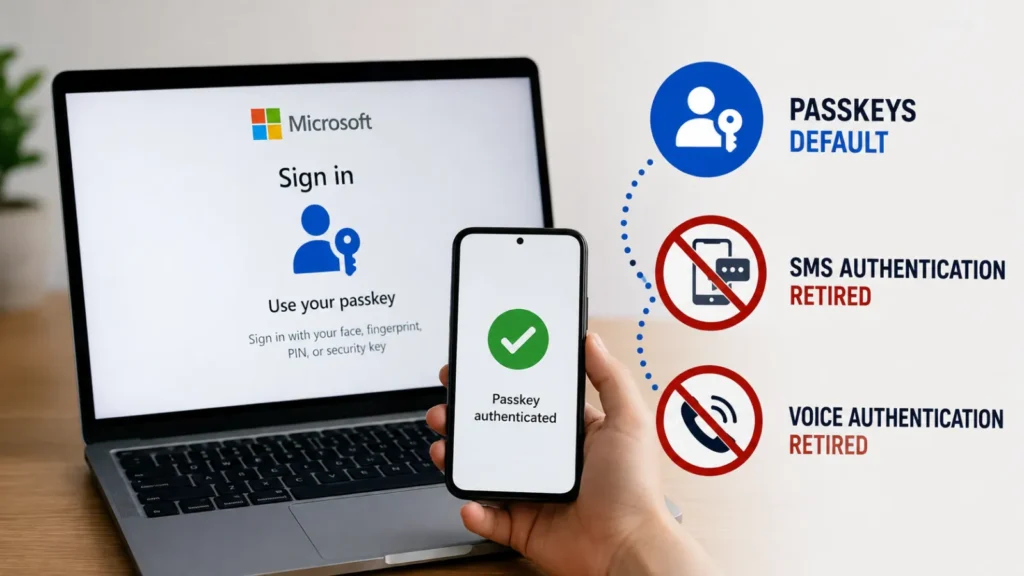
Microsoft will make passkeys the default authentication experience in Microsoft Entra ID as part of a broader move away from phishing-prone sign-in methods. The company will also retire Microsoft-provided SMS and voice authentication for multifactor authentication, pushing organizations toward phishing-resistant credentials. Beginning September 1, 2026, users currently enabled for SMS or voice authentication will be […]
Multiple TP-Link Vulnerabilities Allow Attackers to Bypass Authentication and Escalate Privileges
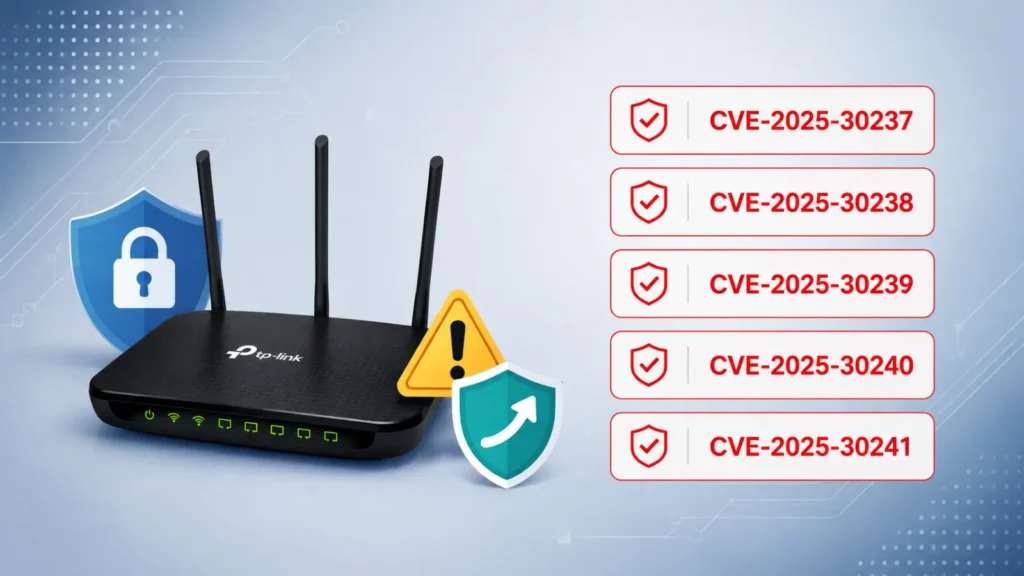
TP-Link has disclosed multiple high-severity vulnerabilities affecting ISP-managed Aginet networking products, including mesh systems, routers, PON devices, and xDSL modems. The flaws could allow attackers with network access to bypass authentication, escalate privileges, steal sensitive information, read device files, and execute operating system commands. The security advisory, last updated on August 10, 2026, tracks the […]
DCRat Campaign Hides Malware Archive Inside SVG Using HTML Smuggling
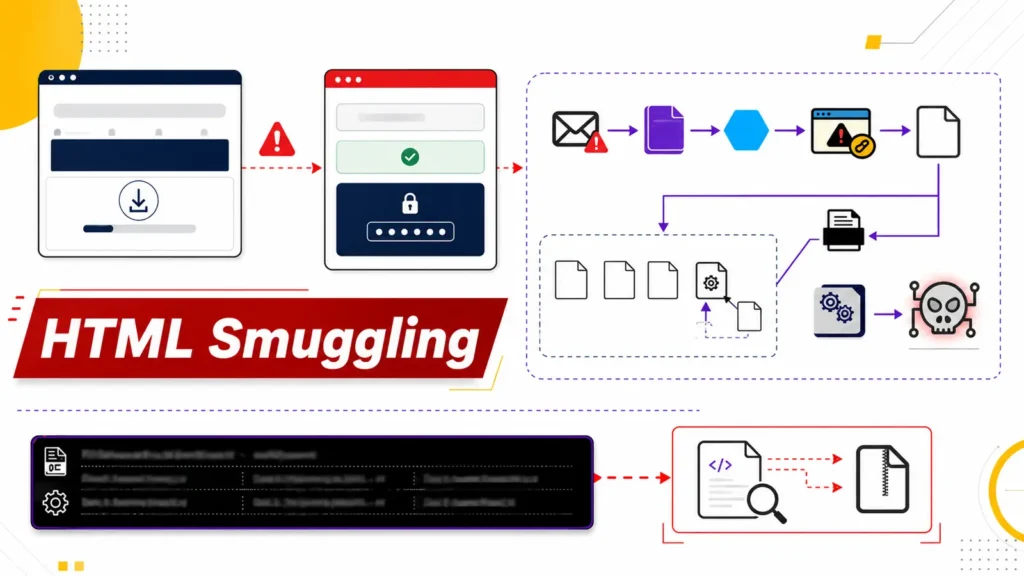
A new DCRat campaign is using a familiar image format to hide a dangerous malware archive. The operation begins with phishing emails that pose as legal notifications and urge recipients to open an attached SVG file. The attachment looks harmless because SVG files are commonly used for graphics. In this case, however, the file contains […]
1 Tbps DDoS Attacks Become the New Normal as Cloudflare Reports Record H1 Activity
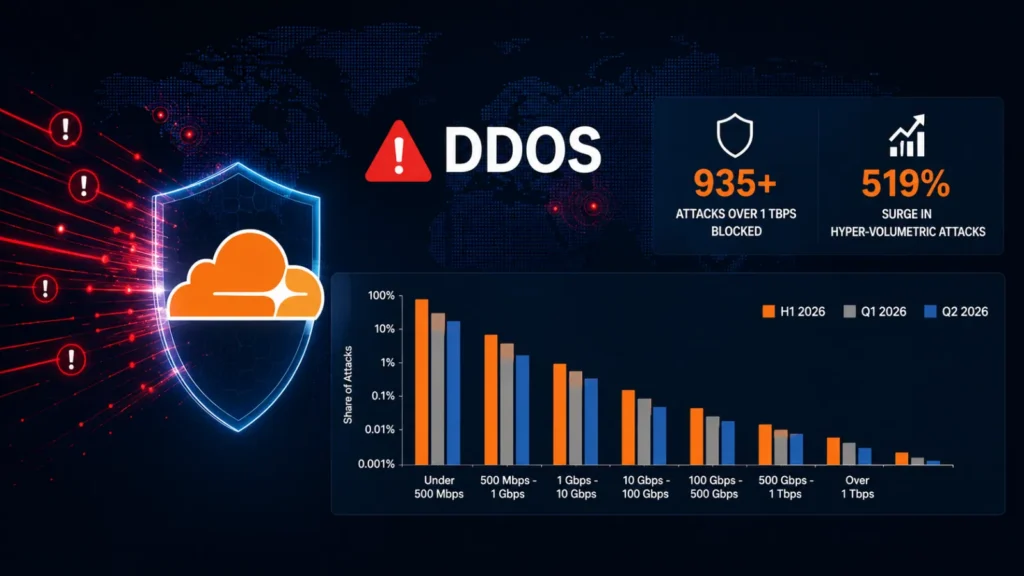
Cloudflare has reported a sharp rise in large-scale distributed denial-of-service attacks during the first half of 2026, blocking 935 network-layer attacks exceeding 1 terabit per second. The company said hyper-volumetric attacks grew 519% between the first and second quarters, showing that attackers are increasingly capable of delivering extreme traffic floods at a rapid pace. The […]