
Critical Linux Kernel Flaw Lets Attackers Escape Virtual Machines and Take Control of Hosts
A critical flaw in the Linux kernel may allow an attacker-controlled virtual machine (VM) to breach its isolation boundary and impact the host system. This vulnerability, identified as CVE-2026-99999 and referred to as PwnEscape by researcher Paulos Yibelo, originates from the Linux networking code rather than a specific hypervisor. Paulos Yibelo demonstrated a technique that […]
Burger King Japan Confirms Data Breach Exposing 11.18M User Records
Burger King Japan has confirmed a data breach that exposed about 11.18 million records linked to members of its official app. BK Japan, which operates the chain in Japan, said an outside party gained unauthorized access to the system used to manage app member information. The company disclosed the incident on October 15, 2026. According […]
CISA Warns of Hackers Exploiting Ivanti Connect Secure Zero-Day to Steal Credentials
CISA urged administrators to patch Ivanti Connect Secure appliances after attackers exploited CVE-2026-104935, a zero-day flaw that allows remote authentication bypass and command execution, enabling credential theft and data exfiltration. CISA issued its warning and added the flaw to its Known Exploited Vulnerabilities catalog on October 13, 2026. The warning covers Ivanti Connect Secure versions […]
Multiple Active Directory Vulnerabilities Let Attackers Bypass Security Feature Remotely
Microsoft has disclosed three Active Directory vulnerabilities that could let a remote attacker bypass a key security feature in Windows domain environments. The issues are tracked as CVE-2026-69982, CVE-2026-96252, and CVE-2026-108131, and administrators should review Microsoft’s Security Update Guide entries and deploy the available fixes as soon as possible. Active Directory is the central identity […]
Multiple NGINX Flaws Let Remote Attackers Crash Servers and Execute Malicious Code
F5 has disclosed three serious security flaws in NGINX Plus and NGINX Open Source that can let remote, unauthenticated attackers crash worker processes by sending crafted HTTP requests. In certain setups, the memory errors could also allow code execution, although F5 says that outcome requires Address Space Layout Randomization, known as ASLR, to be disabled […]
VirusTotal Integrates Threat Intelligence With ChatGPT for Malware Analysis
VirusTotal can now bring threat intelligence into ChatGPT through VirusTotal AI (VTAI), allowing users to investigate suspicious files, URLs, domains, and IP addresses within a conversation. The connection helps analysts retrieve existing reports and explain detection results while keeping the source, analysis date, and coverage visible. The integration uses Model Context Protocol (MCP), a standard […]
OpenAI Engineer Arrested for Planting Spyware Device in an Executive Conference Room
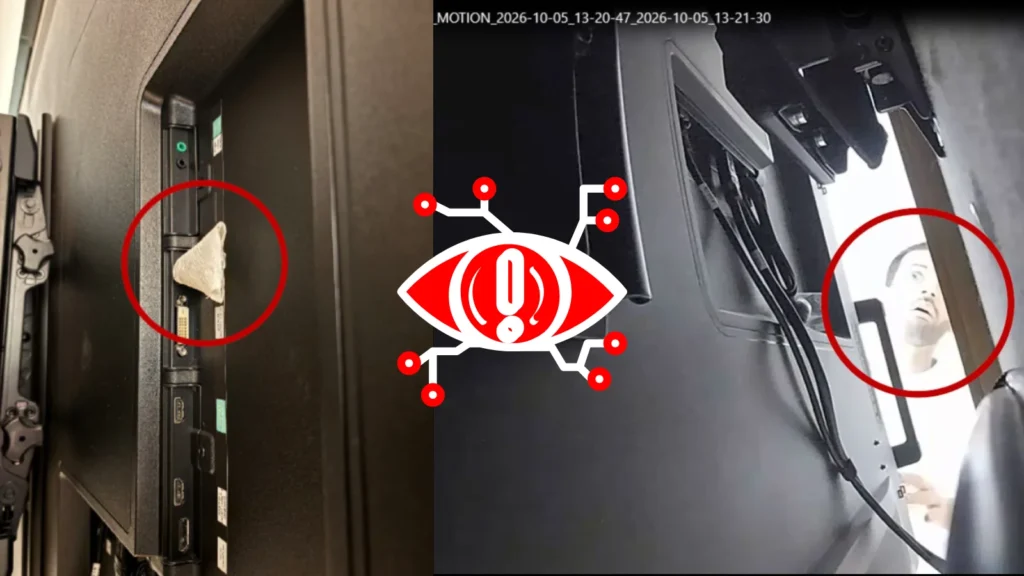
An OpenAI engineer has been arrested for allegedly hiding an audio recording device in an executive conference room at the company’s San Francisco offices. Abdulrahman Alfozan, 35, a Saudi national, was arrested on October 9, 2026, and appeared in federal court on October 13, according to the U.S. Department of Justice. Prosecutors charged him with […]
Microsoft Fixes 1,118 Vulnerabilities in October Patch Tuesday and Introduces New Risk Cohorts
Microsoft’s October 2026 Patch Tuesday briefing outlines 1,118 vulnerabilities across 15 risk groups, alongside a new approach designed to help security teams review large update releases. Called risk cohorts, these groups bring together flaws that require similar questions about an organization’s systems, users, and exposure. Microsoft’s accompanying document maps individual CVEs to these shared areas […]
Fake Web3 Accelerator Uses Malicious npm Packages to Target Crypto Founders
A fake Web3 accelerator called Apex has been using malicious npm packages to target cryptocurrency start-ups and founders with what appeared to be free AI credits, coding tools, smart-contract audits, investment access, and invitations to in-person events. Behind the polished Web3 pitch, the operation delivered malware for macOS and Windows, exposed AI-agent data to attacker-run […]
Yandex Data Center Outage Disrupts Access to Cloud Files Following Drone Attack
Yandex has confirmed a major service outage after drone attacks damaged three data centers in Russia, leaving some users unable to access cloud files. Two facilities stopped operating, while a third lost part of its infrastructure. The disruption affected Yandex Disk users and businesses running services on Yandex Cloud across the platform. The first attack […]