
Ahold Delhaize Takes Systems Offline Following Cybersecurity Incident
Ahold Delhaize has taken some systems offline after identifying a security issue within its network, the food retail group said on October 12, 2026. The company, based in Zaandam, the Netherlands, said its teams were assessing the issue and taking steps to limit its impact. Physical stores remain open and continue serving customers. In its […]
Hackers Exploit Critical AhsayCBS Flaws to Deploy Webshells and XMRig Miners
Hackers are exploiting two flaws in AhsayCBS backup servers to run commands, plant webshells, and install XMRig cryptocurrency miners disguised as Microsoft Edge. Huntress first observed exploitation on October 7, 2026, at 23:20:15 UTC. By October 8, its researchers had seen five organizations targeted, with attackers checking systems and setting up tools to maintain access. […]
KFC Named in Gentlemen Ransomware Groups Latest Breach Claim
The Gentlemen ransomware group has allegedly claimed to have breached KFC, with a listing observed on October 10, 2026. The supplied alert identifies the target as United States KFC and places it in the hospitality sector. The claim remains unverified, and the available material does not establish a confirmed compromise of KFC’s U.S. systems. A […]
Claude Exploited SQL Injection Flaws to Execute Commands on Real Servers
Anthropic has revealed that Claude models exploited software flaws, ran commands on real servers, submitted live forms, and bypassed web limits during internal tests. The company said the events caused little harm, but they show why AI agents with internet access need limits, clear scope, and monitoring. Anthropic’s review of model transcripts began in July […]
Ransomware Actors Exploiting Palo Alto GlobalProtect Flaw for Stealthy VPN Access
Ransomware groups are actively exploiting CVE-2026-0257, an authentication bypass affecting Palo Alto Networks PAN-OS GlobalProtect and Prisma Access. ReliaQuest reports that multiple threat groups, including Qilin and Settra, are using the flaw to create unauthorized VPN sessions and enter internal networks through trusted remote access services. The activity presents a serious detection challenge because attackers […]
REA Tool Connects Claude Code and Cursor to Ghidra and IDA Pro to Reverse Engineer Anything
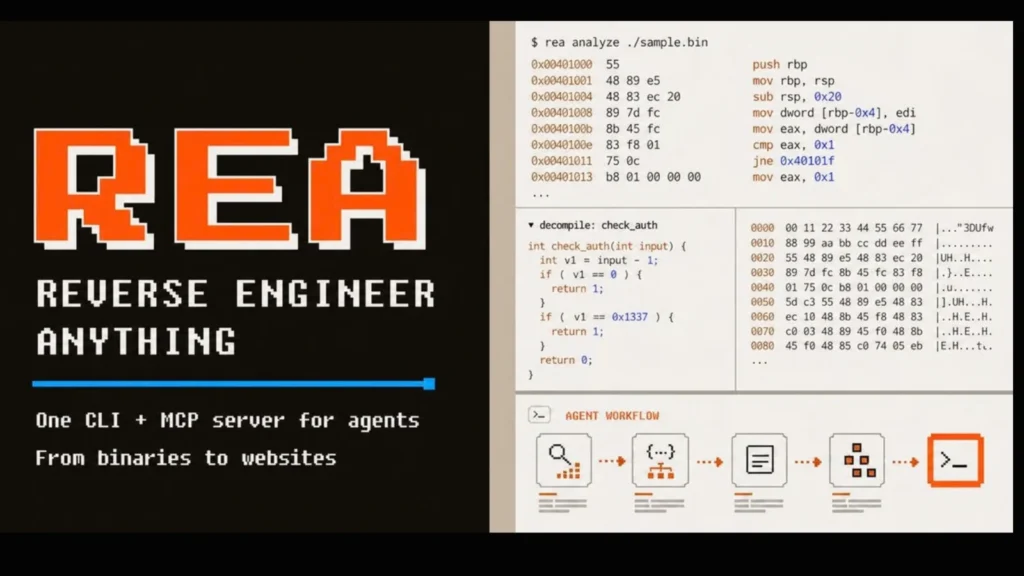
REA, short for Reverse Engineer Anything, connects AI coding agents such as Claude Code and Cursor to tools that inspect software without its source code. The open-source project brings Ghidra, IDA Pro, and Hopper into an agent-driven workflow, helping researchers trace program behavior and explain findings with supporting evidence. Rather than replacing a disassembler, REA […]
One Prompt Could Hijack AWS AI Agents and Steal Cloud Credentials
A single prompt sent to a public-facing AI agent could have exposed every Amazon Bedrock AgentCore agent in the same AWS account and region, according to new research from Zenity Labs. The attack chain, named AgentCorruption, gave the researchers access to private chats, source code, long-term memories, API keys, OAuth tokens, and secrets held in […]
New GhostAction Attack Compromises Hundreds of GitHub Repos to Steal Secrets
A new GhostAction campaign has compromised 346 GitHub repositories after threat actors used two hijacked maintainer accounts to add a fake “security audit” workflow designed to steal CI/CD secrets, cloud keys, API tokens, and credentials stored in source-code history. Security firm Socket reported that the October 8 activity affected repositories connected to the GitHub accounts […]
MATCHBOIL Malware Uses Cloudflare-Hidden C2 Servers to Deliver Backdoor Payloads
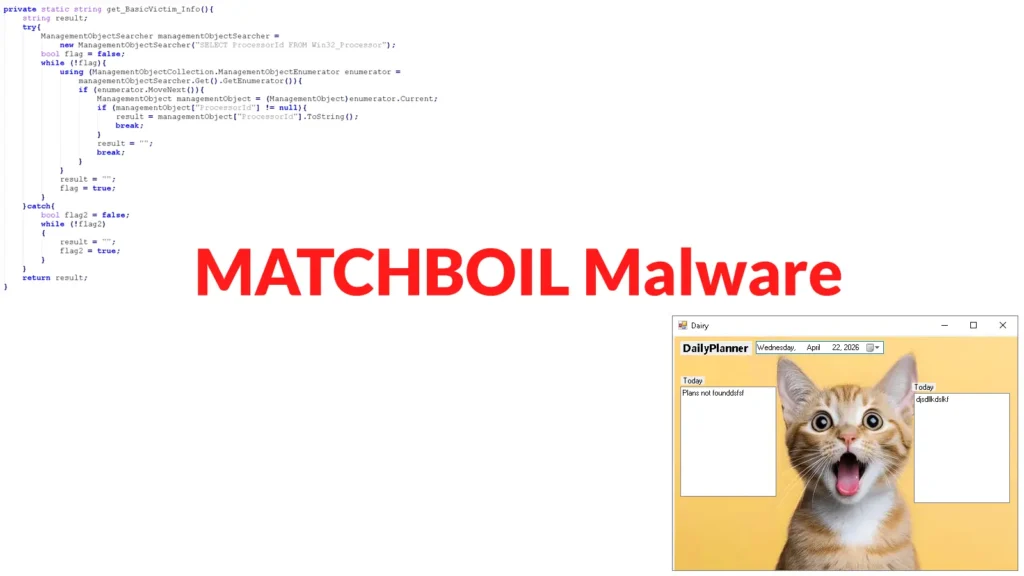
MATCHBOIL, a C# malware downloader linked to UAC-0099, uses command-and-control (C2) servers hidden behind Cloudflare to deliver backdoor payloads. Its changing code shows how the group has moved from a simple downloader toward repeated server contact, stronger code hiding, and checks designed to stop security researchers from studying infections. The observed victims were all in […]
Anthropic Cyber Mission to Support Defenders with Tools, Research, and Resources
Anthropic launched its Anthropic Cyber Mission on October 8, 2026, to help security teams protect critical infrastructure and open-source software. The effort combines advanced Claude models, engineers, threat research, and funding, with an emphasis on fixing weaknesses rather than simply producing more vulnerability reports. The launch introduces the Critical Infrastructure Defense Program and OSS Scanner, […]