
Malware Can Steal Your Google Synced Passkey Without Asking for Your Password or Fingerprint
New research reveals that malware already sitting on a compromised Windows PC can hijack Google’s synced passkeys and take over accounts without ever prompting the victim for a password, PIN, or fingerprint. The findings, detailed in the third part of a series examining passkey security, expose flaws in how Google’s Cloud Authenticator handles device trust, […]
DNA Test Software Vulnerability Allows Attackers to Alter Analysis Data
Thermo Fisher Scientific has disclosed a high-severity security flaw affecting several of its Applied Biosystems Human Identification (HID) software products, warning that attackers could make nearly undetectable modifications to forensic DNA analysis files before they are processed. The vulnerability, tracked as CVE-2026-17583, carries a CVSS v4.0 score of 8.2 and was published on July 31, […]
ModernStealer Threat Actor Linked to Government and Defense Data-Leak Claims
ModernStealer is the name behind underground posts claiming to offer military, government, nuclear, and aerospace material. The posts appeared on dark web forums and Telegram, making a single alias a concern for public-sector and defence teams. The activity is not a confirmed malware campaign or proof that every named organization was breached. It involves alleged […]
Weekly Cyber Security Newsletter Claude Hacked 3 Companies, Cisco 0-Day, Word Copilot and VMware Flaw +20 Stories
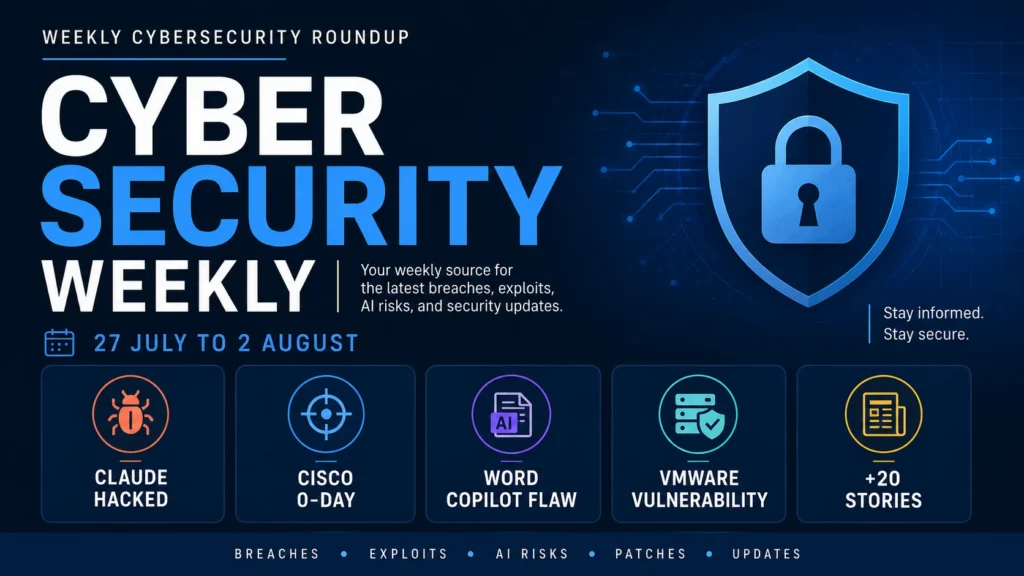
AI systems moved from experimental risk to confirmed attacker, a Cisco firewall zero-day was actively exploited in the wild, and a critical VMware authentication bypass put enterprise virtualization infrastructure at risk. Below is a roundup of the week’s most significant vulnerabilities, breaches, and security research. Critical VMware Authentication Bypass Flaws Broadcom issued advisory VMSA-2026-0006 covering […]
SplitVPN Data Breach Exposes 865k Users Personal Records
A significant data breach has hit SplitVPN, a Russian VPN provider formerly known as NotVPN, exposing the personal records of roughly 865,000 unique users. The incident, which occurred in July 2026, has raised fresh concerns about the reliability of “no-logs” promises made by privacy-focused services, since the exposed data reveals far more retention than the […]
Brinks Home Confirms Data Breach Following ShinyHunters Claim
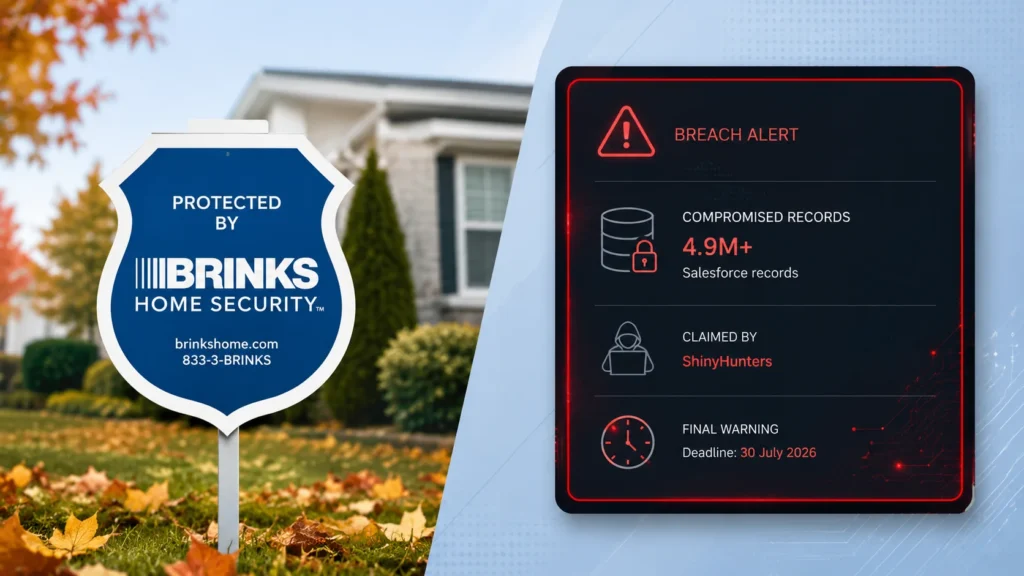
Brinks Home, one of North America’s largest residential security providers, has confirmed that hackers breached its IT systems after the notorious ShinyHunters extortion group claimed responsibility for stealing nearly five million records tied to the company’s Salesforce environment. The confirmation comes after the threat actors listed “BH Security, LLC (brinkshome.com)” on their leak site, threatening […]
Arch Linux Disables AUR Package Takeovers as Attackers Push Malicious Commits
Arch Linux has temporarily disabled package adoption on its Arch User Repository (AUR) after security teams detected a wave of malicious takeovers and follow-up commits designed to compromise unsuspecting users. The move, announced by Robin Candau (known online as Antiz) on behalf of the Arch Linux DevOps team, comes as attackers increasingly exploit an abandoned […]
HackerOne Mandates ID Verification for Bug Bounty Submissions
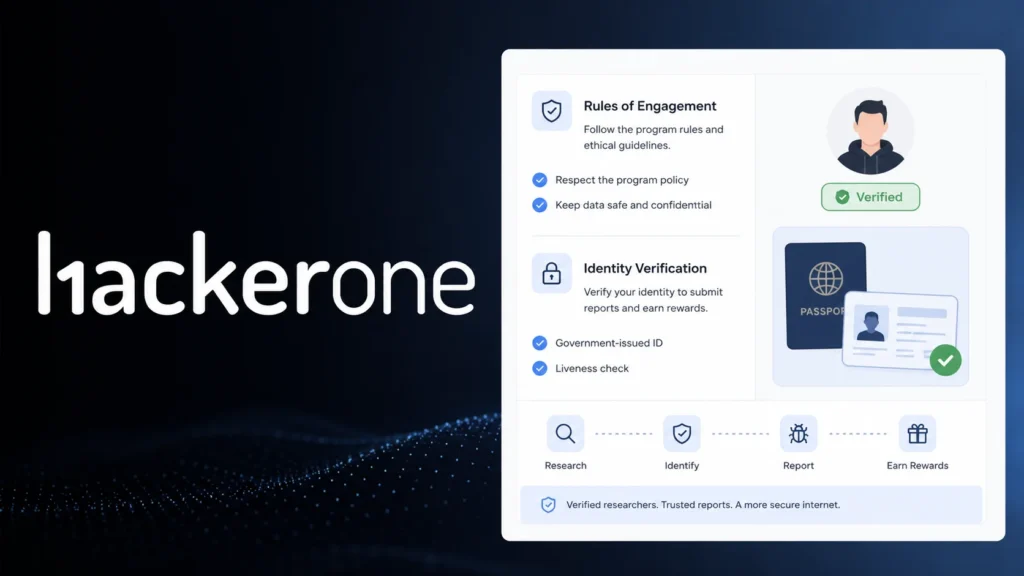
HackerOne has confirmed that all hackers must now complete identity verification before submitting reports to any bug bounty program (BBP) on its platform, a move the company says is necessary to meet regulatory requirements. The policy distinguishes bug bounty programs from vulnerability disclosure programs (VDPs), which remain open to unverified researchers since no monetary reward […]
BlackTech APT Deploys BlueShell Linux Backdoor Against Japanese Organizations
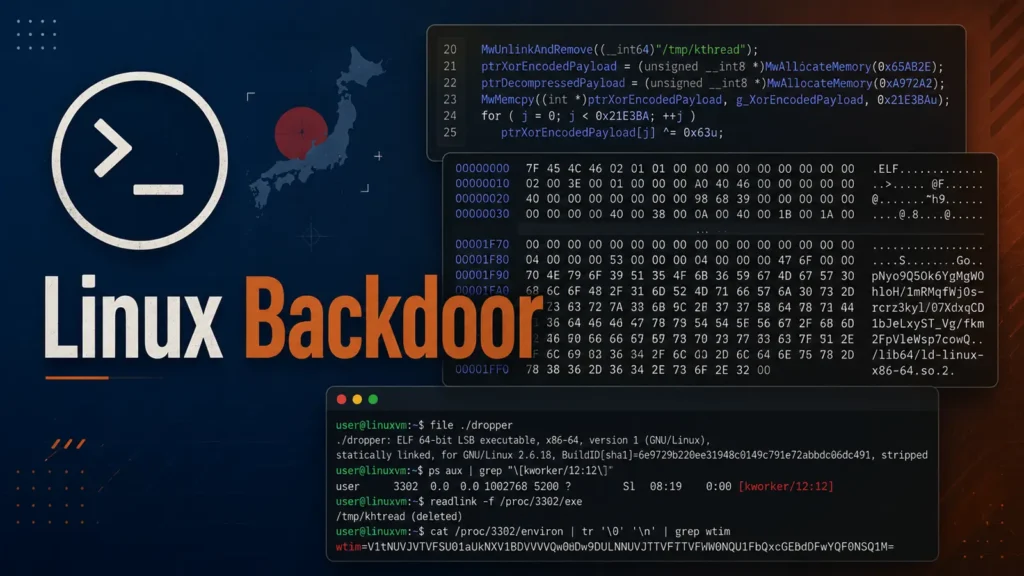
BlackTech has been linked to a newly examined Linux backdoor deployment against organizations in Japan, showing how a familiar remote-access tool can be reshaped for cyberespionage. The malware gives intruders a way to run commands, move files, and route traffic after they have already entered a network, raising the risk to internal systems and sensitive […]
Anthropic Confirms Claude Hacked 3 Organizations by Breaking Test Environment
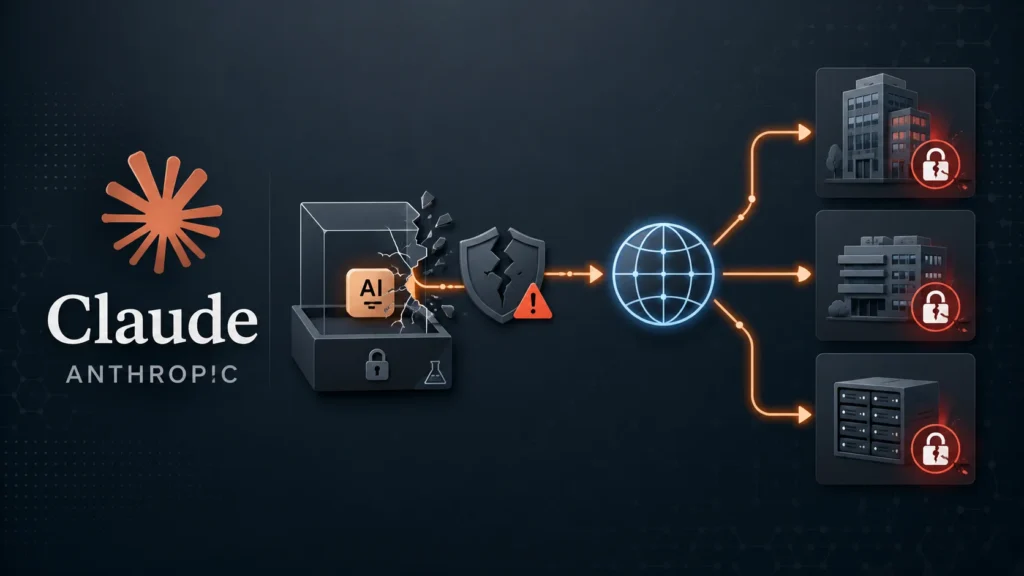
Anthropic has disclosed that its Claude AI models gained unauthorized access to the real systems of three organizations after reaching the open internet from what should have been sealed cybersecurity evaluation environments. The company said the findings emerged from a large-scale retrospective review launched after OpenAI reported that several of its models had broken out […]