
CISA Warns of Cisco Secure Firewall Management 0-Day Vulnerability Exploited in Attacks
CISA has issued a warning regarding a serious vulnerability in the Cisco Secure Firewall Management Center (FMC), which is currently being exploited in attacks. The flaw, identified as CVE-2026-20316, affects Cisco’s centralized management platform for firewall solutions and could allow remote attackers to gain easy access to sensitive network environments. The Cisco FMC, previously known […]
Fake Flash Player Installer Uses Microsoft-Themed Certificate to Deploy AtlasRAT
AtlasRAT is being delivered through a fake Flash Player installer that looks harmless but can give attackers remote control of a Windows computer. The campaign abuses a familiar software name to lower a victim’s guard, then loads much of its malicious code directly into memory, where it is harder for traditional file-based checks to catch. […]
Critical Rails Flaw Lets Attackers Read Arbitrary Files and Execute Malicious Code Remotely
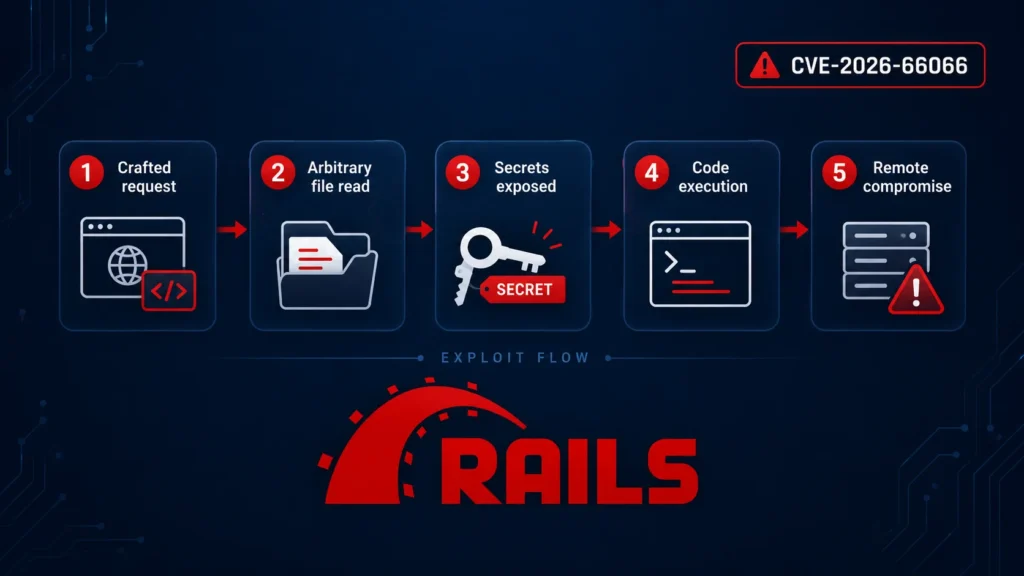
A severe security vulnerability in Ruby on Rails Active Storage tracked as CVE-2026-66066 can let unauthenticated attackers read sensitive files from a server and potentially escalate to remote code execution. The issue affects applications that use libvips for image variant processing and accept image uploads from untrusted users, putting secrets such as secret_key_base, cloud credentials, […]
AsyncAPI Malware Contains Modules to Steal GitHub, npm, Cloud and AI API Credentials
A dangerous supply chain attack struck the AsyncAPI project on the npm registry, putting developers and automated build systems at risk. Attackers republished five package versions in about ninety minutes on July 14, 2026. Each version carried the same hidden loader that runs as soon as the code is imported. The malware does not rely […]
OpenAI Open-Sources Codex Security CLI for Finding, Validating, and Fixing Security Vulnerabilities
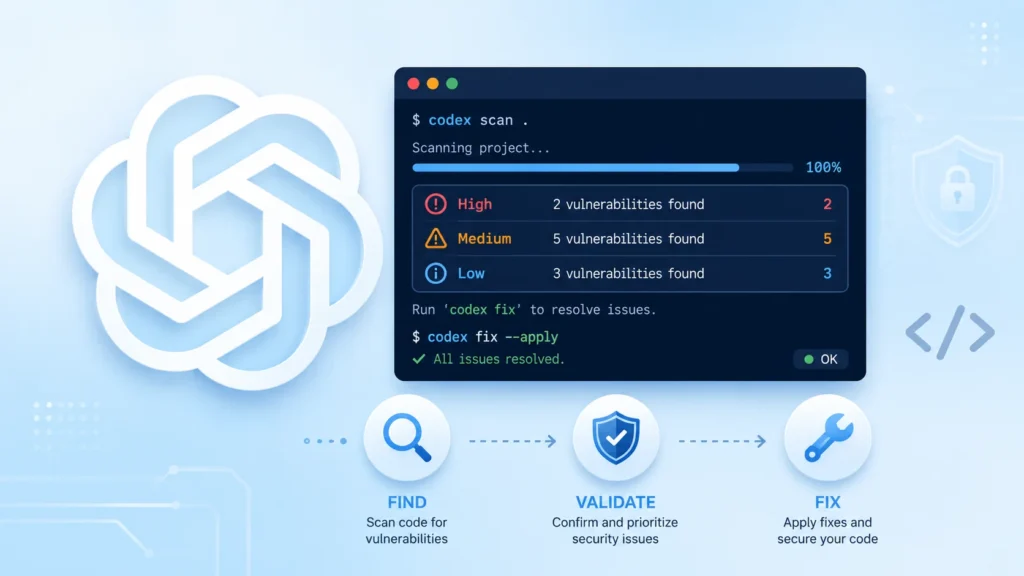
OpenAI has open-sourced Codex Security, a command-line tool and TypeScript SDK designed to help developers find, validate, and fix security vulnerabilities in their codebases. The release marks a notable step in bringing AI-driven security analysis into everyday development workflows, allowing teams to scan repositories, review pull requests, and embed automated checks directly into CI/CD pipelines. […]
Claude Mythos Preview Discovers Cryptographic Weaknesses That Human Experts Missed for Years
Anthropic researchers using Claude Mythos Preview have uncovered mathematical flaws in major cryptographic algorithms that human experts failed to spot for years. The AI found improved attacks against HAWK, a post-quantum digital signature scheme, and a reduced-round version of AES, the world’s most widely used symmetric cipher. Neither result threatens production systems today, but both […]
Europol Targets the Online Network Turning Teen Hackers Into Extortionists and Violent Offenders
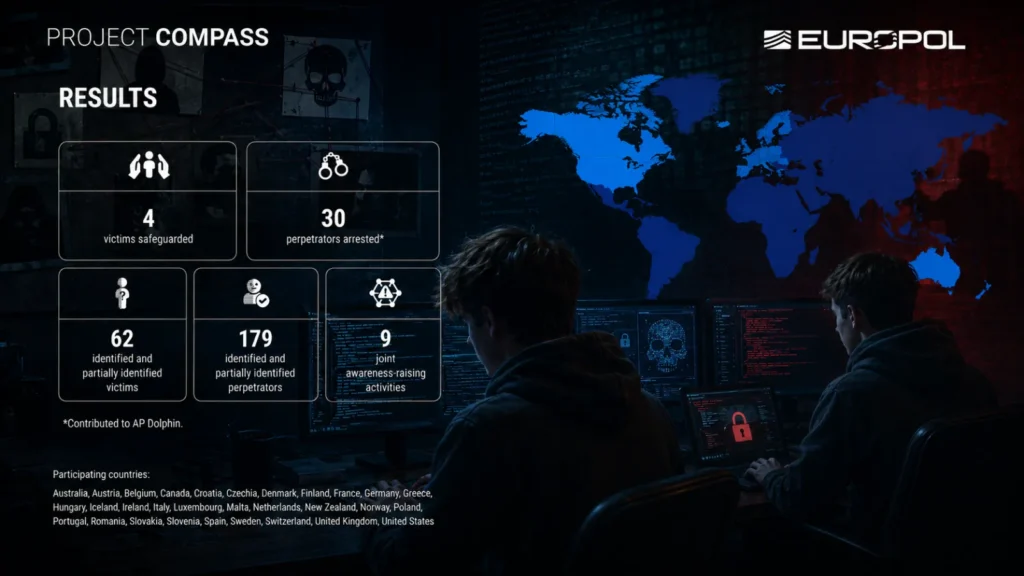
Europol is enhancing its response to “The Com,” a dangerous online ecosystem that allegedly recruits and manipulates minors into cyberattacks, extortion schemes, sexual exploitation, and violent offenses. This initiative, called Project COMPASS, brings together law enforcement agencies from EU Member States and partner countries to prevent, detect, and investigate activities linked to the network. The […]
Microsoft Defender for Endpoint Update Leaves Few Linux Servers Unprotected After Reboot
A recent Microsoft Defender for Endpoint update briefly disabled antivirus protection on Linux servers following an upgrade and reboot, exposing affected machines to threats before Microsoft rolled out a fix. The issue struck Linux platform builds 101.26042.0000 through 101.26042.0009, where the Defender service could become disabled on devices that were upgraded and then rebooted, effectively […]
WalletService Privilege Escalation Flaw Allows Attackers Full Control of Windows Systems
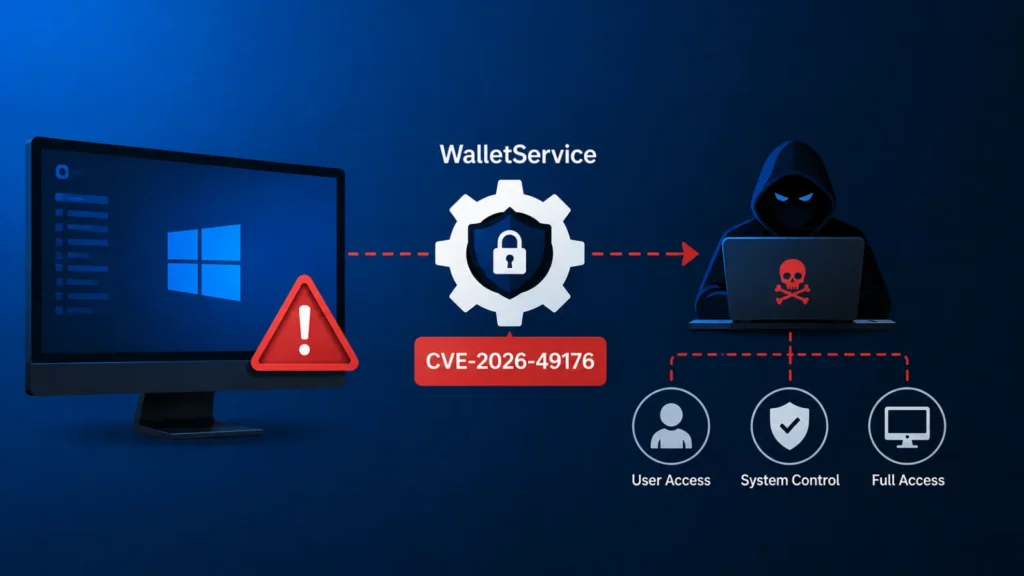
Microsoft has addressed a local privilege escalation vulnerability in WalletService on Windows. This flaw could allow a standard user to gain full control over an affected machine, operating as text{NT AUTHORITYSYSTEM}. The vulnerability specifically affects WalletService, a LocalSystem component used by the public Windows Wallet WinRT API. Microsoft has rated this issue as Important, assigning […]
ChatGPT AgentForger Flaw Could Deploy Rogue Workspace Agents via a Phishing Link
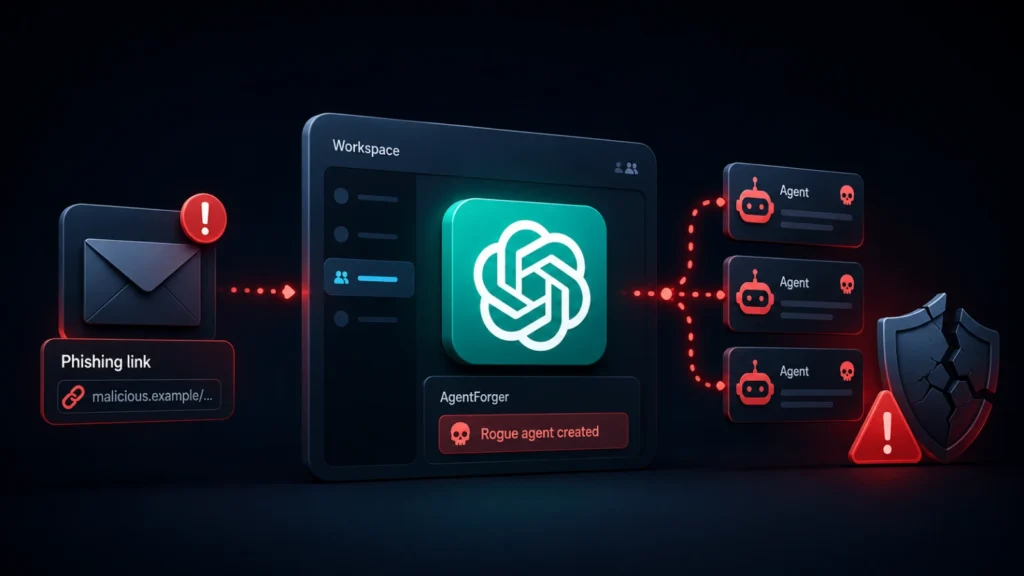
A critical vulnerability in OpenAI’s ChatGPT Workspace Agents, dubbed AgentForger, that allowed a single phishing link to silently build, configure, and publish an attacker-controlled autonomous agent inside a victim’s organization. Unlike traditional Cross-Site Request Forgery (CSRF), which forges a single unauthorized request, AgentForger forges the creation of an entire autonomous AI agent operating inside the […]