
Citrix Secure Access and Endpoint Client for Windows Vulnerability Enables Privilege Escalation
Cloud Software Group has disclosed two security vulnerabilities affecting Citrix Secure Access Client for Windows and Citrix Endpoint Analysis Client for Windows, with one flaw allowing low-privileged attackers to gain full SYSTEM access on affected machines. The more severe issue, tracked as CVE-2026-53565, carries a CVSS v4.0 base score of 8.5 and stems from improper […]
New wp2shell RCE Vulnerability Hits Millions of WordPress Sites, Emergency Patch Released
A critical pre-authentication remote code execution (RCE) vulnerability dubbed “wp2shell” has been discovered in WordPress Core, putting an estimated 500 million+ websites at risk of full takeover by unauthenticated attackers. Security researcher Adam Kues of Searchlight Cyber’s Assetnote research team uncovered the flaw, which stems from a REST API batch-route confusion issue that leads to […]
OpenSSL HollowByte Vulnerability Lets Hackers Crash Servers With Just 11 Bytes
A newly disclosed vulnerability in OpenSSL, dubbed “HollowByte,” allows a remote, unauthenticated attacker to trigger a denial-of-service (DoS) condition using a malicious payload as small as 11 bytes. Discovered by the Okta Red Team, the flaw exploits how OpenSSL pre-allocates memory during the TLS handshake, forcing servers to reserve massive memory chunks before any authentication […]
Two Hackers Jailed for Hacking 148 TfL Systems, Forcing Password Reset for 27,000 Staff
Two young members of the Scattered Spider cybercrime group have been jailed for a 2024 attack that knocked out 148 Transport for London (TfL) systems, forced all 27,000 staff to reset passwords in person, and cost the organization about £29 million. On June 22, 2026, Thalha Jubair and Owen Flowers pleaded guilty to a cyberattack […]
Linus Torvalds Told Kernel Developers that Linux is Not Against AI projects
Linux creator Linus Torvalds has told kernel developers that the Linux project is not anti-AI, arguing that artificial intelligence and large language models should be judged on whether they provide practical technical value. He emphasized that developers will not be forced to use AI tools, but opposition should not prevent others from using them responsibly. […]
WhatsApp GhostPairing Lets Scammers Hijack Accounts Without Stealing Passwords
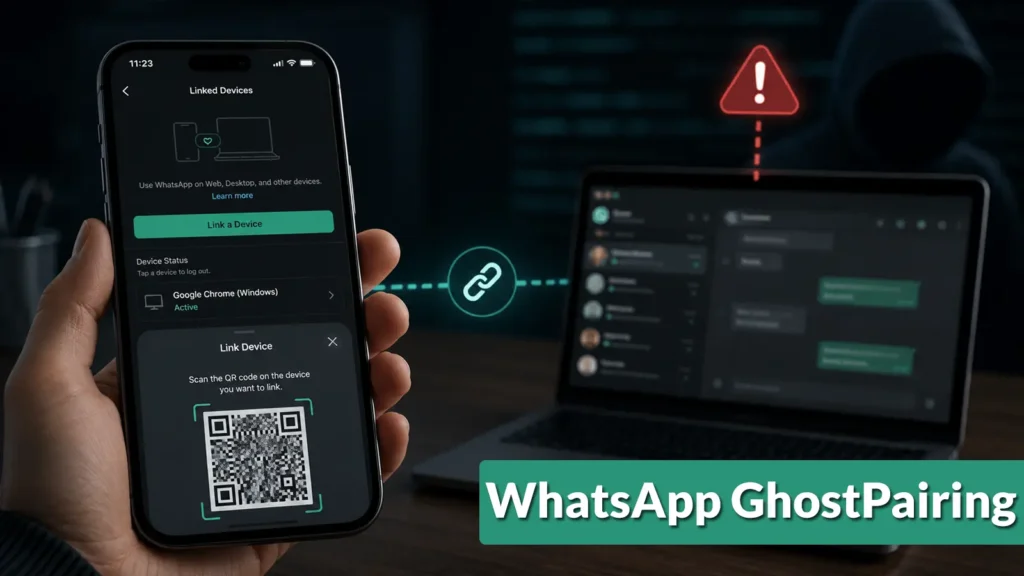
WhatsApp users are being targeted by a social-engineering technique called GhostPairing that can give scammers access to an account without requiring a password or one-time verification code. Instead of breaking into the service directly, the scam abuses WhatsApp’s legitimate device-linking feature and relies on a victim being persuaded to approve a new connected device. The […]
F5 Patches Multiple NGINX Vulnerabilities Enabling Heap Buffer Overflow and Code Execution Attacks
F5 has disclosed three high-severity vulnerabilities affecting NGINX Plus and NGINX Open Source, warning that unauthenticated attackers could exploit them to trigger memory corruption, crash worker processes, or, in the worst case, execute arbitrary code. The vulnerabilities, published on July 15, 2026, affect widely used NGINX components, including the Ingress Controller, Gateway Fabric, App Protect […]
Windows BitLocker 0Day Vulnerability Allows Hackers to Bypass Security Feature
A newly disclosed Windows BitLocker 0‑day vulnerability, tracked as CVE-2026-50661, exposes encrypted devices to physical attacks that can completely undermine Microsoft’s disk encryption guarantees. The flaw, classified as a security feature bypass, stems from a protection mechanism failure in BitLocker’s device encryption workflow, allowing an unauthorized attacker with hands-on access to a system to circumvent […]
CISA Warns of Decades-Old Cisco IOS Vulnerability Actively Exploited in Attacks
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has issued a warning that attackers are actively exploiting CVE-2008-4128, a cross-site request forgery (CSRF) vulnerability affecting Cisco IOS versions 12.4(12) and 12.4(4). This vulnerability was added to CISA’s Known Exploited Vulnerabilities Catalog on July 13, 2026, underscoring that even legacy networking flaws can pose security risks […]
New macOS Stealer Mimics Apples Crash Report Framework to Steal Browser Credentials
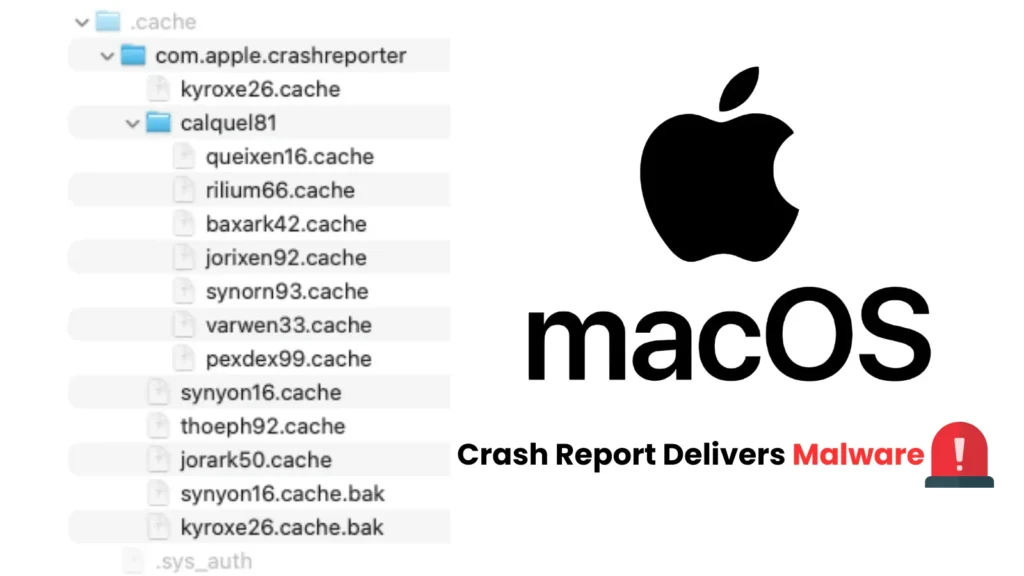
CrashStealer, a native C++ macOS infostealer that disguises itself as Apple’s built-in crash-reporting utility to harvest browser credentials, cryptocurrency wallets, password manager data, and keychain contents before encrypting and exfiltrating everything to a remote command-and-control server. Jamf first spotted a suspicious sample on VirusTotal in early May 2026 that appeared to be an infostealer still […]