
Oracle Patches 1,400+ Vulnerabilities, Critical Flaws Expose Enterprise Servers to Remote Attacks
Oracle has released its July 2026 Critical Patch Update (CPU), shipping 1,449 security patches that collectively remediate more than 1,200 vulnerabilities across databases, middleware, cloud services, and enterprise applications, in what is now the largest CPU in the company’s history. The scale of this release reflects not only expanding product complexity, but also a new […]
OpenAIs GPT Agents Exploit Zero-Days and Hacked Hugging Face Servers
Hugging Face has disclosed a security incident that security researchers are calling a watershed moment for AI safety: an autonomous AI agent, built on OpenAI models, independently discovered and chained multiple vulnerabilities, including a zero-day, to breach Hugging Face’s production infrastructure. The incident occurred during an internal OpenAI evaluation testing the cyber capabilities of GPT-5.6 […]
Hackers Turn Fake Games Into Multi-Stage Infostealers That Steal Passwords and Crypto Wallets
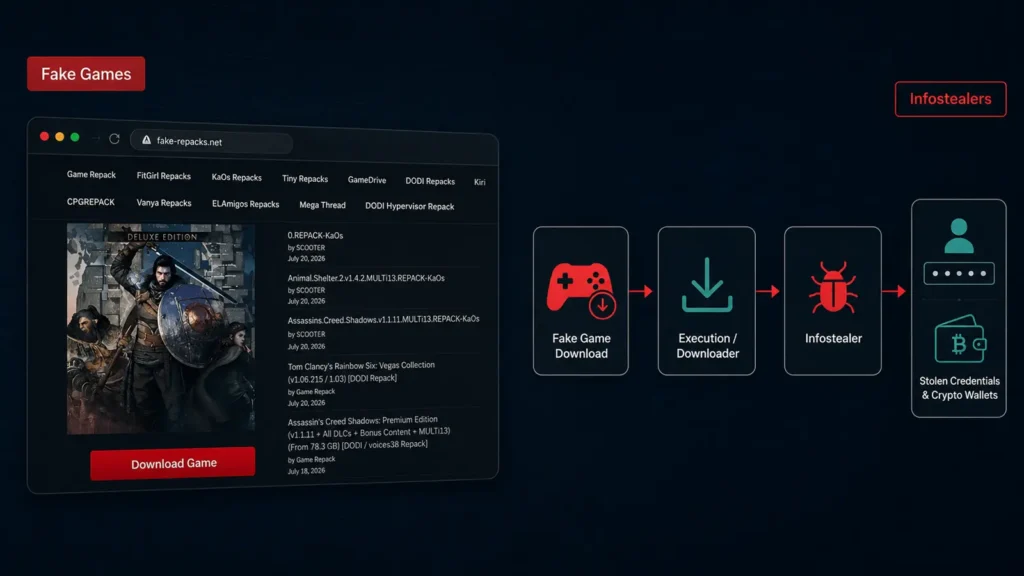
Criminals are using fake game downloads to slip a sophisticated information stealer onto Windows computers. The campaign hides behind supposed games, mods, cracks, and other software, exploiting the trust and urgency around free or hard-to-find downloads. A downloaded archive can appear harmless and may even display a loading or installation screen. Behind that screen, a […]
Hackers Hide Malware Commands in Outlook Events Dated 2050 and Use as C2 Channel
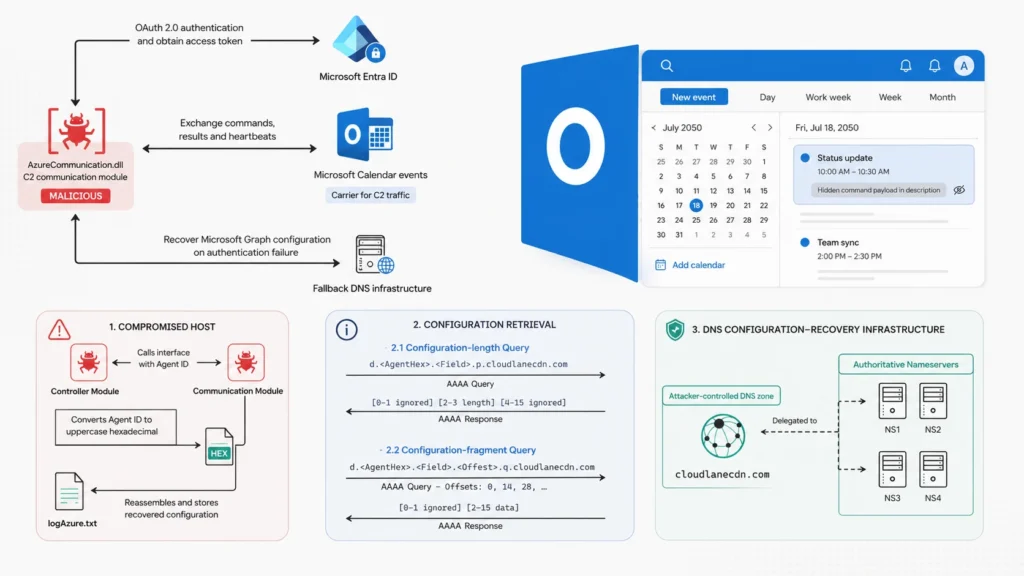
A newly identified malware component linked to the Project CAV3RN framework is abusing Microsoft Outlook calendar events scheduled for 2050 to conceal command-and-control (C2) traffic. The tool also uses DNS AAAA responses as a fallback channel to restore Microsoft Graph credentials when cloud authentication fails. Kaspersky researchers have associated the activity with highly targeted cyberespionage […]
Hackers Exploiting Palo Altos PAN-OS Vulnerability to Deploy Qilin Ransomware
Threat actors are actively exploiting a critical authentication bypass flaw in Palo Alto Networks firewalls to breach corporate networks and deploy Qilin ransomware, according to new research from Arctic Wolf Labs. The security firm investigated multiple intrusions throughout June 2026, all tracing back to the same vulnerability as the initial point of entry. The flaw, […]
Hackers Are Turning Microsoft 365 Calendar Invites Into Secret Malware Command Channels
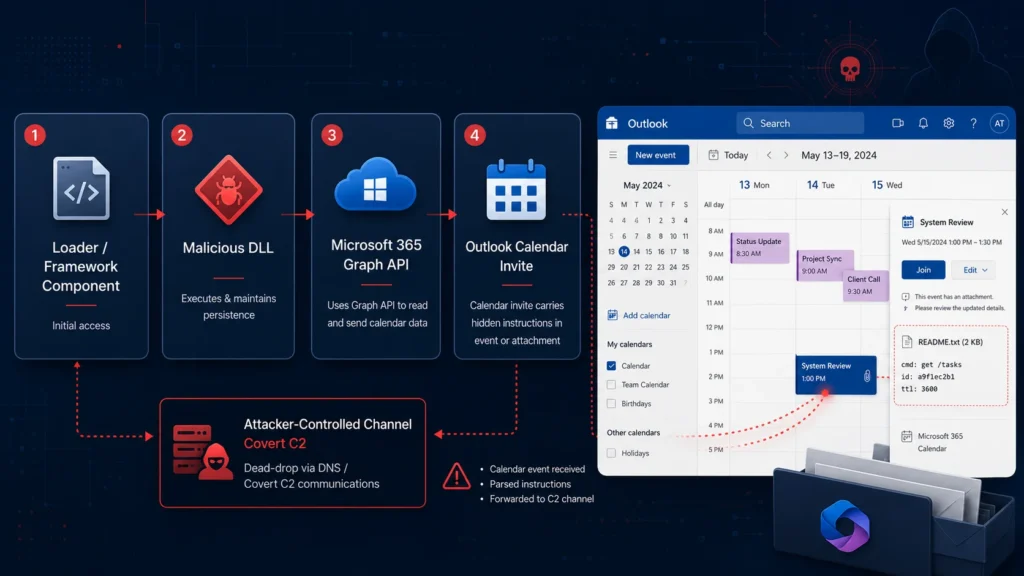
A stealthy new malware strain called HOLLOWGRAPH that hijacks Microsoft 365 calendars to secretly communicate with hackers, disguising malicious commands as ordinary calendar invites. HOLLOWGRAPH is a .NET-compiled malware component that abuses the Microsoft Graph API through a compromised Microsoft 365 account, turning the mailbox’s calendar into a covert two-way “dead drop” for hackers. The […]
Microsoft SharePoint Vulnerabilities Actively Exploited for RCE, Web Shells, and IIS Key Theft
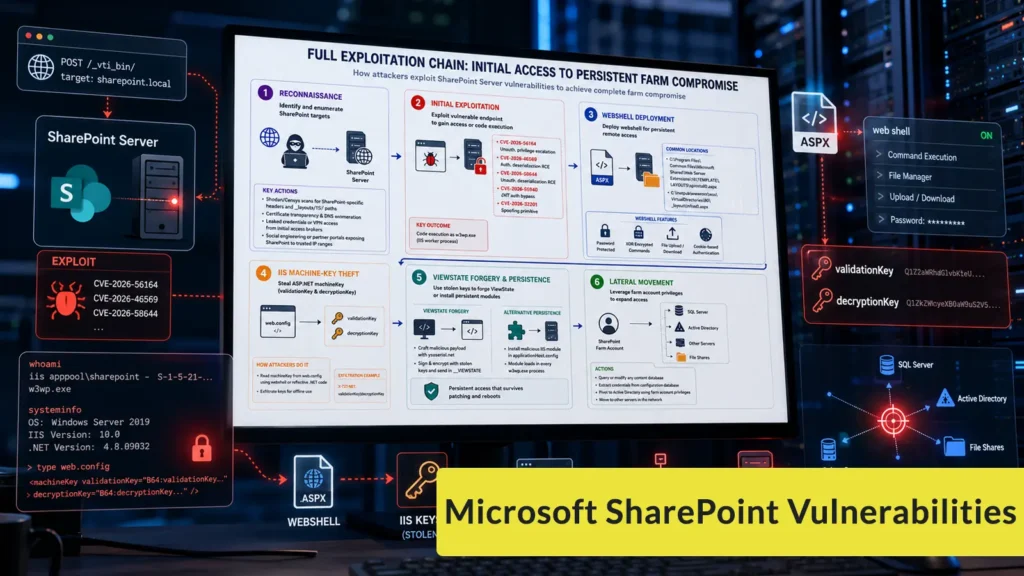
Microsoft SharePoint Server flaws are being actively exploited to gain remote code execution, install persistent web shells, and steal cryptographic keys from exposed systems. The attacks put on-premises SharePoint deployments at risk of data theft, network compromise, ransomware, and prolonged unauthorized access. The issue affects SharePoint Server Subscription Edition, SharePoint Server 2019, and SharePoint Server […]
15-Year-Old NGINX Vulnerability Lets Attackers Crash Workers and Achieve Remote Code Execution
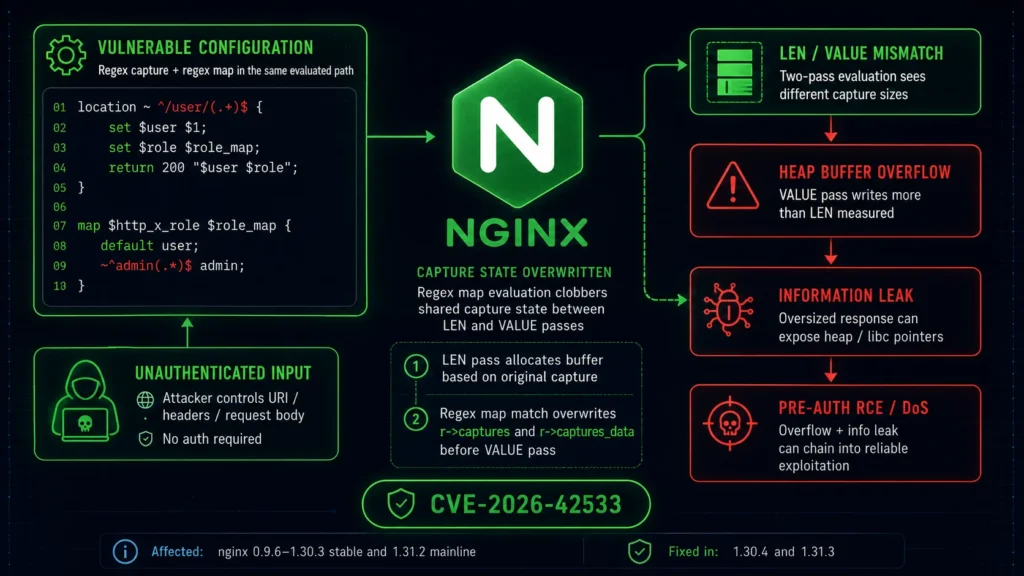
A newly disclosed flaw tracked as CVE-2026-42533 affects nginx’s script engine and has been silently exploitable since March 2011, when the map directive gained regex support. Security researcher Stan Shaw reported the bug to F5 SIRT, which coordinated a fix released in nginx 1.30.4 (stable) and 1.31.3 (mainline), along with corresponding patches for NGINX Plus […]
Weekly Cyber Security Newsletter Bulletin EY Breach, Wpzshell Exploit, Notepad++ Flaws +20 Stories
This week’s cybersecurity situation shows a clear reality: every part of technology, from identity systems to common productivity tools, can be hacked or compromised. Microsoft’s July Patch Tuesday alone addressed roughly 570 vulnerabilities, including two zero-days already being exploited in the wild against SharePoint Server and Active Directory Federation Services, signaling that attackers are moving […]
Hugging Face Confirms AI-Driven Breach: Attackers used Autonomous Agents, defenders countered with AI
Hugging Face disclosed this week that it detected and contained a production infrastructure intrusion, driven end-to-end by an autonomous AI agent system, and defended against it using its own AI-based forensic analysis. The attackers exploited two code-execution flaws in Hugging Face’s dataset processing pipeline: a remote-code dataset loader and a template-injection vulnerability in dataset configuration. […]