
Maine Takes Data Breach Reporting Portal Offline After Fake VRChat and Discord Filings
The Office of the Maine Attorney General has temporarily taken its public-facing data breach reporting database offline after discovering that an unknown entity submitted fabricated breach notifications targeting two major online platforms, VRChat and Discord, in what officials are calling a deliberate abuse of the state’s breach disclosure system. On June 12, 2026, the Maine […]
152 Chrome Extensions Hide Ad Tracking and Fake Google Search Traffic
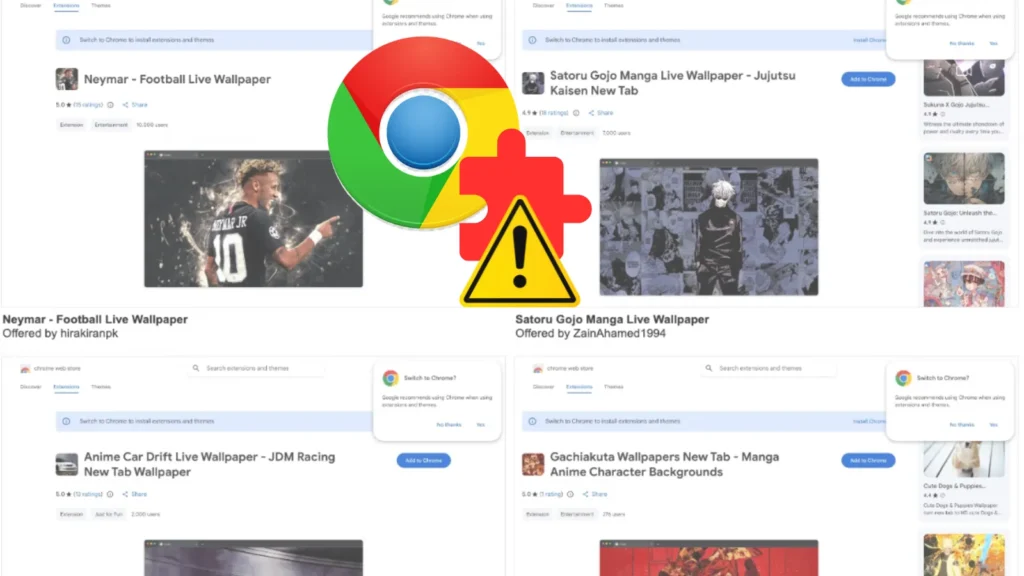
152 Chrome “live wallpaper” extensions on the Chrome Web Store have been caught secretly logging user data and faking Google “organic search” traffic to inflate ad revenue, despite promising they do not collect any data. This adware‑adjacent campaign abuses new‑tab extensions to launder extension‑generated visits into what appears to be legitimate search traffic, polluting analytics […]
New Agentjacking Attack Hijacks Your AI Coding Agent to Run Code From a Hackers Server
New “Agentjacking” attack that hijacks AI coding agents and silently executes attacker-controlled code on developer machines using nothing more than a single injected Sentry error. The technique turns trusted AI assistants like Claude Code and Cursor into an execution layer for malicious commands, without phishing, malware delivery, or any breach of the victim’s infrastructure. In […]
BugHunter Bug Bounty Toolkit Powered by Claude and Free AI Providers
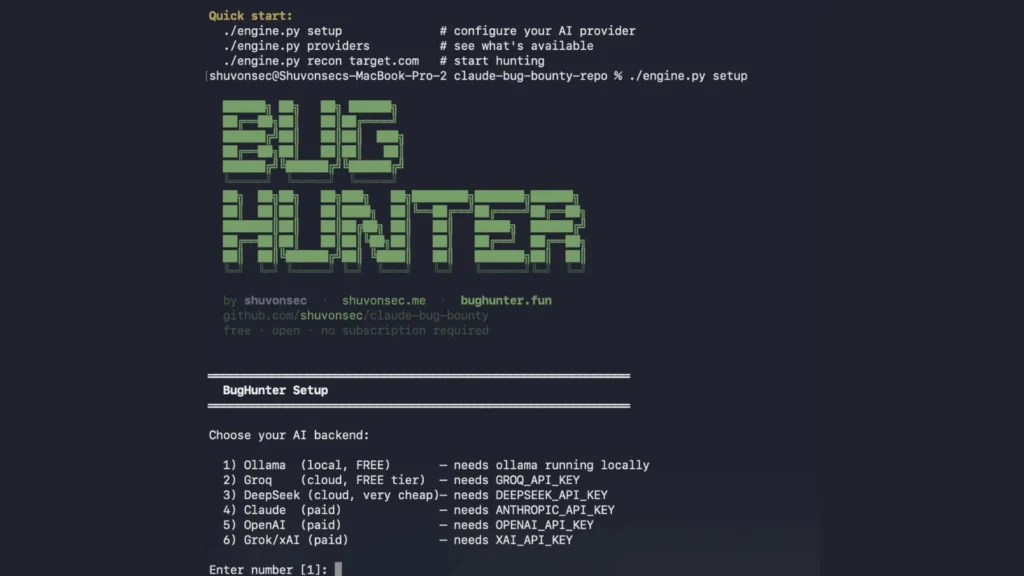
A new open-source bug bounty hunting toolkit called BugHunter, built on top of Anthropic’s Claude Code and now extended to support free AI providers like Ollama and Groq, is gaining traction in the security research community for automating the full vulnerability discovery and reporting pipeline. Developed by security researcher Shuvon Md Shariar Shanaz and hosted […]
Splunk Enterprise Pre-Auth RCE Chain Exposes Database With Zero Authentication
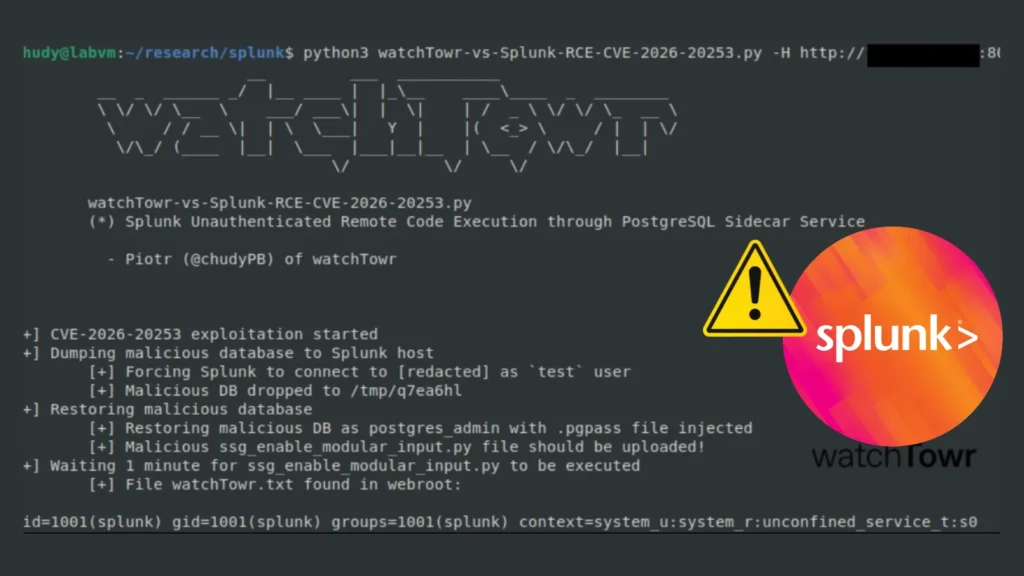
A critical vulnerability chain in Splunk Enterprise has been disclosed, enabling unauthenticated attackers to achieve remote code execution (RCE) through a misconfigured PostgreSQL sidecar service. Tracked as CVE-2026-20253, the flaw has a CVSS score of 9.8 and affects Splunk Enterprise 10 and later. The issue originates from the PostgreSQL Sidecar Service, an internal component introduced […]
Anthropic Fable 5 and Mythos 5 Access Blocked to All Users Following Government Directive
Anthropic has disabled its two most capable AI models, Fable 5 and Mythos 5, after the U.S. government issued an export control directive late on June 12 ordering the company to block access for any foreign national, whether inside or outside the United States, including Anthropic’s own foreign-national employees. Because the company says it cannot […]
Fancy Bear Hackers Abuse EdgeRouters and Cloud Services to Launch Stealthy Cyberattacks
One of the most persistent hacking groups in the world has found a new way to stay hidden. The threat actor known as Fancy Bear, formally tracked as APT28 and attributed to Russia’s military intelligence unit GRU Unit 26165, has been quietly shifting how it runs cyberattack operations. Instead of relying on traditional infrastructure, the […]
Authorities Dismantle Cryptocurrency Laundering Services AudiA6 Used by Ransomware Gangs
Authorities have dismantled a major cryptocurrency laundering service known as “AudiA6,” widely used by ransomware groups and cybercriminal networks to obscure illicit financial flows and cash out stolen digital assets. The international operation targeted what investigators described as an industrial-scale laundering platform that processed more than EUR 336 million between 2022 and 2025. The service […]
Oracle PeopleSoft 0-Day RCE Vulnerability Exploited in Attacks by ShinyHunters
Mandiant and Google Threat Intelligence Group (GTIG) have issued a critical warning after identifying an active compromise-and-extortion campaign targeting Oracle PeopleSoft infrastructure, attributed to the notorious threat actor UNC6240, also known as ShinyHunters. The campaign exploited CVE-2026-35273, a critical unauthenticated remote code execution (RCE) vulnerability with a CVSS score of 9.8, as a zero-day before […]
CISA Requires Federal Agencies to Patch Critical Vulnerabilities Within 3 Days
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has issued Binding Operational Directive (BOD) 26-04, titled “Prioritizing Security Updates Based on Risk,” compelling all Federal Civilian Executive Branch (FCEB) agencies to remediate the most dangerous known exploited vulnerabilities within just three calendar days. The directive, released on June 10, 2026, represents the most aggressive federal […]