
PoC Exploit Released for Guest-to-Host Escape Linux Kernel Vulnerability
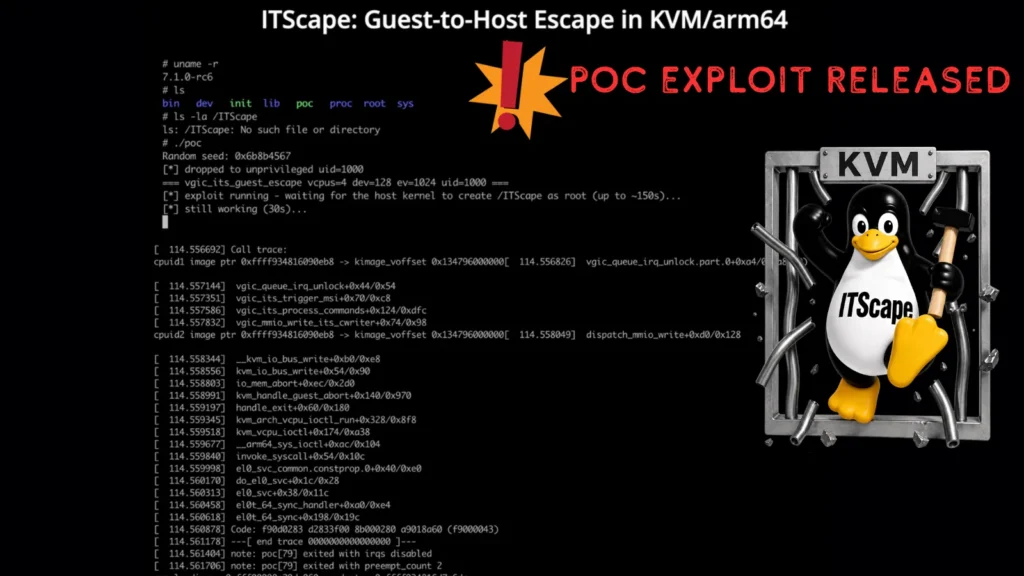
A proof-of-concept (PoC) exploit has been released for a critical Linux kernel vulnerability, CVE-2026-46316, that enables a guest-to-host escape in KVM environments on arm64 systems. The flaw, named “ITScape,” allows attackers to break out of a virtual machine and execute arbitrary commands on the host with full kernel-level privileges. The vulnerability was discovered by security […]
Anthropics Claude Fable 5 Jailbroken to Generate Stack Exploits
Anthropic launched Claude Fable 5 on June 9, 2026, as the first publicly available model in its new Mythos class, its most capable AI to date, excelling in software engineering, knowledge work, and vision benchmarks. Researcher “Pliny the Liberator” defeats Claude Fable 5’s safety classifiers using multi-agent decomposition, Unicode tricks, and narrative framing, leaking the […]
Hackers Abuse Fake Utility Downloads to Install ScreenConnect and Mine Cryptocurrency
Hackers are turning everyday software searches into a trap. A sophisticated cryptojacking campaign is actively targeting users who search for popular PC utilities online, luring them into downloading malware-laced files that secretly mine cryptocurrency using their own GPU. The attackers have built a network of more than 150 fake download sites that closely mimic trusted […]
Hackers Deploy MLTBackdoor Malware via Multi-Stage ClickFix Infection Chain
A newly discovered backdoor malware called MLTBackdoor is making waves in the cybersecurity community after being spotted in a carefully designed, multi-stage attack chain. Identified in May 2026, this threat stands out for its advanced ability to hide from security tools while quietly establishing a deep foothold on infected machines. The infection begins with something […]
New Windows Defender 0-Day Exploit RoguePlanet Grants SYSTEM Access to Attackers
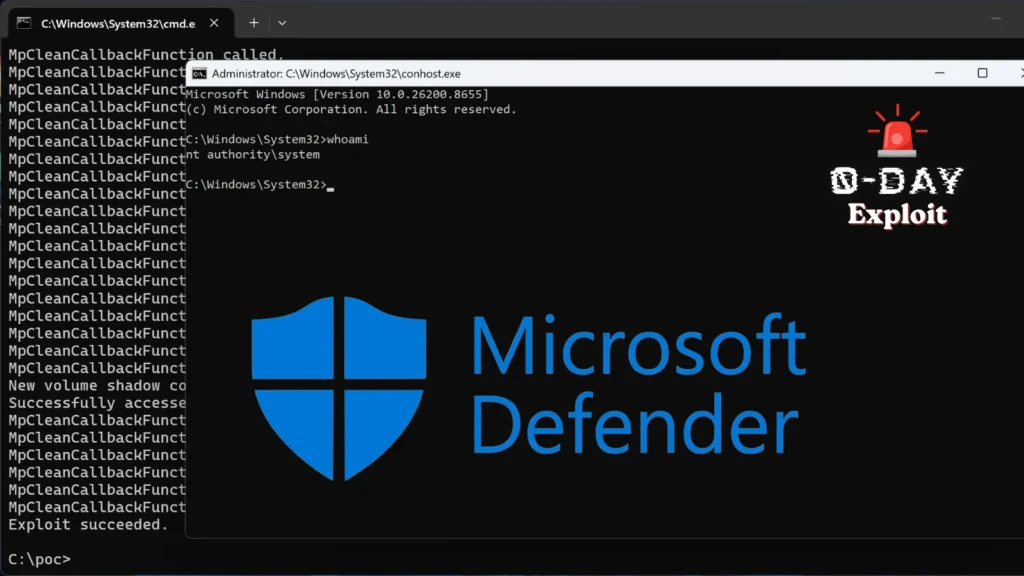
A researcher known as Nightmare Eclipse (also tracked as Chaotic Eclipse or Dead Eclipse) has publicly released a new proof-of-concept (PoC) exploit named RoguePlanet, targeting a previously undisclosed race condition vulnerability in Microsoft Windows Defender. When successfully executed, the exploit spawns a command shell running under SYSTEM-level privileges, granting an attacker the highest possible access […]
New MagicAd Android Malware Flood Device With Ads Bypassing Restrictions
A newly discovered Android trojan called MagicAd has been found flooding infected devices with ads, cleverly slipping past the built-in restrictions of the Android operating system. What makes this threat stand out is not just what it does, but how it does it. It uses multiple techniques to keep showing ads in the background, even […]
New NFCShare Android Malware Delivered via Weaponized Versions of Egitimate Banking Apps
A newly evolved strain of Android malware known as NFCShare is being spread through fake versions of legitimate banking apps, putting mobile users across Europe at serious risk. The malware is designed to secretly steal payment card data using a phone’s NFC chip, and it has grown into a much broader and more coordinated campaign […]
Apache HTTP Server 2.4.68 Released With Fix For Use-After-Free, DoS, XSS, and Buffer Overflow Flaws
The Apache Software Foundation released Apache HTTP Server version 2.4.68 on June 8, 2026, addressing 13 security vulnerabilities spanning multiple modules. The patched flaws include use-after-free conditions, cross-site scripting, heap-based buffer overflows, denial-of-service, privilege escalation, and out-of-bounds read issues affecting all versions from 2.4.0 through 2.4.67. Administrators running any prior release are strongly urged to […]
New China-Linked Threat Cluster OP-512 Targets IIS Servers With Cryptographically Unique Web Shell Framework
A newly identified threat cluster with suspected ties to China has been caught targeting Internet Information Services (IIS) web servers using a purpose-built web shell framework. Tracked as OP-512, this group stands out for deploying tools designed to evade every detection method that works against similar China-linked actors. The discovery marks another escalation in a […]
OWASP Releases AI Security Report to Empower Security Professionals with New Tools
OWASP has released the “State of Agentic AI Security and Governance v2.01” report, a technical blueprint aimed at security teams racing to secure rapidly proliferating autonomous AI agents in production. The report, part of the OWASP GenAI Security Project’s Agentic Security Initiative, reframes AI security as an operational reality rather than a theoretical concern, backed […]