
Hackers Can Hijack Claude Code MCP Traffic to Steal OAuth Tokens
A five-step attack chain that silently redirects Claude Code’s Model Context Protocol (MCP) traffic through attacker-controlled infrastructure, intercepting OAuth bearer tokens that grant persistent, broadly scoped access to connected SaaS platforms like Jira, Confluence, and GitHub with no patch incoming from Anthropic. Researchers at Mitiga Labs have demonstrated the attack, with the entry point being […]
New EDRChoker Tool Uses Policy-Based Quality of Service to Block EDR Processes
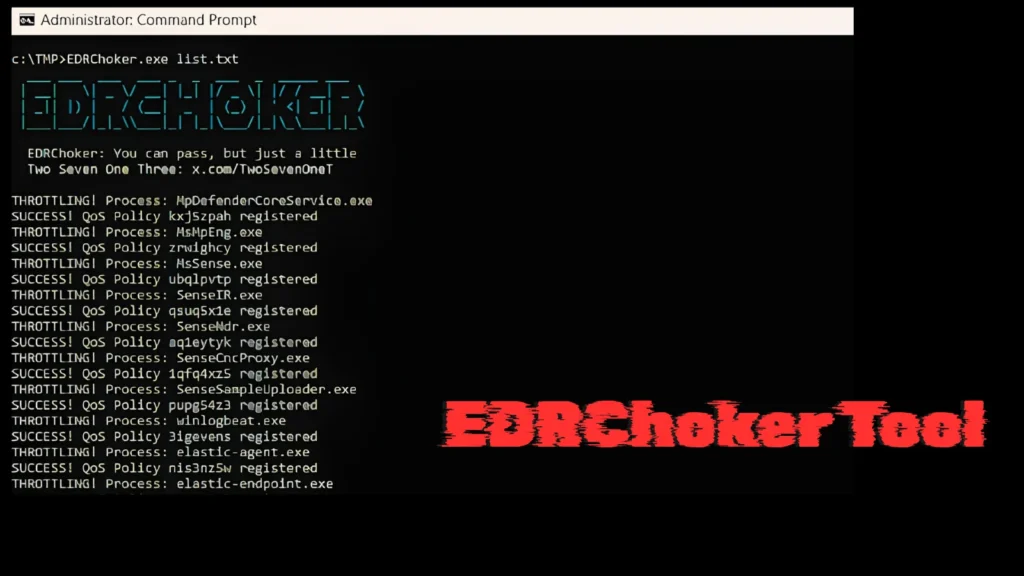
A newly released open-source red team tool called EDRChoker introduces a novel technique for silencing cloud-connected Endpoint Detection and Response (EDR) agents not by killing their processes or injecting code, but by quietly choking their network bandwidth to near-zero using Windows’ native Policy-Based Quality of Service (QoS) engine. Developed by security researcher @TwoSevenOneT, the tool exploits Windows […]
Instagram Fixes Password Reset Flaw That Exposes User Emails and Phone Numbers
A critical logic bug in Instagram’s web-based password reset flow on June 6, 2026, exposed unredacted email addresses and phone numbers associated with user accounts, including those belonging to high-profile individuals such as Meta CEO Mark Zuckerberg and model Georgina Rodriguez. Instagram’s parent company Meta deployed an emergency hotfix within hours of the disclosure, but […]
CISA Warns of Linux Kernel Improper Authentication Vulnerability Exploited in Attacks
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has added a critical Linux kernel vulnerability, tracked as CVE-2022-0492, to its Known Exploited Vulnerabilities (KEV) catalog, warning that the flaw is being actively leveraged in real-world attacks. The issue, categorized as improper authentication, affects Linux systems using the cgroups v1 release_agent feature and may allow attackers […]
New ChatGPT Lockdown Mode to Mitigate Prompt Injection and Data Exfiltration Attacks
OpenAI has released ChatGPT Lockdown Mode, a new security feature designed to limit outbound network access and reduce the risk of data exfiltration from prompt-injection attacks. The feature is now available to eligible personal accounts, self-serve ChatGPT Business users, and managed enterprise workspaces. Prompt injection, where malicious instructions are embedded in content processed by an […]
CISA Warns of SolarWinds Serv-U Vulnerability Exploited in Attacks
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has added a critical SolarWinds Serv-U vulnerability to its Known Exploited Vulnerabilities (KEV) catalog, warning that threat actors are actively exploiting the flaw in the wild. Tracked as CVE-2026-28318, the vulnerability affects SolarWinds Serv-U file transfer software and enables unauthenticated attackers to crash the service through specially […]
OWASP CVE Lite CLI New Tool to Scan for Vulnerabilities in Your Projects
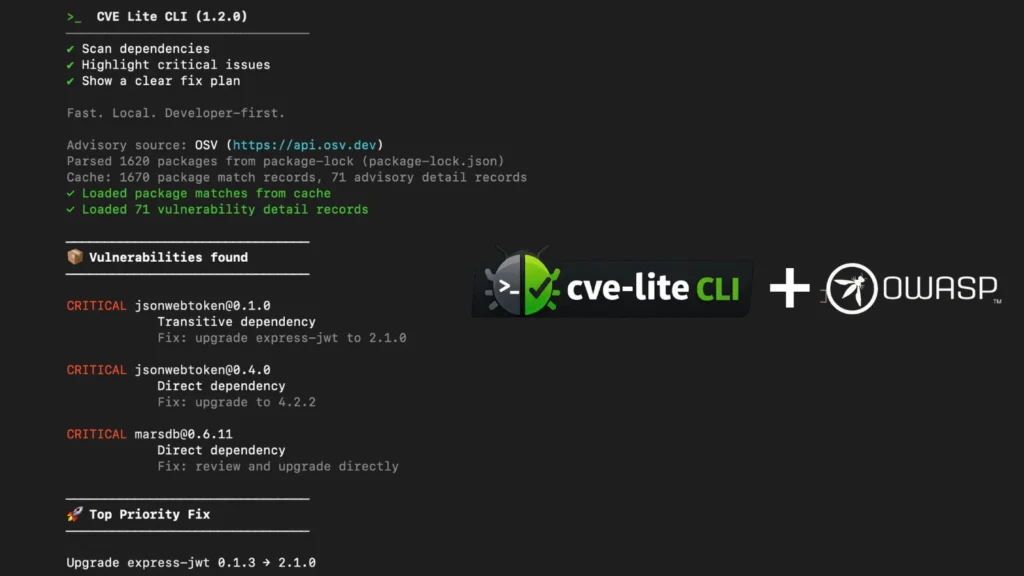
CVE Lite CLI is a free, open-source vulnerability scanner officially recognized as an OWASP Incubator Project, designed to bring dependency security directly into developers’ terminals rather than leaving it buried in CI pipelines. Maintained by Sonu Kapoor and backed by the same organization behind the OWASP Top 10, the tool addresses a longstanding gap in […]
Hola Browser for Windows Delivery Pipeline Compromised to Deliver Cryptominer
A trusted browser application has landed at the center of a supply chain security incident after researchers discovered that its official delivery pipeline had been quietly compromised. Hola Browser for Windows, used by millions of users around the world, was found distributing an unexpected executable file alongside its legitimate installer. The file, named me.exe, was […]
VECT 2.0 Ransomware Can Damage Files Its Own Decryptor Cannot Reliably Restore
A new ransomware strain called VECT 2.0 is raising serious concerns among security professionals, and for a troubling reason — even if a victim pays the ransom, the attacker’s own decryptor may not fully restore their files. This is not a typical failure tied to weak defenses or victim error. The damage, in many cases, […]
ClawHub, Cisco, Vercels Malicious Skill Detector Bypassed to upload Malicious Skills
AI skill scanners from ClawHub, Cisco, and Vercel’s skills. The platform can be bypassed with minimal effort, allowing malicious skills to be uploaded and distributed through public marketplaces. The findings highlight a growing supply chain risk in agent ecosystems, where skills serve as reusable components that can execute code and influence model behavior. The Trail […]