
Tensorlake npm Package Compromised to Spread Shai-Hulud Worm and Steal Developer Secrets
A malicious release of the Tensorlake npm package has been published with a Shai-Hulud worm variant that can steal developer secrets and attempt to spread through connected software supply chains. The affected version, tensorlake@0.5.144, was released on October 8, 2026. Tensorlake is a serverless sandbox platform for AI agents, and its npm package has recorded […]
Solo Hacker Used AI Tools to Breach South Korean Financial Organizations and Steal Data
A suspected lone threat actor used an AI-powered penetration-testing tool called ARTEX to breach several South Korean financial organizations and steal customer and employee data. The activity, which ran from late September to early October 2026, affected banks, savings banks, capital firms, and online lending services. The case shows how open-source AI tools can help […]
Discord Users Data Exposed in Security Bot Double Counter Security Breach
Double Counter, a Discord security bot, has disclosed a breach that exposed user data after an attacker broke into its cloud systems on October 4, 2026. Attackers copied about 12 GB of database records, and the stolen bot token was used to post unwanted invitations across roughly 50 large Discord servers. According to Double Counter’s […]
Anthropic Mythos AI Finds Rejetto HFS Flaw That Lets Attackers Forge Admin Sessions and Execute Code
Anthropic’s Mythos AI has identified a critical vulnerability in Rejetto HTTP File Server that could allow remote attackers to forge administrator sessions and execute arbitrary code. The issue, tracked as CVE-2026-61500, stems from predictable session-signing keys generated through JavaScript’s non-cryptographic Math.random() function. Horizon3 made the finding after joining Anthropic’s Project Glasswing in July 2026, which […]
Anthropic Opens Claude Access to Red Teams and Verified Cyber Defenders With Reduced Restrictions
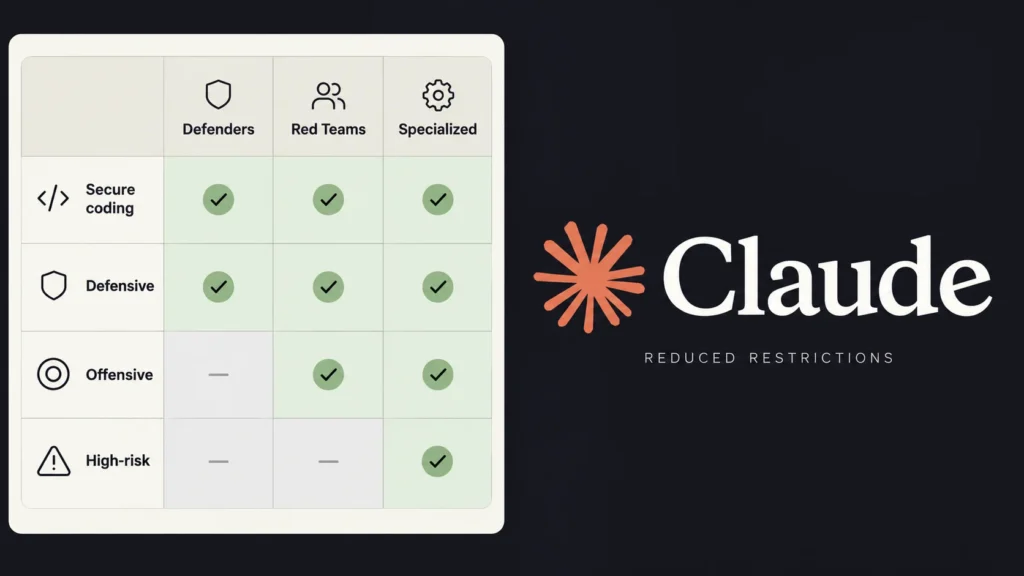
Anthropic has expanded its Cyber Verification Program, giving verified security professionals access to advanced Claude models with fewer cybersecurity restrictions. Announced on October 6, 2026, the update introduces three access tiers covering defensive research, authorized penetration testing, and testing of systems where failures could threaten lives or disrupt markets. The program includes Claude Opus 5.5, […]
Critical Apache Struts Vulnerabilities Enables Remote Code Execution Attacks
Four security flaws described in the supplied Apache Struts advisories could expose affected applications to remote code execution, denial-of- service, and unintended data disclosure. Recommended fixes include Struts 7.4.0 or later, or Struts 6.12.0 or later for organizations using the 6.x maintenance line. The vulnerabilities affect different framework components, so exposure depends on application configuration […]
Midnight Blizzard Abuses Hotel Wi-Fi Captive Portals to Deliver Malware and Steal Credentials
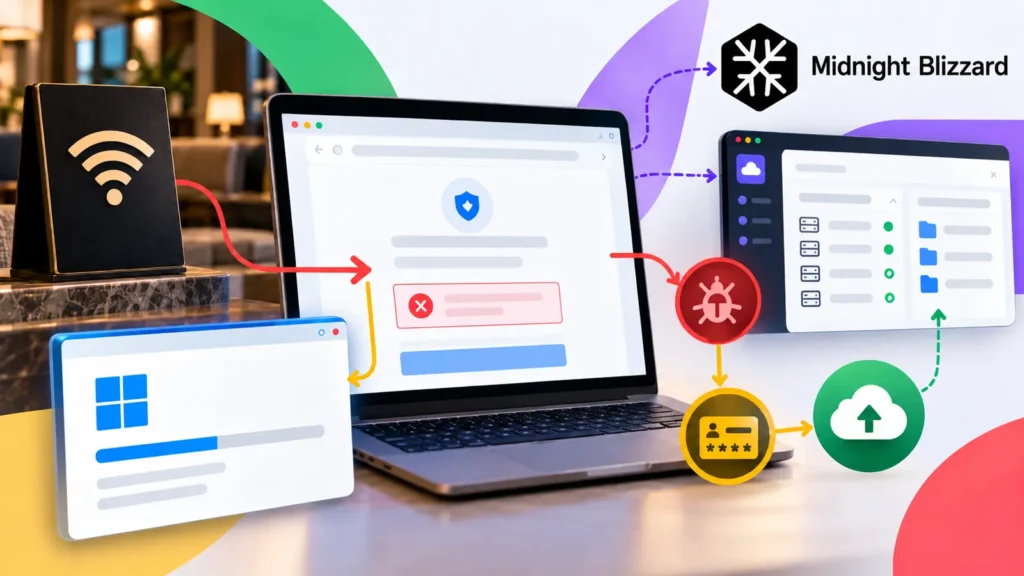
Travelers connecting to hotel Wi-Fi may now face more than an unreliable internet signal. A campaign linked to Midnight Blizzard has turned captive portals, the sign-in pages shown before online access, into a route for malware, credential theft, and possible access to corporate accounts. The operation, known as CaptiveCrunch, has affected hospitality-related networks and other […]
Hacker Group Claims to Have Stolen Trump Mobile Customers Personal Data
Trump Mobile customers’ personal data has appeared on a dark web leak site after a ransomware group called BYOD claimed it breached the company. The published file reportedly contains 3,615 records, including names, email addresses, phone numbers, home addresses, and order details. Straight Arrow News reported the incident on October 5, 2026, after reviewing the […]
Malicious HEIC Images Can Trigger Remote Code Execution on WordPress Servers
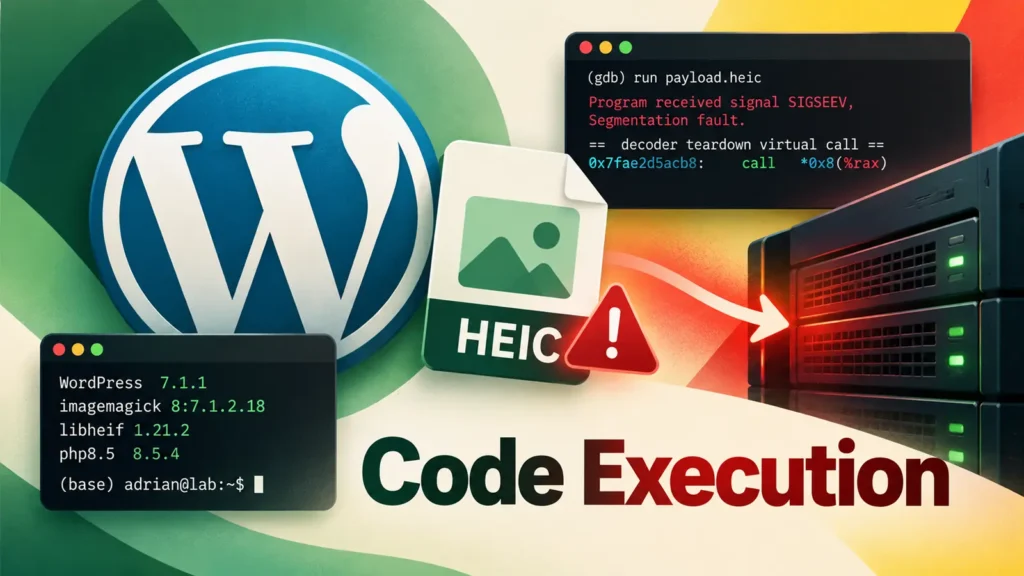
A malicious HEIC image can become a route to remote code execution on a WordPress server. Researchers have demonstrated an attack chain that turns a normal Media Library upload into code execution in the PHP-FPM process that runs the site. The risk comes from libheif, a widely used component that reads HEIC, HEIF and AVIF […]
Google Pauses Open-Source Bug Bounty Program After Flood of Invalid AI-Generated Reports
Google has temporarily stopped accepting new product vulnerability reports through its Open Source Software Vulnerability Reward Program(OSS VRP) following a major increase in automated submissions that were mostly invalid. The change took effect on October 1, 2026, and Google said it will provide an update on the program in the first quarter of 2027. The […]