
Amazon Quick Bug Exposed AI Chat Agents to Users Blocked by Custom Permissions
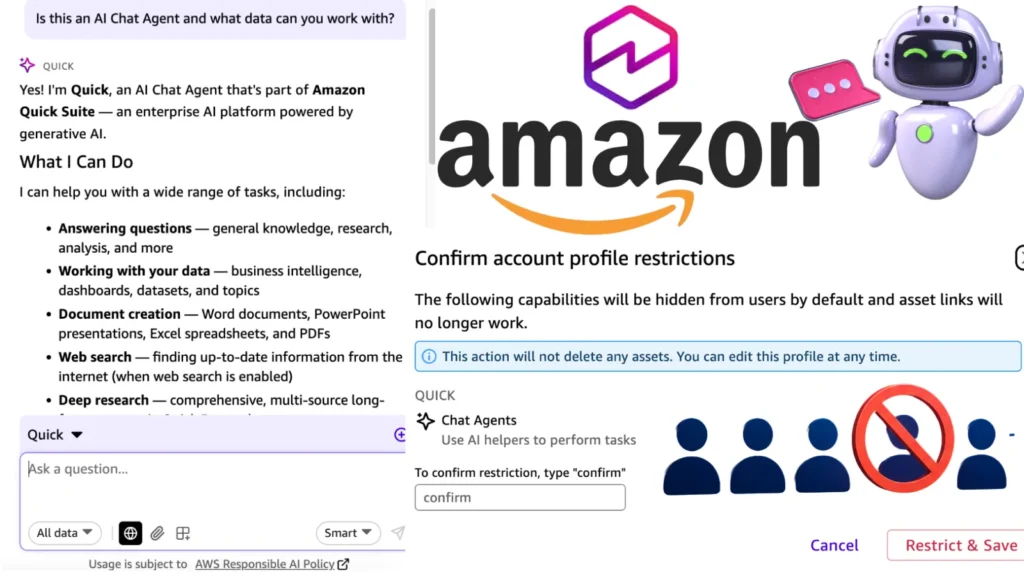
Imagine locking your organization’s sensitive data behind a heavy vault door, only to realize the locking mechanism is entirely missing. Security researchers at Fog Security recently uncovered a severe authorization bypass in Amazon Quick’s AI Chat Agents. This vulnerability allowed blocked users to interact freely with enterprise AI tools, despite explicit administrative restrictions. Compounding the […]
Windows DNS Client Vulnerability Enables Remote Code Execution Attacks
A newly disclosed vulnerability in the Microsoft Windows DNS Client could let attackers silently execute malicious code across enterprise networks, exposing a massive attack surface. Officially designated as CVE-2026-41096, this critical security flaw carries a severe CVSS score of 9.8 out of 10. By simply returning a maliciously crafted response to a routine network query, […]
How Top SOCs and MSSPs Prevent Phishing Incidents Missed by Email Filters
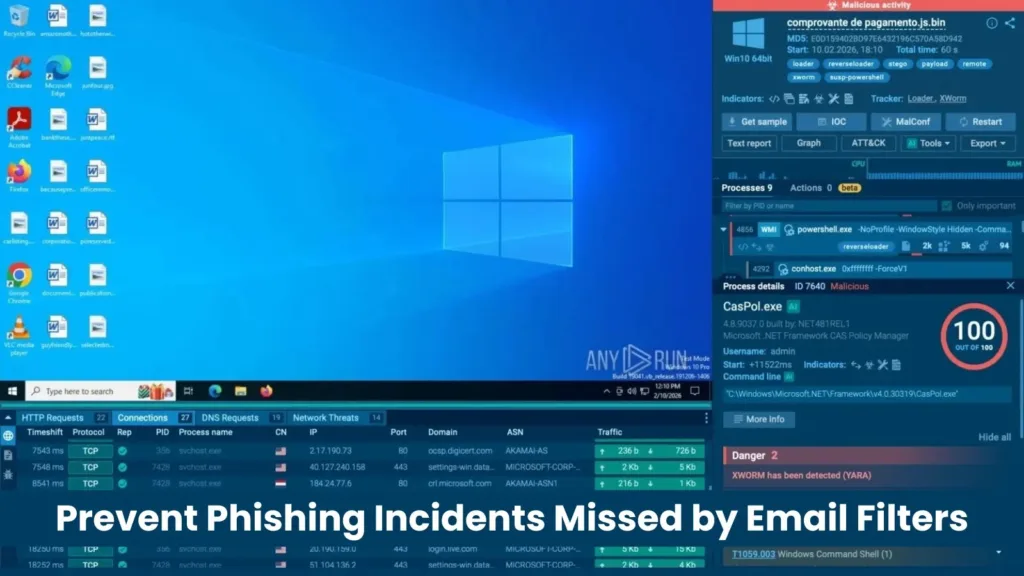
Email filters are important, but they can’t remove phishing risk on their own. Today’s campaigns are built to slip through the cracks, using fresh domains, CAPTCHA checks, fake login pages, OTP theft, and even legitimate RMM tools. For security leaders, the bigger issue is business exposure. One missed email can slow response, create uncertainty, and leave teams unsure […]
Foxconn Confirms Cyberattack After Nitrogen Ransomware Gang Claim
Foxconn has officially confirmed a cyberattack targeting its North American operations after the Nitrogen ransomware gang publicly listed the company on its data leak site, claiming to have stolen a staggering 8 terabytes of sensitive data. The Nitrogen ransomware group made its move on Monday, posting Foxconn on its breach and extortion portal and asserting […]
Google Enhances Android Mobile Security with New AI-Powered Protections
Android smartphones have become the go-to device for billions of people around the world. From banking and messaging to storing personal photos and sensitive documents, people rely on them for almost everything. That reliance has made mobile devices a prime target for scammers, cybercriminals, and threat actors who constantly evolve their tactics to slip past […]
Microsoft Patch Tuesday May 2026 120 Vulnerabilities Fixed, Including 29 Critical RCE Flaws
Microsoft’s May 2026 Patch Tuesday lands with a heavy enterprise focus, fixing 120 vulnerabilities across Windows, Office, Azure, developer tools, and Microsoft 365 apps, including 29 remote code execution (RCE) flaws rated Critical. Unlike several recent cycles, Microsoft reports no zero‑days exploited in the wild or publicly disclosed ahead of the release, but the breadth […]
Threat Actors Leverage Vercels AI Tools to MassProduce Realistic Phishing Sites
A new and growing wave of phishing attacks is making credential theft easier than ever before. Threat actors are now using Vercel, a legitimate AI-powered web development platform, to build convincing fake login pages that closely mirror real websites. The ease and low cost of this approach has opened the door for a broader range […]
TeamPCP Compromised Checkmarx Jenkins AST Plugin Following KICS Supply Chain Attack
A supply chain attack that started with a relatively obscure open-source scanner has now reached one of the most widely used application security tools in the industry. In May 2026, a malicious version of the Checkmarx Jenkins AST plugin was quietly published to the Jenkins Marketplace, exposing development pipelines to credential theft and unauthorized access. […]
Popular Go Library fsnotify Raises Supply Chain Alarms After Maintainer Access Changes
A widely used Go library called fsnotify has found itself at the center of a supply chain security scare after a sudden change in maintainer access triggered alarm across the open source community. The project provides cross-platform filesystem notifications for applications running on Windows, Linux, macOS, BSD, and illumos. Contributors were removed from its GitHub […]
Hackers Use PlugX-Like DLL Sideloading Chain in Fake Claude Malware Campaign
Cybercriminals are getting creative with how they lure victims into downloading malware, and a new campaign involving a fake version of Anthropic’s Claude AI assistant is raising serious concerns. Attackers set up a convincing lookalike website to distribute a dangerous installer that quietly plants a backdoor on infected systems. The campaign uses a chain of […]