
Critical WordPress Plugin Vulnerability Exposes Websites to Authentication Bypass Attacks
A critical vulnerability in a widely used WordPress plugin has exposed over 200,000 websites to full account takeover, raising urgent concerns across the security community. Discovered on May 8, 2026, by Wordfence’s AI-powered PRISM threat intelligence platform, the flaw affects the Burst Statistics plugin, a privacy-focused analytics tool. Tracked as CVE-2026-8181 with a CVSS score […]
Grafana Labs Security Breach Hackers Access GitHub and Download Codebase
A threat actor infiltrated Grafana Labs’ GitHub environment, stealing a privileged token to download the company’s private codebase, and then attempted to extort the open-source observability giant with an unanswered ransom demand. Grafana Labs disclosed on May 16, 2026, that an unauthorized party obtained a token granting access to its GitHub environment, enabling the threat […]
First Public macOS Kernel Exploit on Apple M5 Prepared Using Mythos Preview in Five Days
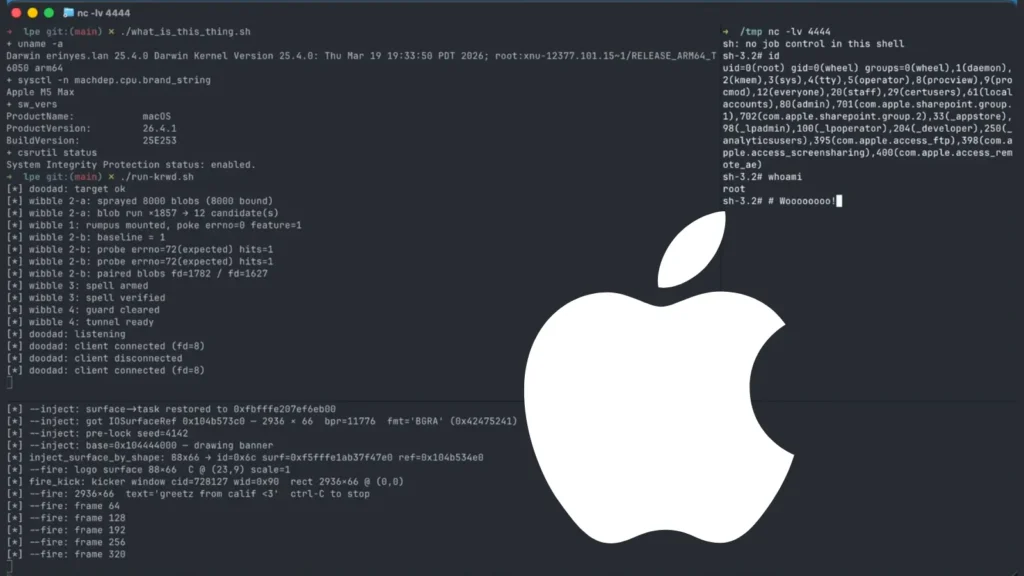
Apple’s M5 silicon has reportedly been exploited for the first time in a public macOS kernel memory corruption attack, successfully bypassing the company’s notable hardware-level memory protection. Researchers from Calif, Bruce Dang, Dion Blazakis, and Josh Maine, developed a working kernel local privilege escalation (LPE) exploit targeting macOS 26.4.1 (25E253) on bare-metal M5 hardware. The […]
Microsoft Exchange, Windows 11, and Cursor Zero-Days Exploited on Pwn2Own Day 2
Pwn2Own Berlin 2026 is rapidly escalating into one of the most intense offensive security contests in recent years, with Day Two delivering a fresh wave of critical zero-day exploits targeting enterprise software, AI tools, and operating systems. Security researchers demonstrated real-world attack scenarios against high-value targets, including Microsoft Exchange, Windows 11, and AI coding platforms, […]
JDownloader Website Compromised to Distribute Malicious Windows and Linux Installers
A widely used download manager trusted by millions has briefly turned into a malware delivery platform after attackers compromised the official JDownloader website, replacing legitimate installers with malicious versions targeting both Windows and Linux users. The incident, confirmed by developers and security researchers, occurred between May 6 and May 7, 2026. During this window, threat […]
Malicious JPEG Images Could Trigger PHP Memory Safety Vulnerabilities
Two critical memory-safety vulnerabilities in PHP’s image-processing functions could allow attackers to leak sensitive heap memory or to execute denial-of-service attacks via specially crafted JPEG files. The flaws, discovered in PHP’s ext/standard extension by Positive Technologies researcher Nikita Sveshnikov, affect the widely-used getimagesize and iptcembed functions that process JPEG metadata and IPTC data. PHP Memory […]
Linux Kernel Vulnerability ssh-keysign-pwn Lets Attackers Read SSH Keys and Shadow Passwords
A newly disclosed Linux kernel vulnerability is raising serious concerns across the security community, as it allows attackers to access highly sensitive data, including SSH private keys and password hashes, on affected systems. Tracked as CVE-2026-46333, the flaw has been nicknamed “ssh-keysign-pwn” and impacts a wide range of Linux distributions. Linux Kernel Vulnerability “ssh-keysign-pwn” The issue originates in […]
Gunra Ransomware Expands RaaS Operations After Shifting From Conti-Based Locker
Gunra ransomware has quickly grown from a new threat into a serious global problem, hitting dozens of organizations in less than a year. The group behind it is not just encrypting data, but also running a business-like operation that sells access, leaks stolen files, and recruits partners to spread its malware. For defenders, this is […]
OpenClaw Chain Vulnerabilities Expose 245,000 Public AI Agent Servers to Attack
A chain of four critical vulnerabilities discovered in OpenClaw, one of the fastest-growing open-source platforms for autonomous AI agents, has left an estimated 245,000 publicly accessible server instances exposed to remote exploitation, credential theft, and persistent backdoor installation. Originally launched as “Clawdbot” in late 2025, OpenClaw connects large language models directly to filesystems, SaaS applications, […]
79 Chrome Vulnerabilities Patched, Including 14 Critical Ones Update Now!
Google has rolled out a massive security update for its Chrome browser, sealing a staggering 79 vulnerabilities before threat actors can exploit them. With 14 of these flaws rated as critical, browsing the web on an outdated version leaves your entire system wide open to devastating cyberattacks. The newest stable release bumps Chrome to 148.0.7778.167/168 […]