
OpenAI Warns macOS Users to Update ChatGPT and Codex Immediately
OpenAI has disclosed a security incident tied to the compromise of Axios, a widely used third-party JavaScript developer library, as part of a broader software supply chain attack detected on March 31, 2026. While the company confirmed no user data, API keys, or systems were compromised, it is taking aggressive precautionary measures to protect its […]
Google Launches Gmail End-to-End Encryption for Android and iOS
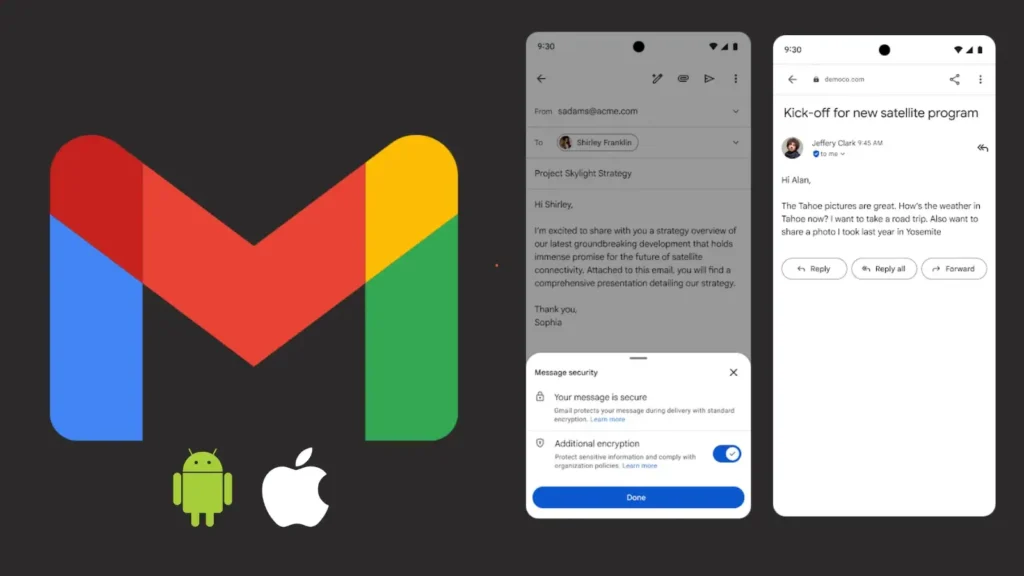
Google has officially rolled out End-to-End Encryption (E2EE) for the Gmail application on Android and iOS devices. This major update targets users utilizing Gmail client-side encryption. It allows organisations to handle sensitive data confidentially directly from their smartphones or tablets. The feature ensures compliance with strict data sovereignty rules while keeping the workflow entirely mobile. […]
Google Unveils Device-Bound Chrome Sessions in Anti-Cookie-Theft Move
Google officially announced the public rollout of Device Bound Session Credentials (DBSC) for Windows users on Chrome 146. According to the Google Account Security and Chrome teams, this major security update aims to eliminate session hijacking, a primary method for attackers to compromise user accounts. The feature will also expand to macOS in an upcoming […]
Ransomware Gangs Expand Use of EDR Killers Beyond Vulnerable Drivers, ESET Warns
In recent years, Endpoint Detection and Response (EDR) killers have become a standard, highly effective weapon in modern ransomware intrusions. Before launching their file-encrypting malware, cybercriminals routinely deploy specialized tools to bypass security software. According to a comprehensive new report by ESET Research, the threat landscape has grown far beyond the well-known Bring Your Own […]
Hacker Uses Claude and ChatGPT to Breach Multiple Government Agencies
A single threat actor compromised nine Mexican government agencies and stole hundreds of millions of citizen records in a highly sophisticated cyberattack. The campaign, which ran from late December 2025 through mid-February 2026, highlights a dangerous shift in the modern threat landscape. Researchers at Gambit Security recently released a full technical report detailing how the […]
Anthropic Launches Claude Beta for Word, Bringing AI-Powered Editing to Microsoft Docs
Anthropic has officially launched Claude for Word in public beta, bringing its AI assistant directly into Microsoft Word as a native sidebar add-in for Team and Enterprise users on both Mac and Windows platforms. The integration marks a significant step in Anthropic’s push to embed Claude into everyday productivity workflows beyond chat-based interactions. Claude for […]
EngageSDK Vulnerability Exposes Millions of Crypto Wallet Users to Cyberattacks
A serious security flaw found inside a widely used Android library called EngageSDK has put over 30 million cryptocurrency wallet users at risk of financial theft and personal data exposure. The vulnerability, described as an intent redirection flaw, allowed malicious apps on the same device to break through Android’s built-in security sandbox and gain unauthorized […]
MuddyWater Turns to Russian Malware-as-a-Service in New ChainShell Campaign
Iranian state-backed hacking group MuddyWater has made a decisive operational shift, adopting a Russian-built Malware-as-a-Service platform to power a new campaign against Israeli targets. The operation, built around a previously unknown tool called ChainShell, marks a clear departure from the group’s earlier reliance on custom-developed tools, and raises fresh concerns for organisations in critical sectors […]
New ClickFix Campaign Uses macOS Script Editor to Deliver Atomic Stealer
A newly discovered ClickFix campaign is targeting macOS users through a technique that completely bypasses Terminal, using Script Editor to drop the Atomic Stealer infostealer onto compromised systems. This campaign marks a clear shift in how attackers are responding to Apple’s tightening security controls — a sharp reminder that social engineering can work around almost […]
Hackers Impersonate Linux Foundation Leader in Slack to Target Open Source Developers
Open source developers are facing a growing and sophisticated threat — one that does not rely on complex exploits or hidden vulnerabilities but instead uses something far simpler: trust. A social engineering campaign is actively targeting developers through Slack, where an attacker poses as a respected Linux Foundation community leader to trick victims into downloading […]