
Microsoft 365 Network-Level Disruption Affecting Exchange Online, Teams, and Core Suite Services
A network-level disruption struck multiple Microsoft 365 services on Wednesday evening, knocking out or degrading access to Exchange Online, Microsoft Teams, and the broader Microsoft 365 suite for users across affected regions. The incident, tracked under issue ID MO1274150, began at approximately 8:37 PM IST (3:07 PM UTC) on April 8, 2026, and prompted Microsoft’s […]
Hackers Used EvilTokens, ClickFix Campaign to Attack Claude Code Users with AMOS Stealer
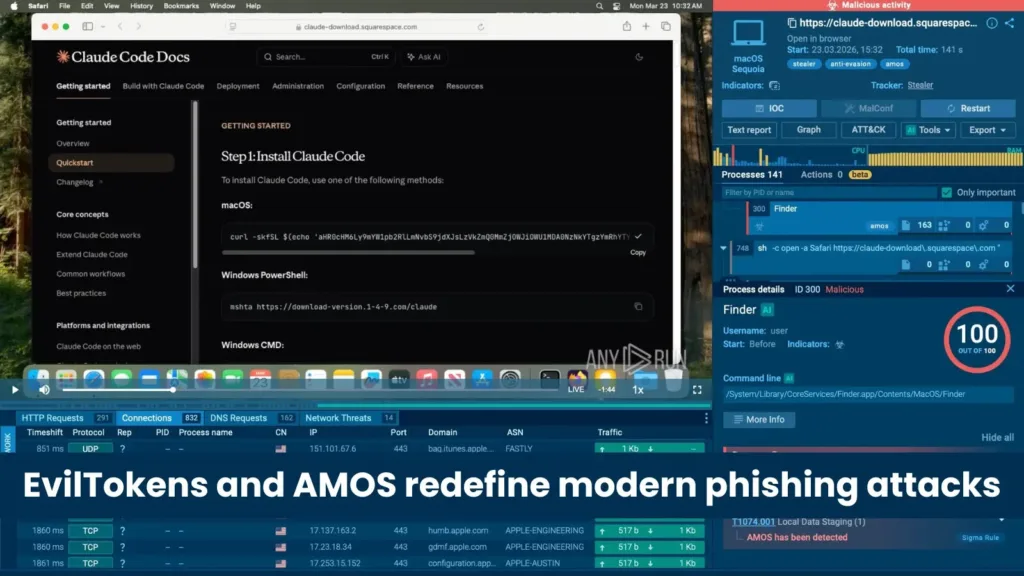
EvilTokens and AMOS redefine modern phishing attacks Two significant threat campaigns from March 2026, one abusing Microsoft’s OAuth authentication flow to silently hijack enterprise accounts, and another deploying the AMOS infostealer against macOS users who work with AI development tools like Claude Code. The EvilTokens campaign represents a significant evolution in phishing tactics because it […]
Microsoft Confirms Recent Windows 11 Update Breaks Start Menu Function
Microsoft has acknowledged a server-side issue that disrupted Start Menu search functionality for a subset of Windows 11 23H2 users, and has since deployed a fix to address the problem without requiring users to install any additional updates. The issue, officially tracked under release health identifier WI1273488, began surfacing around April 6, 2026, and was […]
CUPS Vulnerability Chain Enables Remote Attacker to Execute Malicious Code as Root User
A critical vulnerability chain in the Common Unix Printing System (CUPS) that allows unauthenticated remote attackers to execute arbitrary malicious code with root system privileges. Security researcher Asim Viladi Oglu Manizada and his team discovered two zero-day flaws, officially tracked as CVE-2026-34980 and CVE-2026-34990, that affect CUPS versions 2.4.16 and older. The sophisticated attack chain […]
Hackers Use Fake Gemini npm Package to Steal Tokens From Claude, Cursor, and Other AI Tools
A new supply chain attack has surfaced targeting software developers who work with AI coding tools. On March 20, 2026, a threat actor published a malicious npm package named gemini-ai-checker under the account gemini-check, presenting it as a simple utility to verify Google Gemini AI tokens. The package looked credible enough to fool developers — but beneath its […]
Iran-Linked Hackers Launch Password Spray Campaign Against Microsoft 365 Tenants in Middle East
Microsoft 365 tenants in the Middle East are facing a new password spray campaign tied to an Iran-linked threat actor. Rather than starting with malware files or software exploits, the attackers are trying to break in through weak passwords and exposed cloud accounts. The case shows how a basic identity attack can still open access […]
CISA Warns of Fortinet 0-Day Vulnerability Actively Exploited in Attacks
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has added CVE-2026-35616, a critical improper access control vulnerability in Fortinet FortiClient Enterprise Management Server (EMS), to its Known Exploited Vulnerabilities (KEV) catalog on April 6, 2026, mandating federal agencies to remediate by April 9, 2026. CVE-2026-35616 is a critical-severity flaw rooted in CWE-284 (Improper Access Control), carrying a CVSS score […]
Googles Bug Bounty Program Hits All-Time High With $17 Million in 2025 Payouts
Google’s Vulnerability Reward Program (VRP) celebrated its 15th anniversary in 2025 by breaking every payout record in its history. The tech giant awarded a staggering $17 million to external security researchers worldwide, representing a massive 40% surge compared to 2024. Over 700 ethical hackers from across the globe successfully identified and responsibly disclosed vulnerabilities, proving […]
CISA Adds TrueConf Vulnerability to KEV Catalog Following Active Exploitation
The Cybersecurity and Infrastructure Security Agency (CISA) has officially added a critical vulnerability affecting TrueConf software to its Known Exploited Vulnerabilities (KEV) catalog. Tracked as CVE-2026-3502, this security flaw is currently facing active exploitation in the wild. The discovery has prompted federal agencies and private organizations to take immediate defensive action to secure their networks. […]
New Progress ShareFile Bugs Let Attackers Take Over Servers Without Logging In
A dangerous attack chain in Progress ShareFile that can allow attackers to take over exposed on-premises servers without first logging in. The issues affect customer-managed ShareFile Storage Zones Controller 5.x deployments, and Progress says customers should upgrade to version 5.12.4 or move to any 6.x release, which is not impacted. According to Progress and WatchTower, […]