
GitLab Email Feature Vulnerability Lets Attackers Push Code Into Private Repositories
GitLab’s “Email work item to this project” feature can become a repository-compromise primitive when its private address is exposed, according to research published by Aikido Security researcher Joe Leon on September 23, 2026. The address contains a long-lived glimt- incoming-email token that GitLab says does not expire and must remain secret. GitLab documentation confirms that […]
The Domains Keep Disappearing, but the Malware Infrastructure Behind Them Never Moves
Fake verification pages are steering people toward malware, but the web addresses behind the lures keep changing. Over five months, investigators tracked four different attack chains that began with the same hosting network, even as domains, downloads and command servers shifted. The pattern makes blocking individual websites a poor way to stop the first step. […]
Hackers Exploiting F5 BIG-IP OAuth Server 0-day Flaw to Gain Remote Code Execution
F5 has warned that hackers are actively exploiting a critical zero-day vulnerability in BIG-IP Access Policy Manager (APM) deployments to execute code remotely without authentication. Tracked as CVE-2026-94127, the flaw affects virtual servers configured with both an APM access policy and an OAuth profile, specifically where APM operates as an OAuth Authorization Server. F5 published […]
Check Point Management Server 0-Day Vulnerability Actively Exploited in Attacks
Check Point has warned customers that attackers are exploiting a critical zero-day vulnerability in its Security Management infrastructure. Tracked as CVE-2026-93616, the flaw carries a CVSS score of 9.8 and enables an unauthenticated remote attacker to upload and execute arbitrary scripts on an exposed Management Server. Check Point says it has identified a handful of […]
Hackers Clone Legitimate Websites to Silently Trigger Chrome and Windows Zero-Day Exploits
Hackers are using convincing copies of trusted websites to turn an ordinary browser visit into a full Windows compromise. The campaign pairs targeted phishing emails with a chained set of previously unknown flaws in Google Chrome and Microsoft Windows, giving attackers a quiet path from a fake page to malware on a victim’s device. The […]
Metas Muse AI Agent 0-Day Vulnerability Allows Attackers to Hijack the Tool and Inject Malware
A zero-day vulnerability in Meta’s Muse AI agent for macOS could allow malware already running under a user account to hijack the assistant, intercept dictated prompts, inject malicious instructions, and steal authentication material. The flaw is especially concerning because a compromised agent could inherit the extensive permissions and connected-service access that users have entrusted to […]
Claude Opus 5 Helps Researchers Weaponize HEIF Image Flaw Into Remote Code Execution
A specially crafted image file was enough to turn a normal upload feature into a potential path to server takeover. Researchers have shown that a flaw in widely used image-decoding software can corrupt memory and, in certain cases, allow attackers to run code remotely on affected systems. The issue, named HEIF Heist, affects applications that […]
Weekly Cybersecurity Newsletter Bulletin Cisco and Android 0-Day, BragJack Attack, Claude Opus 5 Used to Hack OpenAI, and 20+ Stories
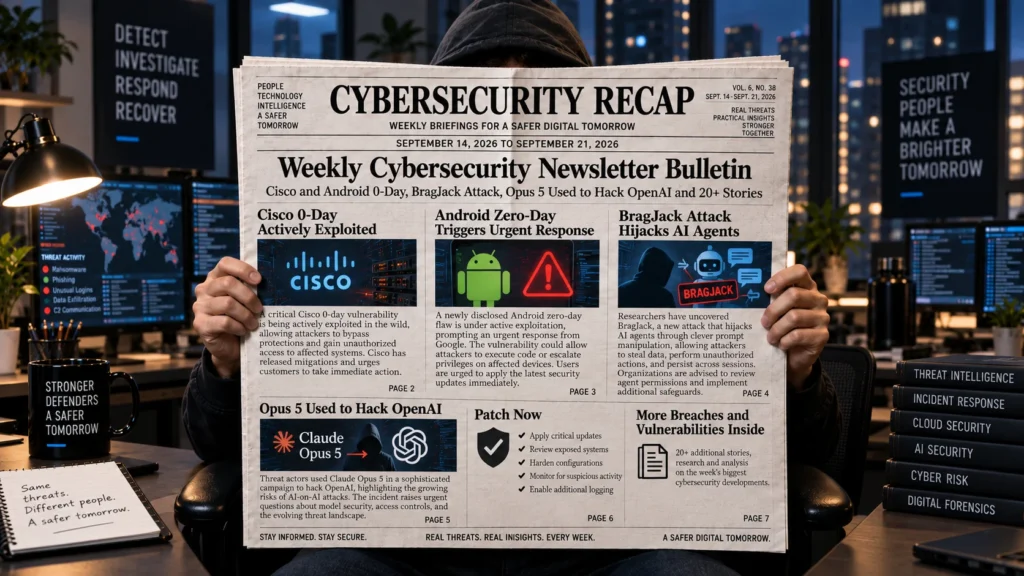
This week’s roundup covers a maximum-severity Cisco ISE zero-day under active exploitation, an actively exploited Android modem flaw on Pixel devices, a browser-extension attack that hijacks AI agents across five browsers, and researchers using Claude Opus 5 to compromise OpenAI’s forum and reach its internal source code. Also inside: a WordPress one-click RCE chain, an […]
CISA Warns of Linux Kernel Vulnerabilities Actively Exploited in Attacks
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has warned that attackers are actively exploiting three Linux kernel vulnerabilities, creating an urgent patching and investigation deadline. CISA added CVE-2025-39682, CVE-2026-53266, and CVE-2025-39964 to its Known Exploited Vulnerabilities catalog on September 18, 2026, with remediation required by September 21 under Binding Operational Directive 26-04. The KEV […]
TanStack Supply Chain Attack Lets Hackers Steal 170 Private CrowdSec GitHub Repositories
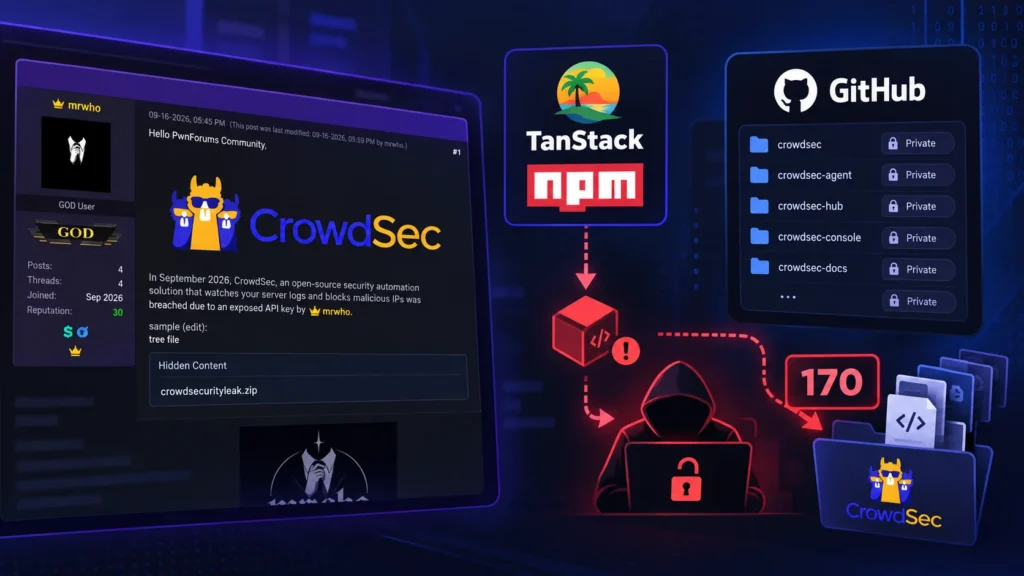
CrowdSec has disclosed that attackers copied about 170 private GitHub repositories after a former employee’s account was compromised through May’s TanStack npm supply chain attack. The May 22 theft remained undetected until stolen source code appeared on a cybercrime forum on September 16, showing how a poisoned dependency can outlive its infection window and undermine […]