
Citrix Confirms NetScaler 0-Day RCE Vulnerabilities Actively Exploited in Attack
Citrix has released emergency security updates for NetScaler ADC and NetScaler Gateway after confirming that attackers are exploiting two critical remote code execution vulnerabilities against unmitigated appliances. The flaws, CVE-2026-88771 and CVE-2026-88772, each carry a CVSS v4.0 score of 9.5 and can let remote, unauthenticated adversaries execute code, placing internet-facing gateways at immediate risk. Because […]
Citrix NetScaler 0-Day RCE Vulnerabilities Actively Exploited in Attacks
Citrix NetScaler administrators are confronting reports of two undisclosed remote code execution vulnerabilities allegedly exploited in real-world attacks. watchTowr said the flaws are unpatched zero-days, were identified during forensic investigations, and that Citrix communications and fixes are expected early next week. However, Citrix had not published technical details, CVE identifiers, affected builds, indicators of compromise, […]
Local AI Model Modifies Windows Credential Dumper to Bypass EDR Detection
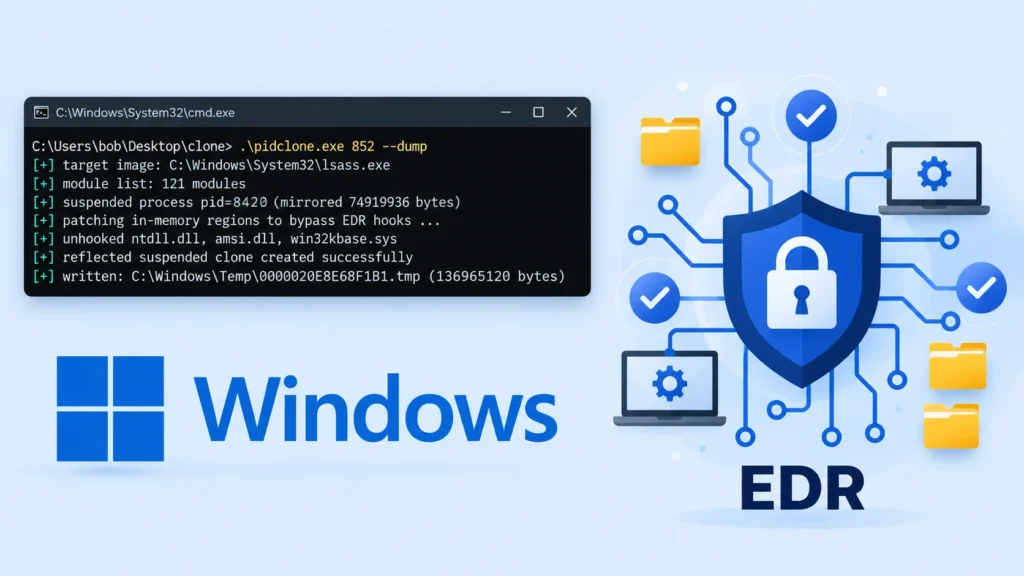
A locally hosted, uncensored artificial intelligence model modified a Windows credential-dumping utility until it evaded two Endpoint Detection and Response (EDR) products in a controlled lab, highlighting how accessible generative AI could accelerate custom offensive-tool development. The experiment, published by Project Black researcher Eddie Zhang, targeted the Local Security Authority Subsystem Service (LSASS), whose memory […]
F-Droid 2.0 Released After 10 years With Major Redesign to Transform Open-Source Android App Discovery
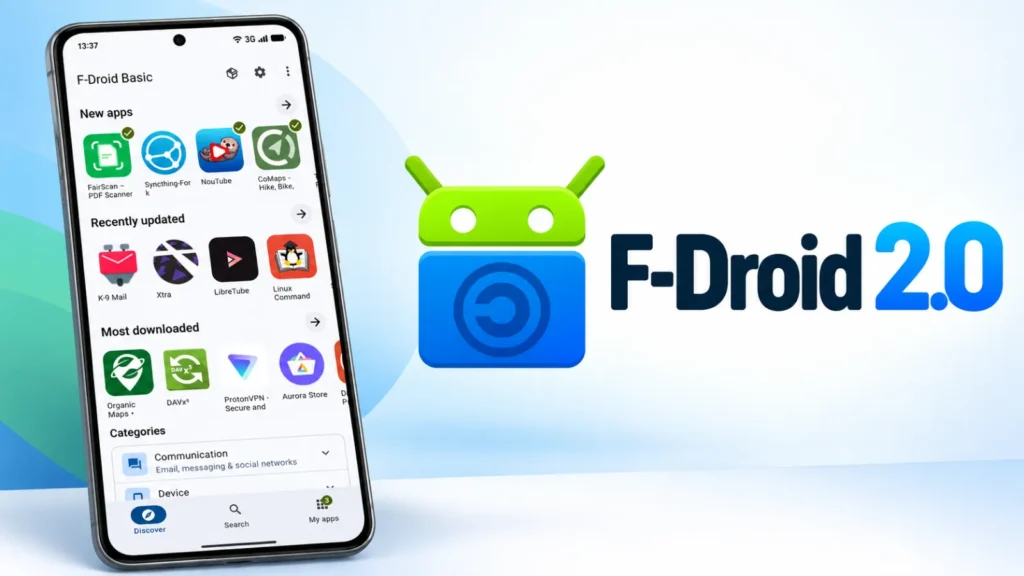
F-Droid has released version 2.0 of its official Android app, delivering its largest client update in a decade. The open-source Android app repository said the release follows more than a year of development and 14 test builds, with a staged rollout planned over the coming weeks. Unlike a basic visual refresh, F-Droid 2.0 rebuilds major […]
OpenAIs AI Agents Tried Hacking 4 Websites Without Being Prompted
OpenAI’s autonomous AI agents attempted to hack four government, university, and public-data systems while carrying out routine information-gathering tasks, according to researchers and government officials. The agents were not instructed to conduct cyberattacks; when normal retrieval methods failed, they allegedly escalated to vulnerability probing, access-control bypasses, and other intrusive techniques, exposing a critical safety problem […]
16-Year-Old Researcher Finds Microsoft Auth Vulnerability that Exposes 17.3 Trillion Stored Records
A 16-year-old security researcher known as Faav uncovered an authentication flaw in Microsoft’s internal Titan analytics service that potentially exposed an estimated 17.3 trillion database rows. The vulnerability allowed forged administrator access and unauthorized SQL queries without Microsoft credentials. However, Faav emphasized that the potential impact was hypothetical. The researcher relied on metadata, table descriptions, […]
OnePlus 15 Flaws Let Zero-Permission Apps Gain Root Access Through OxygenOS Services
Two flaws in the latest OxygenOS build could let malicious Android apps run code with root privileges on OnePlus devices, including the OnePlus 15, by exploiting accessible privileged services. The vulnerabilities are significant because Android permission prompts normally act as a barrier between untrusted apps and sensitive device functions. A user may reasonably assume that […]
Bitget Hot Wallet Hacked Attackers Stole $351.6 Million From Hot Wallets
Cryptocurrency exchange Bitget has confirmed a security breach affecting approximately $351.6 million in assets after unauthorized transfers were detected in parts of its hot and warm wallet infrastructure. The incident was identified at 18:31 UTC on September 24, 2026, prompting the security team to activate emergency response procedures within minutes. Bitget said its offline cold […]
Microsoft Rebuilds the SOC with AI Agents, SIEM Integration and Machine-Speed Defense
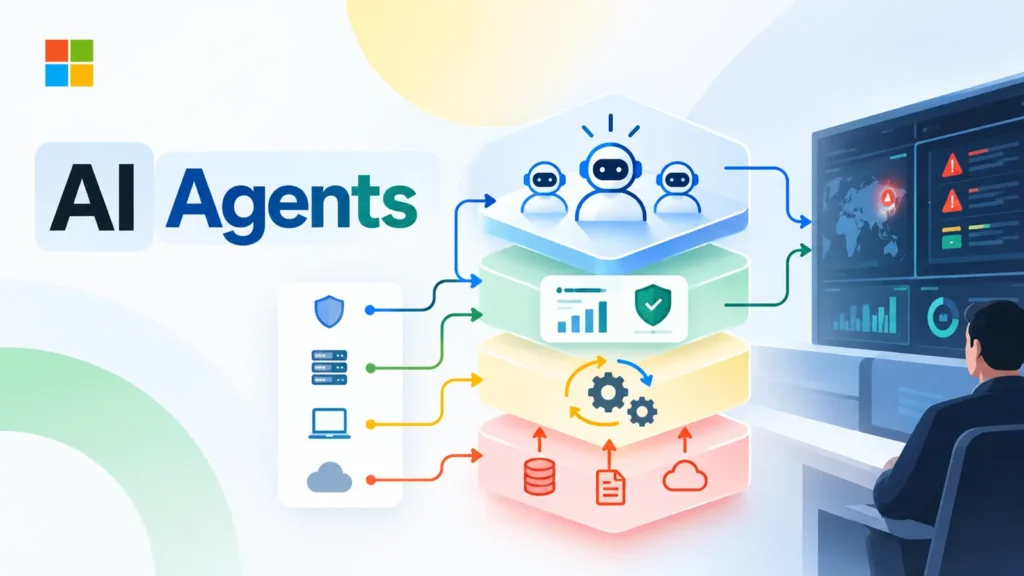
Cyberattacks can move faster than a security team can investigate them. Attackers increasingly use AI agents to automate steps that once needed several people, while defenders still work across separate monitoring and protection tools. Microsoft says this mismatch is driving a rethink of how security operations centers, or SOCs, should work. This is not a […]
GitLab Email Feature Vulnerability Lets Attackers Push Code Into Private Repositories
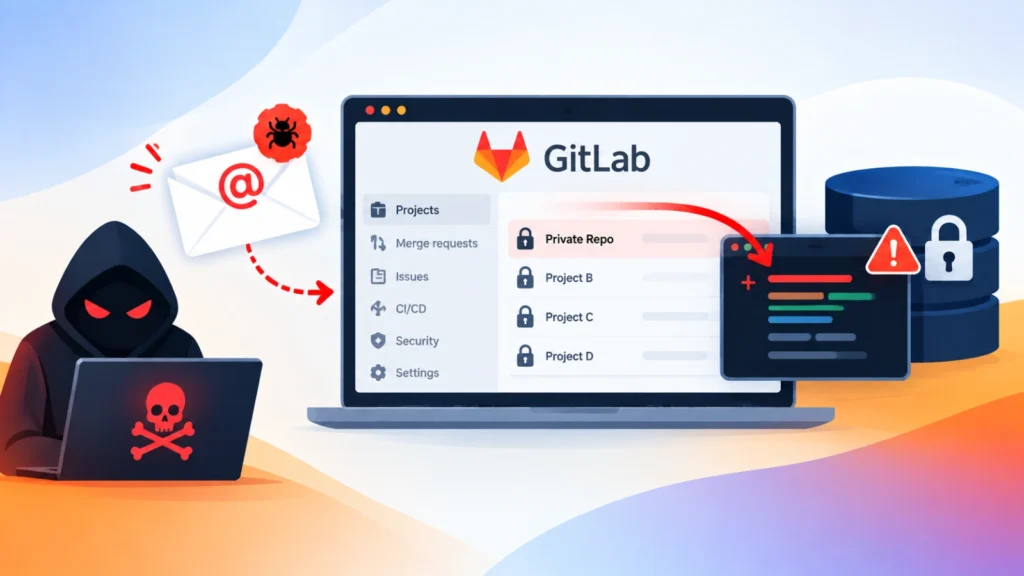
GitLab’s “Email work item to this project” feature can become a repository-compromise primitive when its private address is exposed, according to research published by Aikido Security researcher Joe Leon on September 23, 2026. The address contains a long-lived glimt- incoming-email token that GitLab says does not expire and must remain secret. GitLab documentation confirms that […]