
Critical WordPress RCE Vulnerability Allows Authors to Execute Code via Malicious PNG File
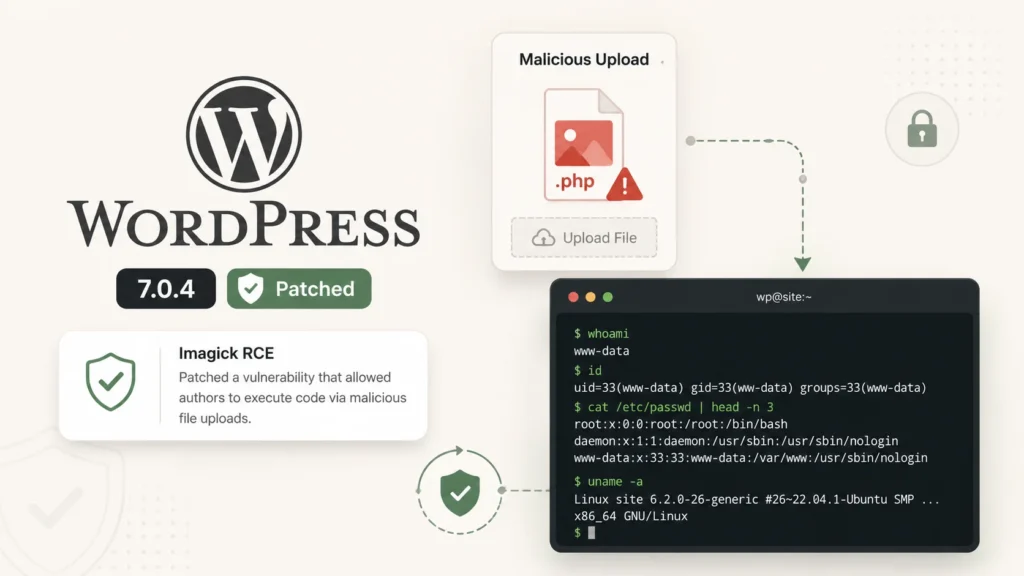
WordPress has released version 7.0.4, a security-focused update that closes a remote code execution vulnerability affecting sites that process images with the Imagick extension and Ghostscript. The WordPress security team is urging site owners to update immediately, either through the Dashboard’s Updates screen or by downloading the release directly from WordPress.org, since sites with automatic […]
Nightmare-Eclipse Drops ShieldBreak Windows Defender 0-day Vulnerability
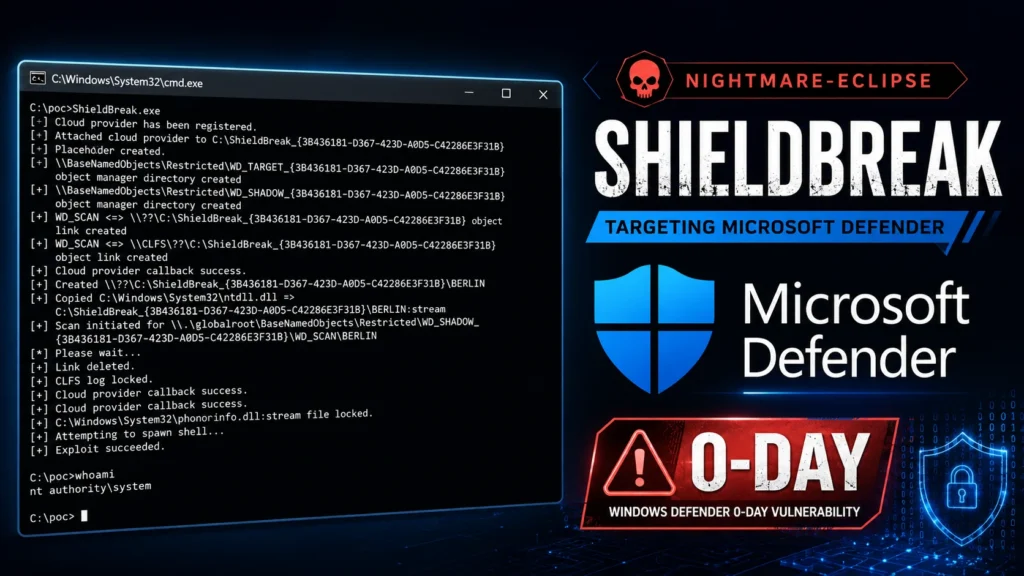
The prolific and controversial security researcher known as Nightmare-Eclipse (also tracked under the alias Chaotic Eclipse) has released a ninth Windows zero-day exploit called ShieldBreak, and this time the target is Microsoft’s own fix. ShieldBreak demonstrates a complete bypass of the patch Microsoft shipped for RoguePlanet, the Windows Defender elevation-of-privilege flaw tracked as CVE-2026-50656, proving […]
Microsoft Outlook Vulnerability Allows Attackers to Execute Malicious Code Remotely
Microsoft has disclosed a new remote code execution flaw in Outlook, tracked as CVE-2026-70329, as part of its August 2026 Patch Tuesday rollout. The vulnerability stems from an integer overflow or wraparound weakness in Microsoft Office Outlook, and it carries a CVSS v3.1 base score of 8.8, placing it in the High severity band. Microsoft’s […]
Microsoft Patch Tuesday Update August 2026 394 Vulnerabilities Fixed, Including 3 Zero-Days
CVE-2026-72971 Windows Container Isolation FS Filter Driver (unionfs.sys) Tampering Vulnerability Important CVE-2026-71331 Windows Device Health Attestation (DHA) Remote Code Execution Vulnerability Critical CVE-2026-70355 Microsoft SharePoint Server Elevation of Privilege Vulnerability Important CVE-2026-70354 .NET Core Remote Code Execution Vulnerability Important CVE-2026-70348 Windows Management Services Denial of Service Vulnerability Important CVE-2026-70347 Windows Installer Elevation of Privilege Vulnerability […]
Compromised FortiGate VPN Opens First Step in Multi-Network Polish Energy Attack
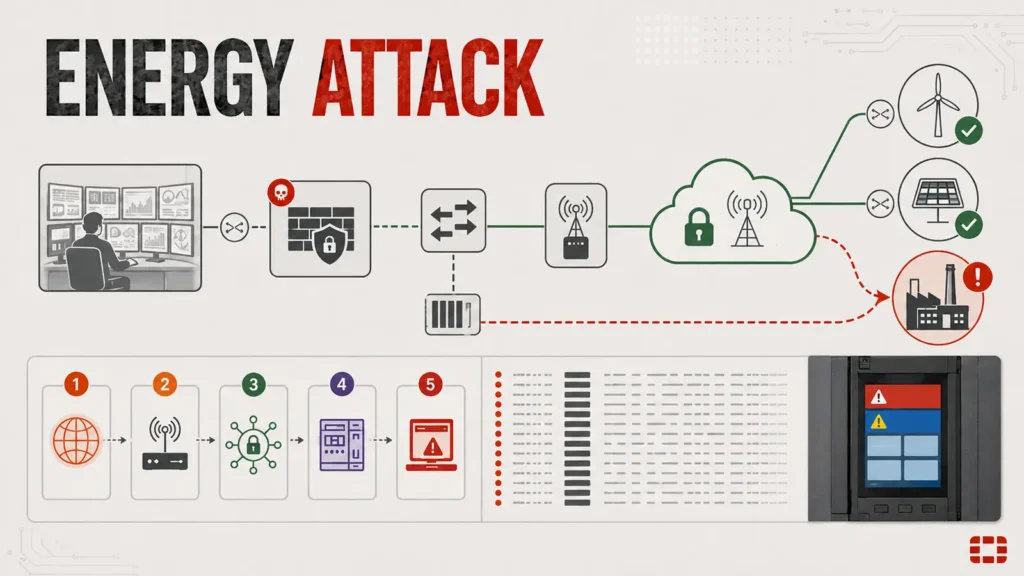
Poland’s energy sector attack has revealed how one compromised remote-access device can become the first step in a wider industrial intrusion. The campaign moved from a wind-farm network into a heat and power plant, turning trusted connectivity into disruption. The incident occurred on 29 December 2025, alongside coordinated destructive attacks against more than 30 renewable […]
OpenAI Expands Daybreak Cyber with GPT-5.6 for Exploit Validation, Pentesting, and Red Teaming
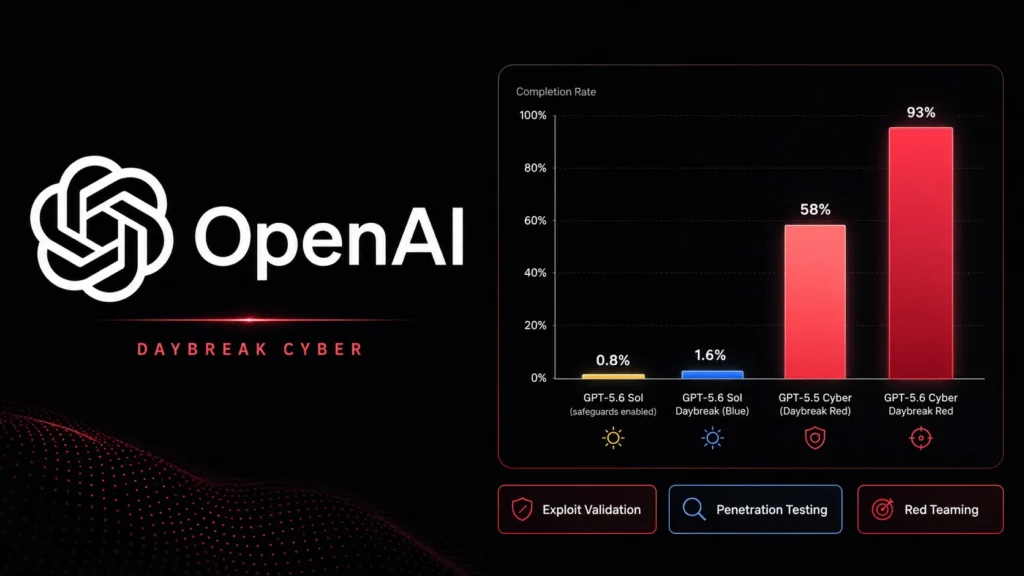
OpenAI has expanded its Daybreak program to give vetted security defenders deeper access to frontier AI models, introducing two access tiers—Daybreak Blue and Daybreak Red—alongside a new specialized model, GPT-5.6-Cyber, purpose-built for exploit validation, vulnerability research, and red teaming. The move is a direct response to a widening gap between attacker and defender capabilities, as […]
Gunra Ransomware Exploits Fortinet VPN Flaws to Bypass MFA and Steal Enterprise Data
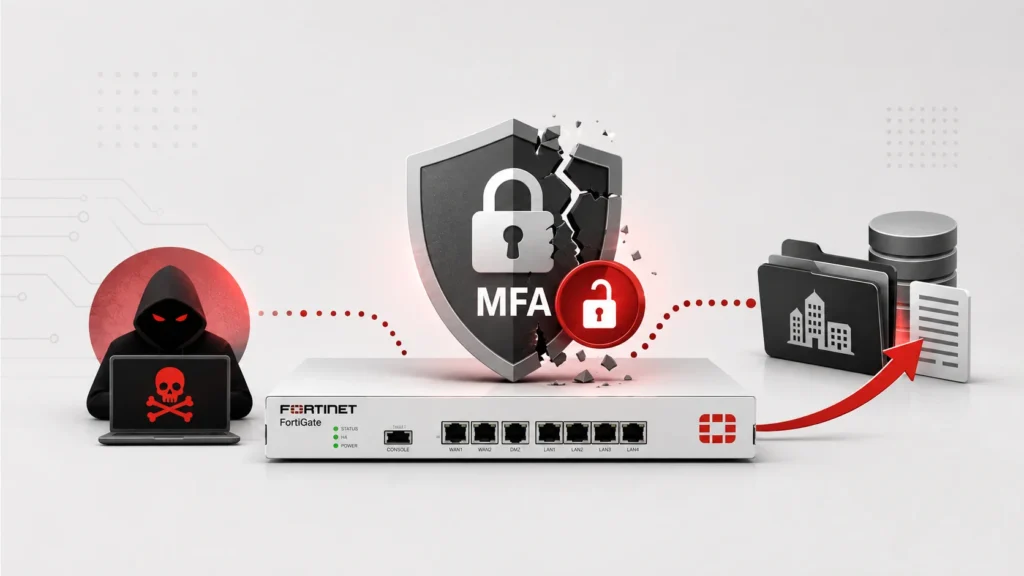
A joint cybersecurity advisory from the FBI, CISA, the Department of Defense Cyber Crime Center, the NSA, the U.S. Secret Service, and South Korea’s National Police Agency has exposed a dangerous new wave of attacks by the Gunra ransomware group, which is actively exploiting known Fortinet VPN vulnerabilities to bypass multi-factor authentication and exfiltrate sensitive […]
Apple Private Cloud Compute Flaw Enables Root File Writes and AI Inference Telemetry Leakage
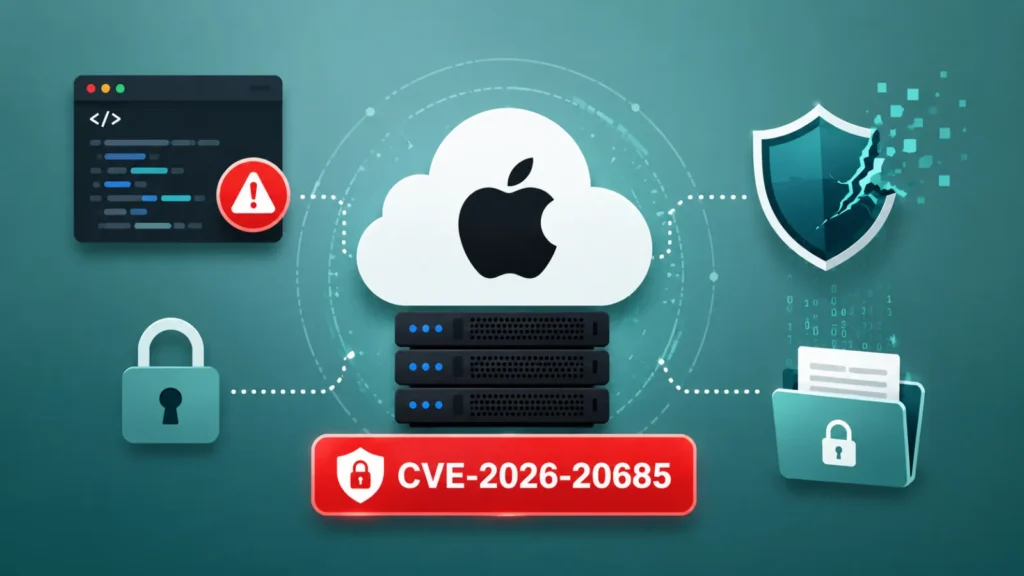
CVE-2026-20685 is a path traversal vulnerability affecting Apple’s Private Cloud Compute (PCC), potentially allowing attackers to write files as root during node boot and redirect sensitive AI inference telemetry to an external server. Sentry Security researcher Drinor received a $150,000 Apple Security Bounty for discovering and reporting CVE-2026-20685, a flaw that could expose sensitive data […]
Weekly Cyber Security Newsletter OWASP Top 10 for LLM, Cisco IOS XE Flaw, and 1-Click Cursor RCE +20 Stories
This week’s roundup covers active exploitation of Apache Tomcat and SonicWall SMA, a nearly two-decade-old Linux kernel flaw, critical bugs in N-able N-Central, Veeam ONE, Jenkins, and Cisco IOS XE, plus a wave of AI-security incidents touching Claude, Kimi K3, and code editors like Cursor and VS Code. CISA Warns of Apache Tomcat Encryption Flaw […]
Levi Strauss Data Breach Hackers Gained Access to the Companys Systems
Levi Strauss & Co., the denim giant, reported a cybersecurity incident where an unauthorized third party accessed the company’s internal systems via a targeted social engineering attack. According to a regulatory filing submitted to the U.S. Securities and Exchange Commission, the attackers manipulated three employees into surrendering access to their company-issued computers, ultimately allowing the […]