
Top 10 Best Active Directory Management Tools 2026
Managing Active Directory with native tools alone can become time-consuming as an organization grows. Routine tasks such as provisioning users, resetting passwords, managing group memberships, auditing permissions, and maintaining compliance can place a heavy burden on IT teams. Manual processes also increase the risk of configuration errors, excessive privileges, security gaps, and inactive accounts going […]
GitLab Vulnerabilities Allow Attackers to Execute Remote Code on Default GitLab Installations
A newly disclosed exploit chain in GitLab shows how two long-buried memory-safety flaws in a Ruby JSON parsing library, Oj, could be combined to achieve remote code execution on default GitLab installations, exposing source code, Rails secrets, and internal services. As part of the Open Defense Initiative, Depthfirst researcher Yuhang Wu used the automated analysis […]
Researcher Claims Working Jailbreak on Top AI Models Including GPT-5.6, Claude Opus 5, and Fable
A well-known AI red teamer claims to have developed a universal jailbreak that works against leading large language models, including heavily guarded flagships such as GPT-5.6 Sol, Claude Opus 5, and Fable. In a public post on X, Pliny the Liberator described the technique as effective “on ALL models” and across every category he tested. […]
Foxit Updater Vulnerability Gives Standard Users SYSTEM-Level Control of Windows Devices
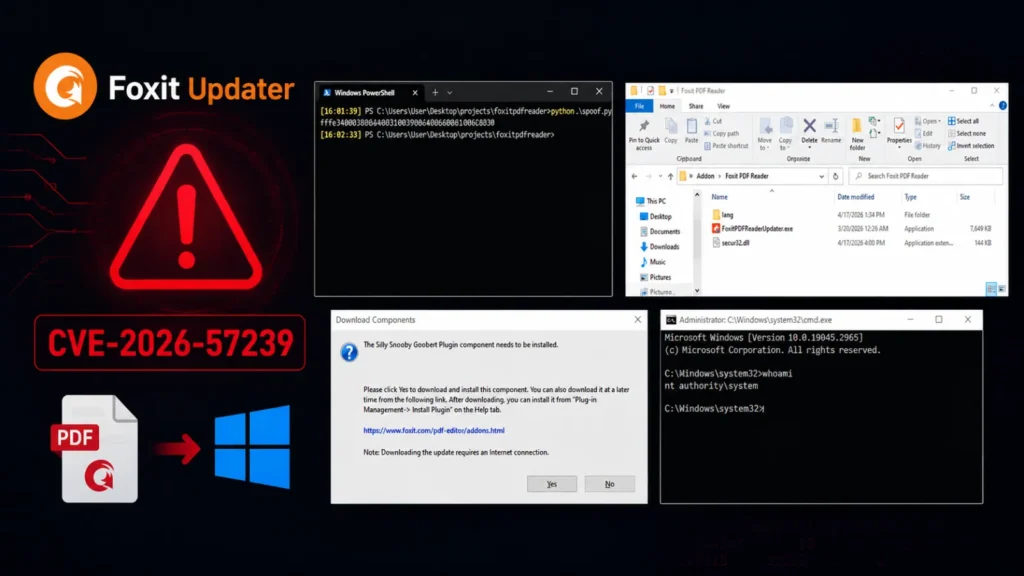
Foxit PDF Reader has been found vulnerable to a local privilege escalation flaw that allows standard Windows users to gain full SYSTEM-level control under specific conditions. The issue, tracked as CVE-2026-57239, was disclosed following research into Foxit’s updater and service architecture and represents a high-impact post-exploitation pathway, although it requires prior code execution on the […]
Certighost Active Directory CS Exploit Allows Low-Privileged Users to Compromise Domain
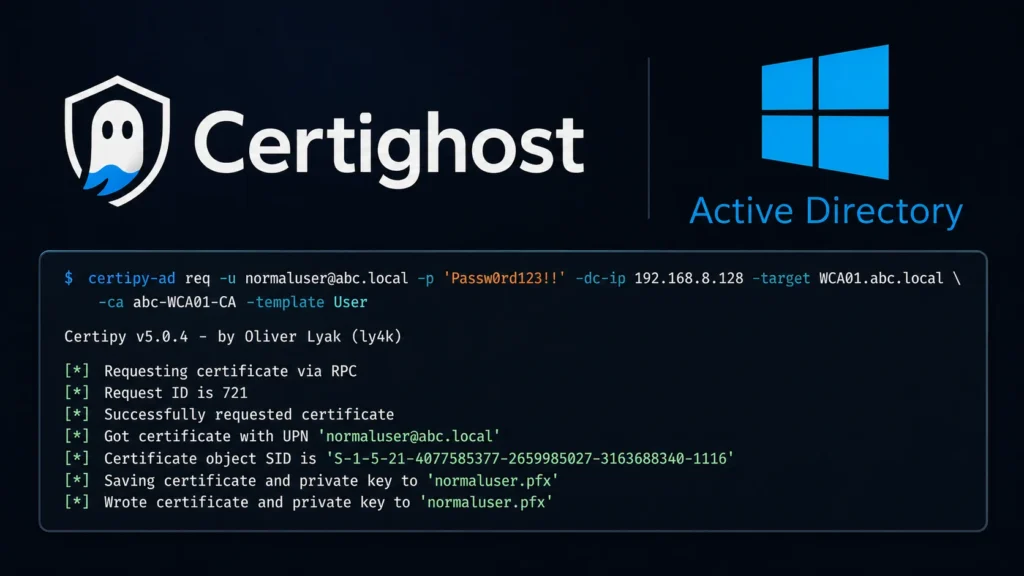
A newly disclosed Active Directory Certificate Services (AD CS) vulnerability, dubbed Certighost, allowed a low-privilege domain user to impersonate a Domain Controller and take over an entire Active Directory domain. Tracked as CVE-2026-54121, the flaw was patched in Microsoft’s July 2026 security updates following responsible disclosure earlier this year. AD CS is Microsoft’s public key […]
Apache Syncope Release Patches for Multiple RCE and SQL Injection Vulnerabilities
Apache has issued critical security updates for its Syncope identity and access management (IAM) platform to address multiple vulnerabilities, including remote code execution (RCE), SQL injection, privilege escalation, server-side request forgery (SSRF), and information disclosure. These flaws affect various versions of Syncope, and administrators are strongly urged to upgrade promptly to the latest secure releases. […]
Hackers Allegedly Claim Breach of Decathlon Customer Database With 160 Million Records
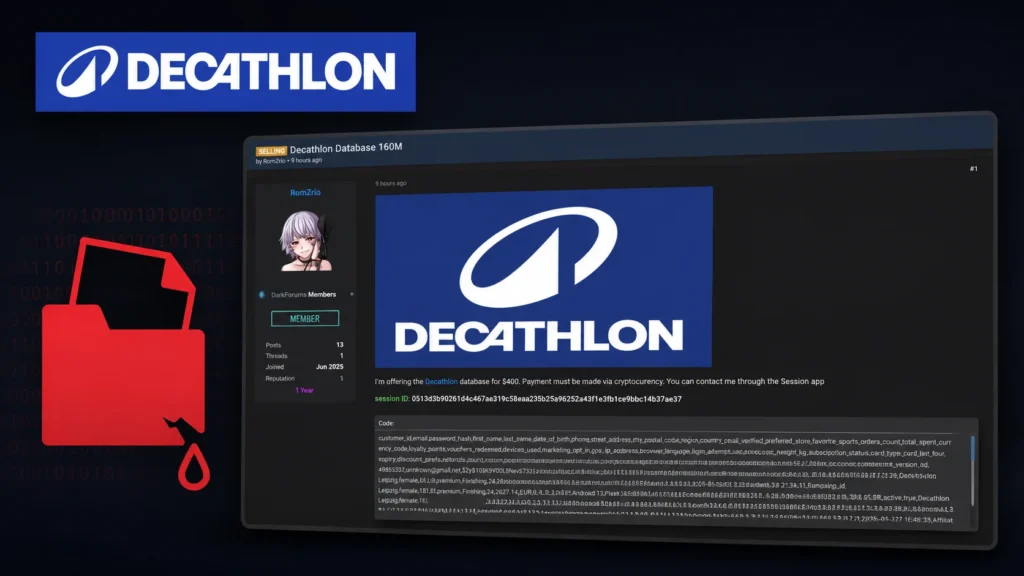
A threat actor is allegedly claiming to possess and sell a Decathlon customer database containing approximately 160 million records. The database was advertised on a cybercrime forum, where the seller stated that payment would be accepted through cryptocurrency. The alleged breach has not been independently verified, and Decathlon has not publicly confirmed that its systems […]
Hackers Abuse Notepad++ Plugins to Compromise Your System Silently
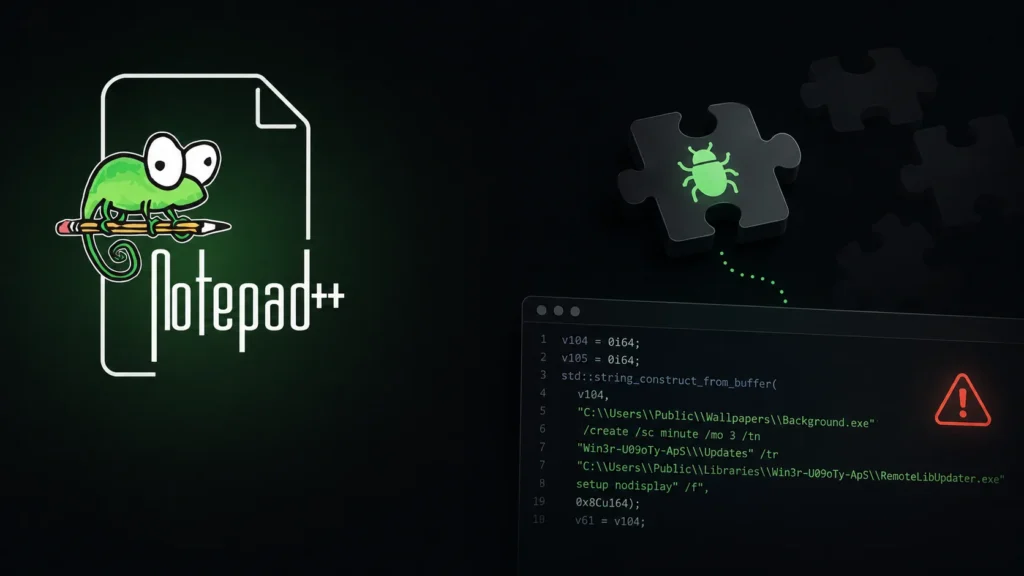
A stealthy new campaign in which the UAC-0099 threat cluster hijacks a legitimate Notepad++ plugin to quietly plant malware on victim machines, marking a significant evolution in the group’s tactics since mid-summer 2026. Uncovered by Ukraine’s CERT-UA, the infection begins with a phishing email carrying an image that links, via a URL-shortening service, to a […]
Anthropic Launches Claude Security Plugin to Scan Code for Vulnerabilities
Anthropic has released the Claude Security plugin in beta, bringing AI-powered vulnerability scanning directly into Claude Code for developers who want to catch high-severity flaws before they ship. The tool lets teams scan recent changes or full repositories from the terminal, using the same Claude inference they already run. The Claude Security plugin works inside […]
RefluXFS Linux Kernel Vulnerability Lets Attackers Gain Root Access
A new Linux vulnerability dubbed “RefluXFS” is a race condition in the Linux kernel’s XFS filesystem copy-on-write path that lets an ordinary local user silently overwrite protected system files and seize host root privileges, even on systems running SELinux in Enforcing mode. The vulnerability tracked as CVE-2026-64600 uncovered by Qualys Threat Research Unit (TRU) exploits […]