
Moody Bible Institute Data Breach Exposes 2.3 Million Users Personal Data
Moody Bible Institute has confirmed a significant data breach after threat actors linked to the ShinyHunters extortion group published personal information belonging to over 2.3 million individuals. The exposed dataset includes donors, supporters, students, and alumni associated with the institute. In June 2026, Moody Bible Institute became the target of a ShinyHunters “pay or leak” […]
T3MP3ST Security Framework With 35 Tools, Turns AI Coding Agents Into 0-Day Bug Hunters
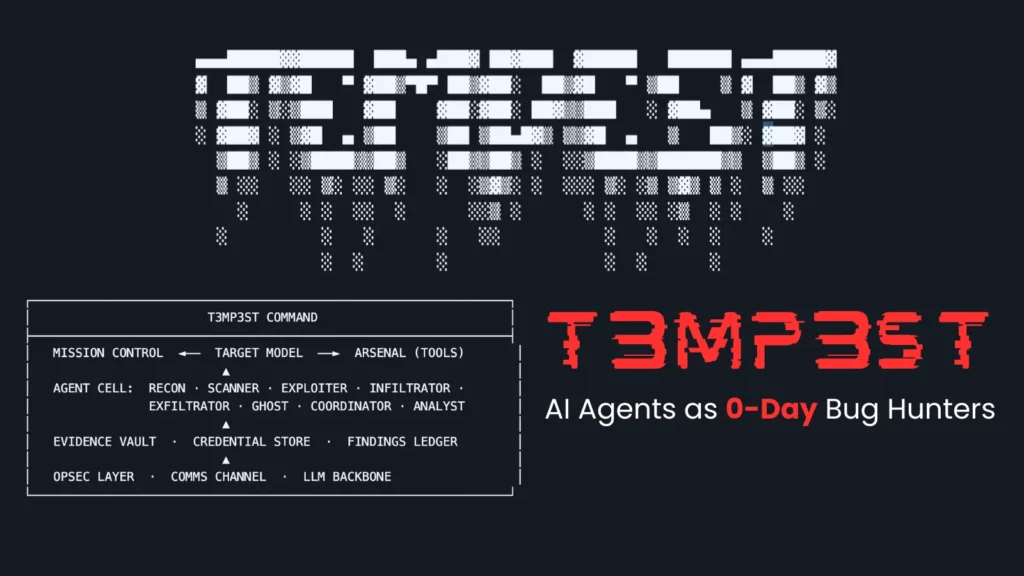
A newly released open-source security framework called T3MP3ST is turning general-purpose AI coding agents like Claude Code, OpenAI’s Codex, and Hermes into autonomous red-teaming operators without requiring new API keys, cloud infrastructure, or additional billing. Built by researcher elder-plinius, T3MP3ST acts as a multi-agent orchestration layer rather than shipping its own model, coordinating multiple agent […]
Flipper Zero Firmware Development Continues With New Community Contribution Rules
Flipper Devices has responded to intense community backlash over perceptions that it had abandoned active development of the Flipper Zero firmware. In a statement addressing the controversy, the company announced it will allocate dedicated resources to firmware maintenance while overhauling how it engages with contributors and feature requesters. The Flipper Zero project launched via Kickstarter […]
Microsoft Releases OOBE Cumulative Update for Windows 11, Versions 24H2 and 25H2
Microsoft has rolled out KB5095189, a new cumulative update targeting the Out-of-Box Experience (OOBE) for Windows 11, versions 24H2 and 25H2. Released on June 23, 2026, this update refines the initial setup flow that users encounter when configuring a new or freshly reset Windows 11 device, rather than touching the core operating system components. KB5095189 […]
PamStealer Mimics Maccy Clipboard Manager Silently Harvests Data and Clipboard Contents
PamStealer is a newly identified macOS infostealer that disguises itself as the popular open-source clipboard manager “Maccy” while silently harvesting sensitive user data. Discovered by Jamf Threat Labs, the malware uses a stealthy two-stage infection chain designed to evade detection and blend into normal macOS activity. The attack begins with a malicious disk image file […]
Multiple FatFs Vulnerabilities Expose Millions of Embedded Devices to Cyber Risks
Security researchers at runZero have disclosed seven new CVEs affecting FatFs, the ubiquitous lightweight FAT/exFAT filesystem driver used across embedded and IoT ecosystems. The vulnerabilities range from CVSS Medium to High, with no Critical-rated findings, but their reach is significant: FatFs underpins platforms including Espressif ESP-IDF, STMicroelectronics STM32Cube, Zephyr RTOS, MicroPython, ArduPilot, RT-Thread, Mbed, Samsung […]
New Bad Epoll 0-Day Vulnerability Allows Root Access on Linux Servers and Android Devices
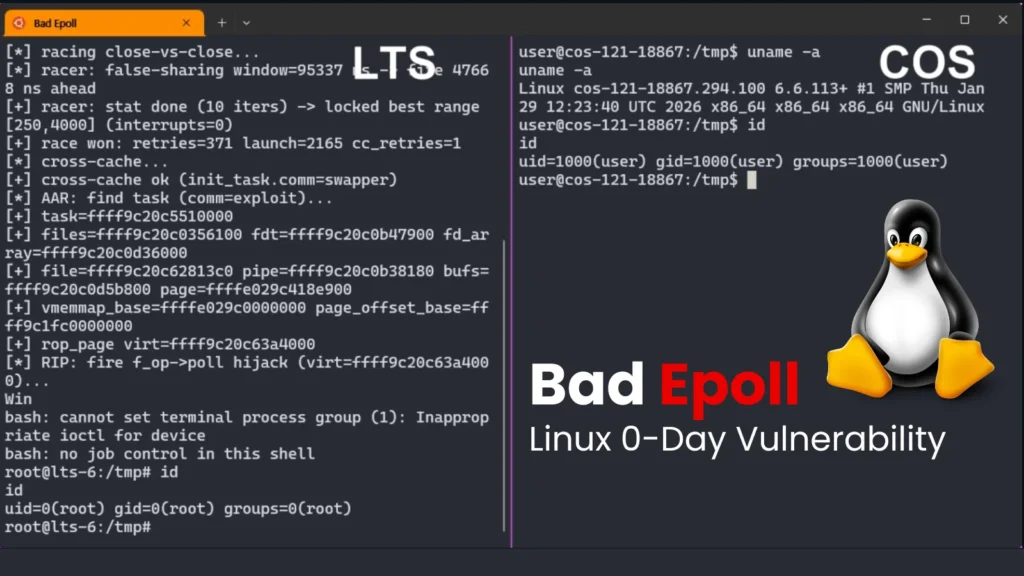
A newly disclosed Linux kernel flaw dubbed “Bad Epoll” (CVE-2026-46242) allows an unprivileged local user to escalate to root on Linux servers, desktops, and Android devices by exploiting a race condition and a use-after-free (UAF) in the kernel’s epoll subsystem. Bad Epoll is a UAF vulnerability in ep_remove(), which clears file->f_ep under file->f_lock but continues […]
Indian Govt Bans Apps Being Misused to Stop E-Rickshaws Remotely
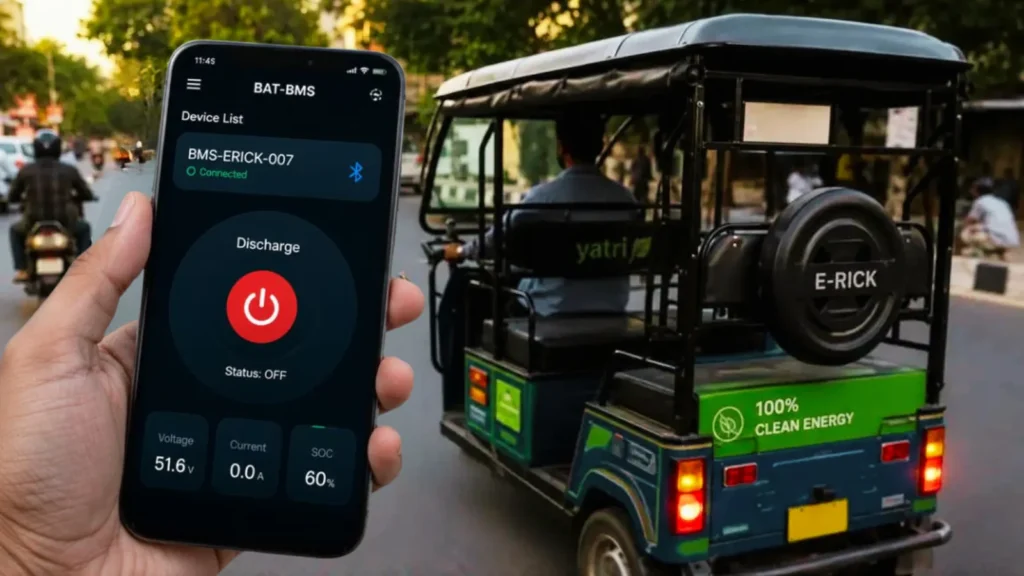
The Indian government has directed Google and Apple to take down three mobile applications, BAT-BMS, Lossigy, and Epoch-i-ion, after they were allegedly misused to remotely disable e-rickshaws and other battery-operated three-wheelers mid-journey, putting passenger safety at risk. Authorities have also warned that any additional apps found to enable similar remote-kill functionality will face the same […]
Hackers Use Fake Cisco AnyConnect and Google Update Installers to Drop SharkLoader
Cybersecurity researchers have uncovered a new malware loader called SharkLoader that is quietly slipping into networks by hiding inside fake software installers. The tool has been spotted delivering Cobalt Strike Beacon, a well known post exploitation framework, onto compromised machines. The campaign blends old fashioned trickery, disguising malware as trusted programs, with advanced evasion engineering […]
Anthropic Details Claude Fable 5 Cybersecurity Safeguards and Jailbreak Framework
Anthropic has published detailed technical documentation on the cybersecurity safeguards protecting Claude Fable 5, following the model’s global redeployment. The disclosure covers both the AI’s safety classifier system and a draft framework for grading jailbreak severity, developed in partnership with Glasswing. Fable 5’s safety classifiers sort cybersecurity requests into four categories rather than blocking all […]