
Anthropic Details Claude Fable 5 Cybersecurity Safeguards and Jailbreak Framework
Anthropic has published detailed technical documentation on the cybersecurity safeguards protecting Claude Fable 5, following the model’s global redeployment. The disclosure covers both the AI’s safety classifier system and a draft framework for grading jailbreak severity, developed in partnership with Glasswing. Fable 5’s safety classifiers sort cybersecurity requests into four categories rather than blocking all […]
AsyncRAT Campaign Uses DLL Sideloading and ScreenConnect for Stealthy Remote Access
A stealthy campaign is turning trusted remote access software into a weapon against everyday users and businesses. Attackers have hidden the AsyncRAT trojan inside fake software installers, letting it slip past basic security checks. The campaign relies on DLL sideloading and a legitimate remote tool called ScreenConnect, making it hard for victims to notice anything […]
Critical JetBrains Vulnerabilities Enable Authentication Bypass and Code Execution Attacks
JetBrains has released security updates for a cluster of critical vulnerabilities that enable authentication bypass, account takeover, and remote code execution (RCE) across its on‑premise ecosystem, including Hub, YouTrack, IntelliJ‑based IDEs, Kotlin, GoLand, and TeamCity. These flaws put development and CI/CD environments at direct risk of compromise if organizations delay patching. The most severe issues […]
WhatsApp Username Reservations Go Live What Are the Security Concerns for 2 Billion Users
WhatsApp has begun allowing users to reserve usernames ahead of a broader feature launch planned for later this year, prompting a wave of questions about security, impersonation risk, and account linkage that security researchers should be tracking closely. According to WhatsApp, usernames are optional, not mandatory, meaning existing phone-number-based identification remains the default authentication and […]
Indian Govt Halts Metas WhatsApp Usernames Rollout Over Fraud Concerns
The Indian government has issued a formal notice to WhatsApp LLC (Meta), directing the platform to justify why regulatory action should not be taken against its newly announced “usernames” feature and instructing the company not to roll it out in India until consultations are satisfactorily concluded. The letter, addressed to WhatsApp’s Chief Compliance Officer for […]
Multiple Citrix NetScaler ADC and Gateway Vulnerabilities Enables DoS and Memory Overflow Attacks
Multiple high-severity vulnerabilities have been identified in Citrix NetScaler ADC and NetScaler Gateway, exposing affected systems to denial-of-service (DoS) and memory overflow attacks. The issues, tracked under CVE-2026-8451, CVE-2026-8452, CVE-2026-8655, CVE-2026-10816, CVE-2026-10817, and CVE-2026-13474, were disclosed in a security bulletin published on June 30, 2026. According to Cloud Software Group, the vulnerabilities impact multiple supported […]
U.S. Lifts Export Controls on Claude Fable 5 and Mythos 5
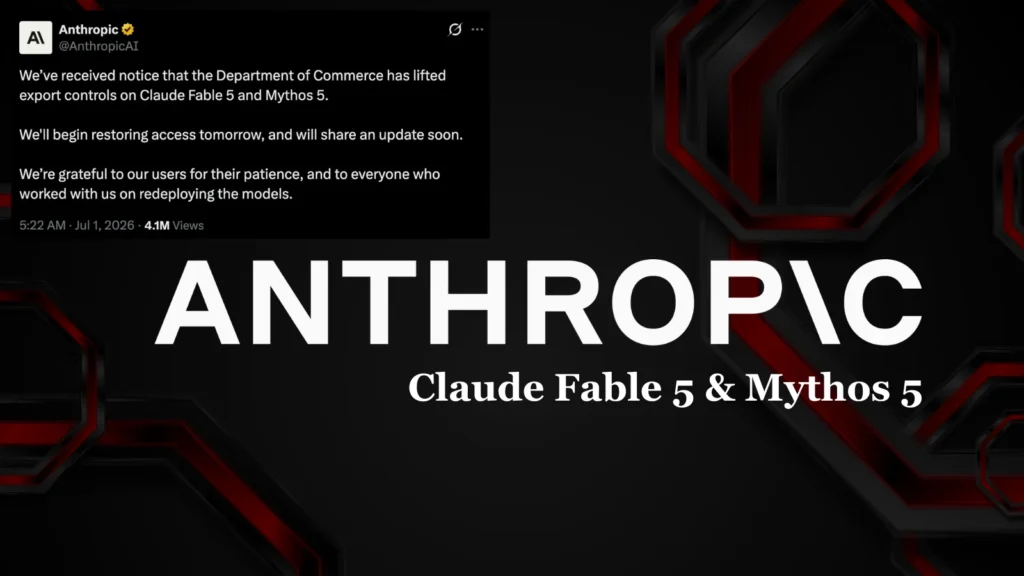
The U.S. Department of Commerce has formally withdrawn export control restrictions on Anthropic’s Claude Fable 5 and Mythos 5 AI models, ending an 18-day standoff that had blocked global access to the company’s most advanced systems. In a letter dated June 30, 2026, Commerce Secretary Howard Lutnick informed Anthropic’s Chief Compute Officer Tom Brown that […]
Anthropics Claude Code Reportedly Uses Hidden Code to Detect Chinese Users
A Reddit disclosure has ignited a serious debate about developer trust and covert surveillance, alleging that Anthropic embedded undisclosed detection logic inside its Claude Code CLI tool, specifically targeting users in China or those routing traffic through Chinese AI lab proxies. A Reddit user identified as LegitMichel777 on the r/ClaudeAI subreddit posted detailed findings on […]
GitHub Advisory Database Hits Record Volume as Vulnerability Reports Surpass Review Capacity
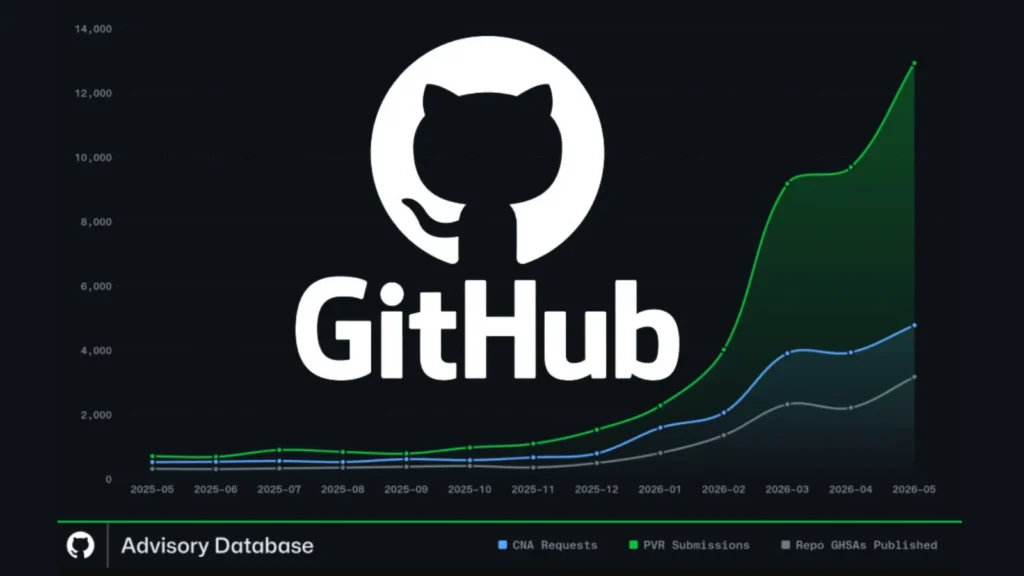
GitHub’s Advisory Database reached an all-time high in May 2026, publishing 1,560 reviewed security advisories, more than five times its typical monthly output. Despite this milestone, the platform still struggled to keep pace with a rapidly expanding volume of vulnerability reports, reflecting a broader shift in the global vulnerability disclosure ecosystem. According to GitHub, the […]
Nissan Confirms Data Breach Following Oracle PeopleSoft 0-Day Attacks
Nissan Americas has officially confirmed a data breach affecting current and former employees across four countries after threat actors exploited a critical zero-day vulnerability in Oracle PeopleSoft software, a campaign attributed to the ShinyHunters extortion group. The attack stems from CVE-2026-35273, a CVSS 9.8-rated unauthenticated Server-Side Request Forgery (SSRF)-to-Remote Code Execution (RCE) vulnerability residing in […]