
WhatsApp Launches New Username Feature to Communicate Without Exposing Phone Numbers
WhatsApp introduces a new privacy update that lets users connect using unique handles, eliminating the need to share phone numbers with strangers or new group members. Earlier, we detailed that WhatsApp is preparing to roll out a long-anticipated username feature. Now WhatsApp has officially launched the ability to reserve usernames, marking one of the most […]
LLM-Generated Mythic Agents Enable Disposable Red-Team Tooling From Prompt to Deployment
Red teamers and offensive security researchers have entered a new era where AI can write functional attack tools from a single sentence. A concept known as “disposable tooling” is now taking shape, and the implications for defenders are real. At the center of this shift is the ability to use large language models to build […]
RedAmon AI Tool that Chains Reconnaissance, Exploitation, and Post-exploitation
A new open-source offensive security platform called RedAmon is redefining automated penetration testing by chaining reconnaissance, exploitation, post-exploitation, AI-driven triage, and automated code remediation all into a single end-to-end pipeline that culminates in a GitHub pull request with the fix already written. RedAmon is a modular, containerized penetration testing framework built on Docker that requires […]
Anthropic Confirms Claude Mythos 5 Redeployment for US Critical Infrastructure Organizations
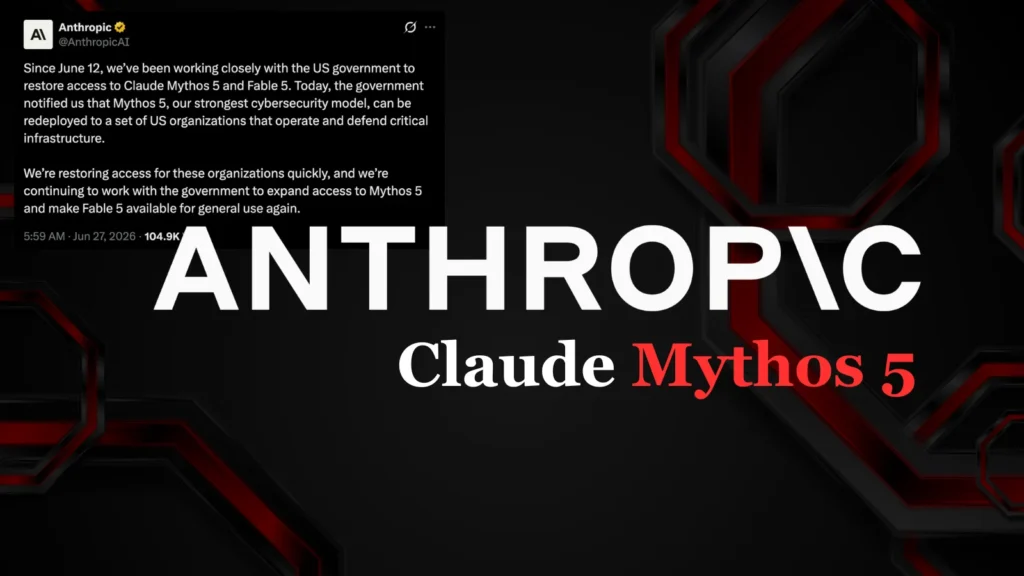
Anthropic has confirmed that Claude Mythos 5, its most powerful AI cybersecurity model, will be redeployed to a select set of U.S. organizations responsible for operating and defending critical infrastructure, following a government-led review process that began on June 12, 2026. Claude Mythos first made headlines in April 2026 when Anthropic described it as a […]
New Bucket Hijacking Attack Allows Hackers to Reroute Cloud Data Streams to External Storage
A critical cloud storage attack technique dubbed “bucket hijacking” a method that enables threat actors to silently redirect an organization’s active cloud data streams, including audit logs and telemetry, into attacker-controlled external storage buckets across major cloud platforms. The technique has been confirmed to affect Google Cloud, Amazon Web Services (AWS), and Microsoft Azure, with […]
New DirtyClone Linux Vulnerability Allows Attackers to Gain Root Access Via Cloned Packets
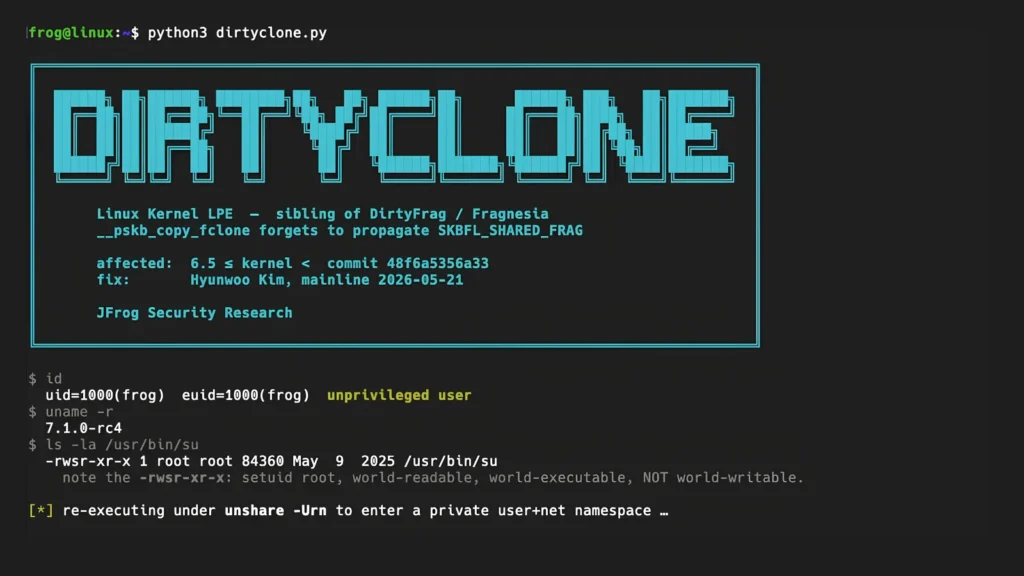
A new Linux kernel local privilege escalation vulnerability, dubbed “DirtyClone” (CVE-2026-43503), that allows unprivileged local users to gain full root access by manipulating cloned network packets through the XFRM/IPsec subsystem, all without leaving a trace in kernel logs or audit records. DirtyClone is a high-severity variant in the DirtyFrag vulnerability family, a class of Linux […]
Amazon Q Vulnerability Let Attackers Execute Code and Access Sensitive Cloud Environments
A high-severity vulnerability in the Amazon Q Developer Extension for Visual Studio Code (VS Code), Amazon’s AI-powered coding assistant. Tracked as CVE-2026-12957 and CVE-2026-12958 and disclosed by Wiz Research, the flaws allowed attackers to achieve arbitrary code execution and cloud credential theft simply by having a developer open a malicious repository. The root cause was […]
New Linux pedit COW Exploit Allows Attackers to Gain System Root Access
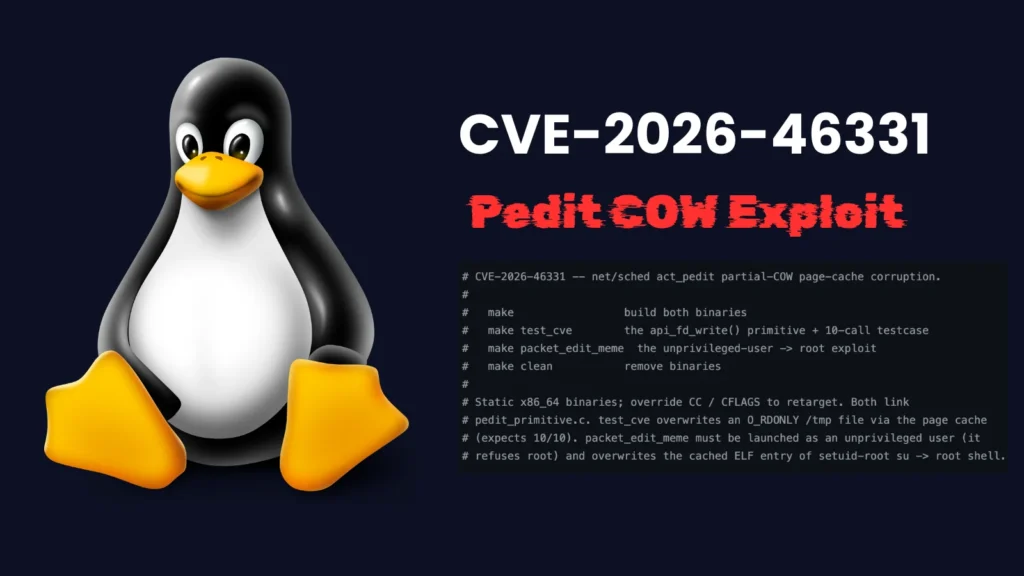
A newly disclosed Linux kernel vulnerability combining a Copy-on-Write (COW) page-cache corruption flaw with the net/sched subsystem’s act_pedit component is enabling unprivileged local attackers to escalate privileges to full root access on several major Linux distributions. The exploit, dubbed packet_edit_meme, has been verified in June 2026 against actively maintained enterprise and consumer kernels. The root […]
New Bluekit Phishing-as-a-Service Bypasses MFA to Steal Microsoft Login Credentials
A sophisticated Phishing-as-a-Service (PhaaS) platform called Bluekit has been confirmed operational at scale, with cybersecurity firm Netcraft detecting approximately 70 live hostnames in a single week. First documented by Varonis Threat Labs as an emerging tool still in development, Bluekit has since matured into a fully operational threat capable of bypassing multi-factor authentication (MFA) and […]
Hackers Leveraged Shopify Oder-Tracking App Shop to Push Fake Invoices
Hackers are no longer waiting in your inbox. A newly identified scam technique places fake invoices directly inside shopping app order histories, making them feel more credible than a typical phishing email. Researchers have observed fraudulent receipts appearing inside the Shop app, the popular order-tracking application from Shopify, catching users off guard in a space […]