
Microsoft has urged IT Admins to Prepare for Windows 11, Version 26H2 Update
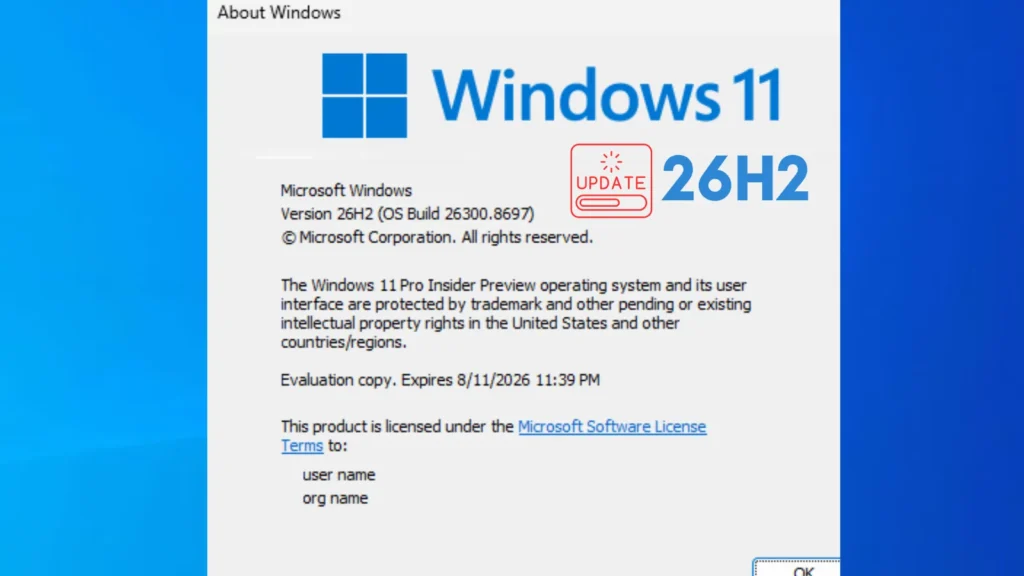
Microsoft has urged IT administrators to begin preparing for the upcoming Windows 11 version 26H2 update, which is now available for testing through the Windows Insider Program. The release continues Microsoft’s shift toward a predictable, low-disruption servicing model designed to simplify enterprise deployment and maintenance. Unlike traditional feature upgrades, Windows 11 version 26H2 uses the […]
GentleKiller Ransomware Abuses Vulnerable Drivers to Disable 400+ EDR Security Processes
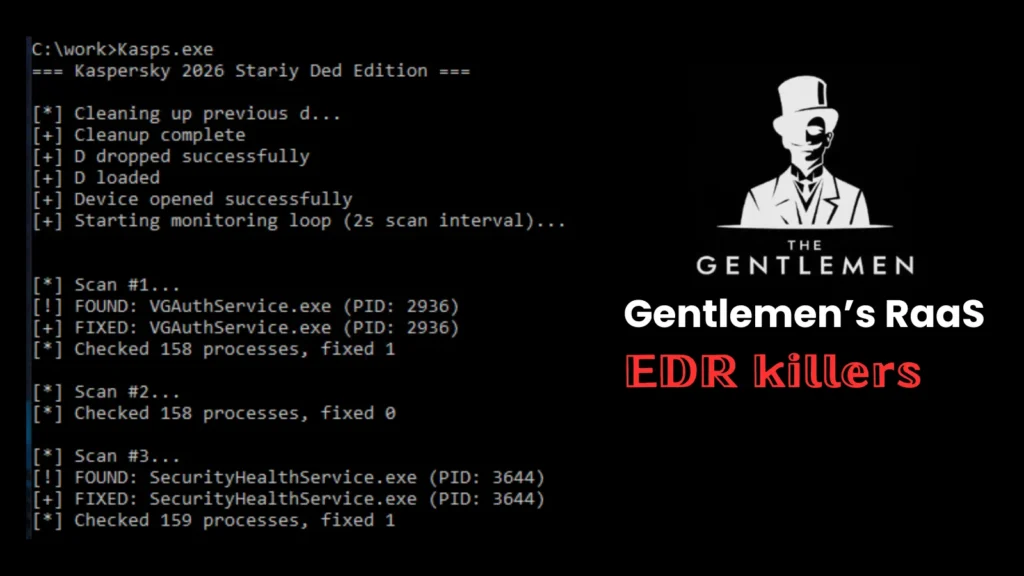
A highly sophisticated EDR-killing framework, dubbed GentleKiller, was used by the Gentlemen ransomware-as-a-service (RaaS) gang to systematically disable endpoint security tools before deploying its ransomware payload. The findings by ESET, published on June 17, 2026, detail how Gentlemen, one of the most active ransomware gangs in Q1 2026, provides affiliates with a centralized, operator-maintained suite […]
CyberSentinel AI with 33 Security Tools, Including Nmap, SQLMap, ZAP, and uses Claude, GPT
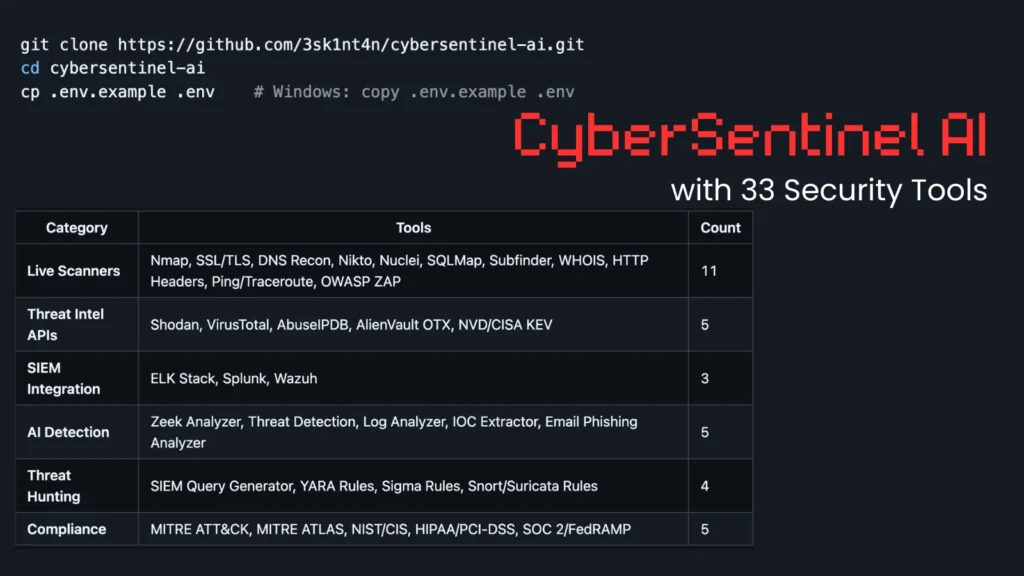
A new open-source cybersecurity platform called CyberSentinel AI v3.0 has emerged as a significant development in autonomous security tooling, combining 33 real-world penetration testing and threat intelligence tools with a provider-agnostic AI engine that supports Claude, GPT-4o, OpenRouter, and fully offline local inference via Ollama. Unlike conventional AI security assistants that just suggest commands, CyberSentinel […]
AutoJack A Single Web Page Can Hijack Your AI Agent to Execute Malicious Code
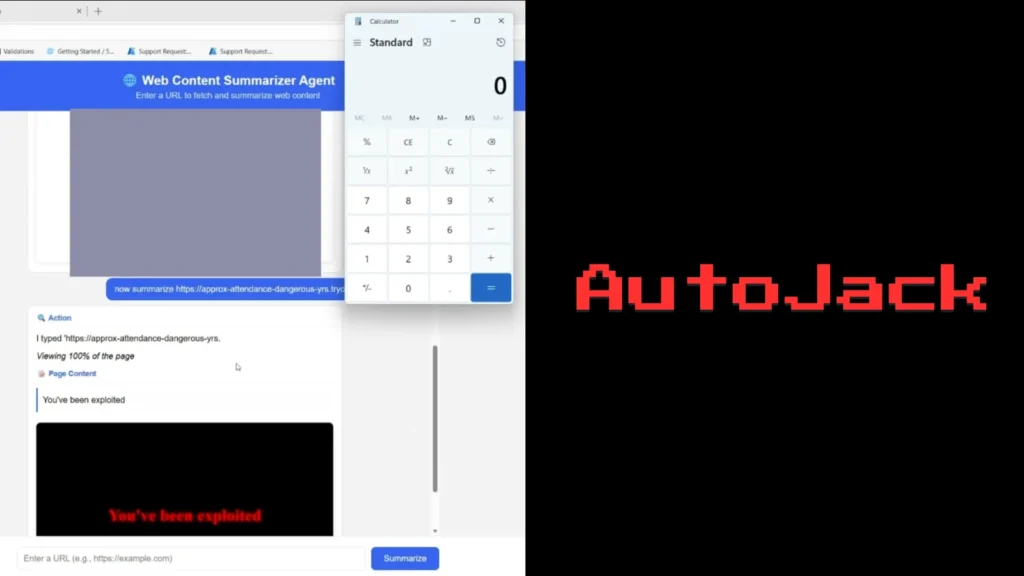
A critical exploit chain dubbed AutoJack that allows a single malicious web page to hijack Microsoft’s AutoGen Studio browsing agent and execute arbitrary code on the host machine without any user interaction beyond submitting a URL. AutoJack is a three-vulnerability exploit chain targeting AutoGen Studio, Microsoft Research’s open-source prototyping UI for multi-agent AI systems. The […]
CISA Adds LiteSpeed cPanel Plugin Vulnerability to KEV List Following Active Exploitation
CISA has added a critical LiteSpeed cPanel Plugin vulnerability, tracked as CVE-2026-54420, to its Known Exploited Vulnerabilities (KEV) catalog following evidence of active exploitation in the wild. The flaw affects shared hosting environments and poses a significant risk to servers running CloudLinux with CageFS isolation. The vulnerability is classified as a UNIX symbolic link (symlink) […]
Chrome Extensions Critical Flaws Let Attackers Easily Compromise Millions of Browsers
Critical security flaws discovered in widely used Chrome extensions SiderAI and MaxAI are putting millions of users at risk, enabling attackers to fully compromise browser sessions and potentially access sensitive data across websites and local systems. Security researchers at Rebora Security uncovered vulnerabilities dubbed “Spyder” and “MaXSS” affecting AI-powered “agentic side panel” extensions. These tools, […]
Critical WordPress Plugin Vulnerability Exposes 1 Million Sites to File Deletion Attacks
A critical security vulnerability in the widely used Avada (Fusion) Builder WordPress plugin has exposed over 1 million websites to arbitrary file-deletion attacks, potentially leading to full-site compromise and remote code execution. The flaw, tracked as CVE-2026-8713 with a CVSS score of 9.1, was discovered by security researcher “daroo” and reported through the Wordfence Bug […]
INC Ransomware Uses Rust-Based Windows and Linux/ESXi Encryptors in New Attacks
INC ransomware has grown from a newcomer threat into one of the most dangerous ransomware operations worldwide. What began as an emerging criminal group in mid-2023 has claimed over 800 victims globally, placing it among the top ransomware groups this year. The group runs under a Ransomware-as-a-Service model, recruiting affiliates and supplying them with ready-built […]
Authorities Dismantle SocGholish Malware Network 106 Servers and 101 Domains Seized
Authorities have dismantled the criminal infrastructure behind SocGholish, one of the most persistent malware frameworks active since 2017, seizing 106 servers and 101 domains while remediating nearly 15,000 infected websites worldwide. The coordinated takedown was executed as part of Operation Endgame, launched in 2024 and recognized as the largest international operation ever conducted against ransomware […]
New iPhone BootROM Vulnerability Exposes Apple SoCs to Full Chain-of-Trust Compromise
A novel BootROM vulnerability, dubbed usbliter8, affects Apple devices powered by A12, S4/S5, and A13 SoCs. The exploit chains a hardware-level bug in the Synopsys DWC2 USB controller with a firmware configuration flaw, enabling full application processor boot-chain compromise with no software patch possible due to the immutable nature of BootROM code. According to Paradigm […]