
Critical Plesk Vulnerability Let Users Execute Arbitrary Commands on the Server
A newly disclosed critical vulnerability in Plesk, tracked as CVE-2026-44962, is raising serious security concerns after researchers confirmed it can allow authenticated users to execute arbitrary operating system commands on affected servers. The issue, published in the National Vulnerability Database and GitHub Advisory Database, affects the APS Application Catalog component and has been assigned a […]
Instagram Meta AI Vulnerability Allegedly Enables Password Reset for Accounts
A critical flaw in Meta’s AI-powered account recovery tool on Instagram allowed attackers to hijack high-value accounts by tricking the chatbot into forwarding password reset codes with no verification required. Security researchers ZachXBT and Dark Web Informer were among the first to publicly expose the vulnerability, revealing that threat actors had found a way to […]
Microsoft Releases KB5089573 for Windows 11 to Fix Patch Tuesday Install Issues
Microsoft has rolled out a new cumulative update, KB5089573, for Windows 11 versions 25H2 and 24H2, targeting a critical installation failure that affected users following the May 2026 Patch Tuesday release. The update brings OS builds to 26200.8524 and 26100.8524, respectively, resolving a widely reported error that prevented many systems from completing the monthly security […]
GitLab Patches Multiple Duo AI, DoS, and Authorization Flaws in Community and Enterprise Edition
GitLab has released emergency security updates for both Community Edition (CE) and Enterprise Edition (EE), addressing multiple Duo AI, denial‑of‑service, and authorization flaws in recent versions of the platform. On May 27, 2026, GitLab shipped versions 19.0.1, 18.11.4, and 18.10.7 as security patch releases for self‑managed instances. These builds fix several vulnerabilities across Duo AI […]
Pentest Swarm AI Tool With Live Access to nmap, sqlmap, Burp, Metasploit, and Others
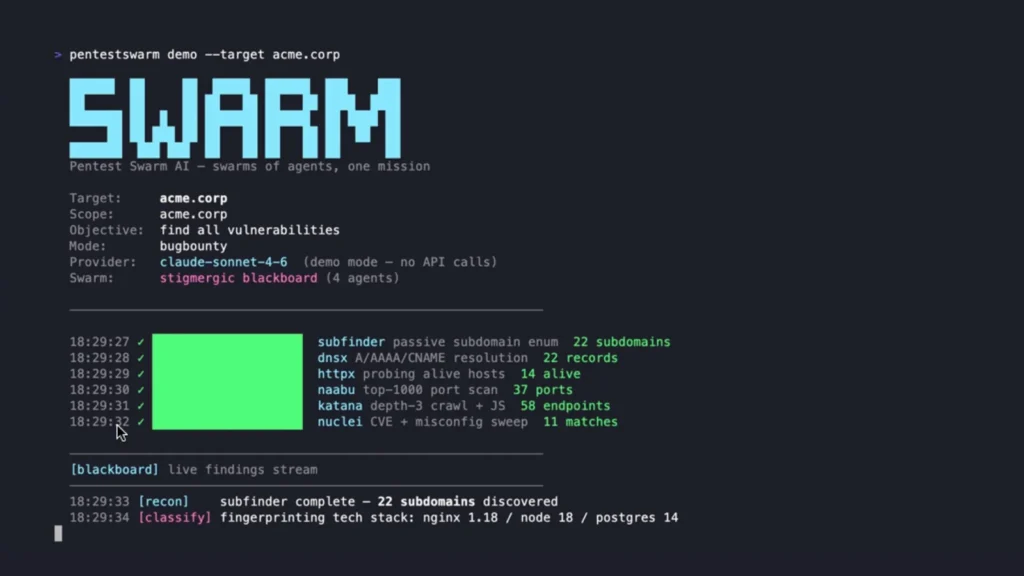
Pentest Swarm AI is the first open-source autonomous penetration testing platform built on a swarm intelligence architecture, not just multiple agents firing in a fixed sequence. Developed by Armur AI, it gives security professionals live, coordinated access to the full offensive stack, including nmap, SQLMap, Burp Suite, ZAP, and Metasploit, all driven by an AI […]
Google Chromes Device-Bound Session Credentials Now GA to Block Account Takeovers
Google has officially moved Device Bound Session Credentials (DBSC) to general availability in the Chrome browser on Windows, delivering a powerful defense against one of the most persistent threats in modern cybersecurity session cookie theft. Previously available in beta for Google Workspace users, DBSC is now enabled by default across all Workspace customers, Individual subscribers, […]
GREYVIBE Hackers Leverage ChatGPT and Google Gemini to Fuel Cyberattacks
GREYVIBE hackers are increasingly leveraging generative AI tools such as ChatGPT and Google Gemini to enhance cyberattack operations. The campaign, active since at least August 2025, primarily targets Ukraine and related entities across the government, military, and civilian sectors, highlighting a growing convergence between artificial intelligence and modern cyber warfare. WithSecure researchers identified GREYVIBE as […]
Palo Alto Networks PAN-OS Authentication Vulnerability Bypass Exploited in the Wild
Palo Alto Networks authentication bypass vulnerability, CVE-2026-0257, affecting PAN-OS and Prisma Access, is now being actively exploited in the wild, with CISA adding it to the Known Exploited Vulnerabilities (KEV) catalog on May 29, 2026. Palo Alto Networks published its security advisory on May 13, 2026, warning that CVE-2026-0257 enables a remote unauthenticated attacker to […]
Ransomware Uses SYSTEM Scheduled Task to Encrypt Local Drives With Elevated Privileges
A newly analyzed ransomware strain called The Gentlemen is raising serious alarms across the cybersecurity community. Built in the Go programming language and obfuscated with a tool called Garble, it combines powerful per-file encryption with an aggressive ability to spread itself silently across entire networks without any human intervention. Organizations in education, healthcare, transportation, and […]
Hackers Use Fake Adobe Document Cloud Pages to Deliver ScreenConnect Malware
A sophisticated phishing campaign is actively targeting financial organizations by using fake Adobe Document Cloud pages to silently install ScreenConnect remote access malware on victim machines. The operation is well-structured, deceptive, and difficult to detect because it blends into everyday enterprise software activity. The campaign works by sending phishing emails that look like legitimate Adobe […]