
Hackers Exploit Microsoft Teams Collaboration Features to Impersonate IT Helpdesk Staff
A growing wave of vishing (voice phishing) campaigns in which threat actors abuse Microsoft Teams’ external collaboration features to impersonate IT helpdesk personnel and investigators is now turning to the Microsoft 365 Unified Audit Log (UAL) as a critical forensic data source to reconstruct attack timelines. The attack chain begins when a threat actor operating […]
Hackers Use GHOSTYNETWORKS and OMEGATECH to Host JS Malware Infrastructure
In March 2026, a wave of malicious spam emails began hitting inboxes across multiple countries and industries. Threat actors were quietly distributing a JavaScript-coded backdoor, targeting organizations in sectors as critical as energy, automotive, and government finance. The scale of the operation was wide, and the infrastructure behind it was carefully selected to stay under […]
FortiClient Code Execution Vulnerability Exploited to Deploy EKZ Malware
A newly observed exploitation campaign targeting FortiClient Endpoint Management Server (EMS) has weaponized trusted administrative infrastructure to silently deploy a previously unreported credential stealer across managed enterprise endpoints. In May 2026, Arctic Wolf researchers identified a cluster of malicious activity exploiting CVE-2026-35616, an improper access control vulnerability in FortiClient EMS. The flaw allows unauthenticated threat […]
GHOST STADIUM Phishing Campaign Targets FIFA World Cup Fans With 300+ Fake Domains
As the 2026 FIFA World Cup draws closer, cybercriminals are moving fast to cash in on the excitement. Researchers have uncovered a massive fraud operation targeting fans of the world’s biggest football tournament, with over 300 fake domains already live. The operation is sophisticated, well-funded, and built to deceive even cautious users. With billions of […]
BIND 9 Software Vulnerabilities Exposes Resolvers and Authoritative Servers to Remote Exploits
A series of newly documented vulnerabilities in ISC BIND 9 has raised significant security concerns for DNS infrastructure operators, with multiple flaws enabling denial-of-service (DoS) attacks, memory corruption, and potential remote exploitation. The latest entries in the BIND 9 Software Vulnerability Matrix highlight critical risks affecting both recursive resolvers and authoritative name servers, underscoring the […]
Multiple Angular Language Service Extension Vulnerabilities Enable RCE Attacks
A set of high-severity vulnerabilities has been identified in the Angular Language Service Visual Studio Code extension (Angular.ng-template), potentially exposing developers to remote code execution (RCE) attacks through multiple exploitation paths. The vulnerabilities arise from insecure handling of user-controlled input and unsafe configuration loading within the extension. Researchers found that attackers can exploit trusted development […]
Windows Server 2016 Domain Controller May Fail with 15-Character Hostname
Windows administrators are facing a disruptive bug in Windows Server 2016 following Microsoft’s May 12, 2026, security update KB5087537. The update introduced a critical flaw that caused domain controller discovery to completely fail on servers configured with hostnames exceeding the 15-character NetBIOS limit, leaving administrators unable to perform essential network operations. Microsoft acknowledged the issue […]
Anthropics Restricted Claude Mythos Moves Toward Public Release via Claude Code and Security
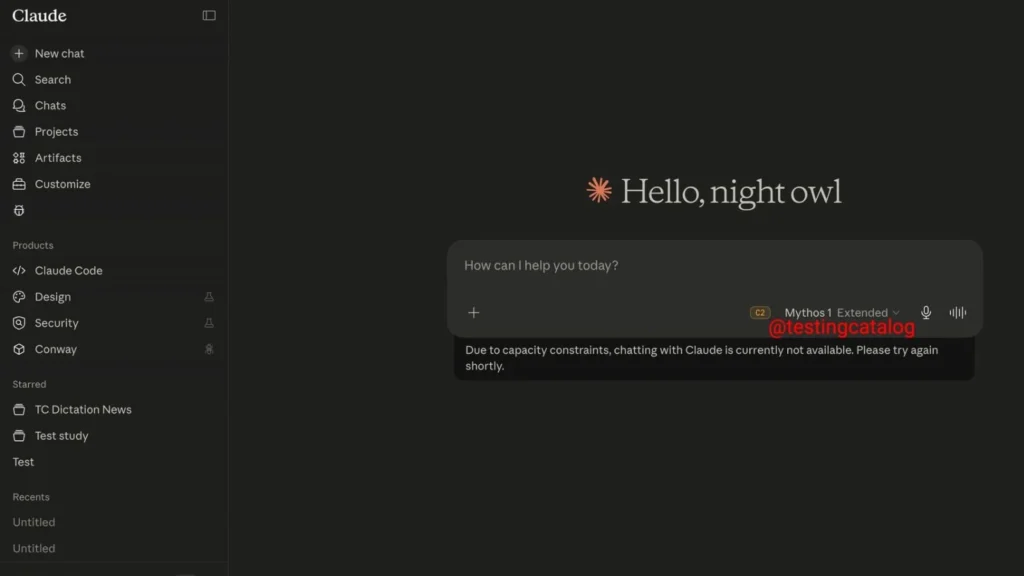
Anthropic appears to be loosening its grip on Claude Mythos, the company’s most powerful and previously restricted AI model, with new signals pointing to a commercially versioned release under the name Mythos 1 (claude-mythos-1-preview), integrated directly into Claude Code and a revamped Claude Security dashboard targeting enterprise customers. Claude Mythos first surfaced in late March […]
InvisibleFerret Malware Now Ships as .pyd and .so Files to Evade Script Detection
A North Korea-linked hacker group has quietly upgraded one of its most dangerous tools, making it harder for security software to detect. InvisibleFerret, an information-stealing malware tied to the threat actor known as Void Dokkaebi (also tracked as Famous Chollima), has been repackaged into a format that slips past many traditional detection methods. Instead of […]
Hackers Actives Scanning SonicWall Firewall Interfaces 597,000 Sessions Observed
A sharp rise in internet-wide scanning activity targeting SonicWall firewall management interfaces has been detected, raising concerns about a potential pre-disclosure reconnaissance phase tied to new vulnerabilities. Threat intelligence firm GreyNoise reported a significant surge in scanning of SonicWall SonicOS management APIs between May 9 and May 18, 2026. The most notable spike occurred on […]