
GitHub Internal Repositories Breached Via Weaponized VS Code Extension
GitHub confirmed a significant security breach on May 18, 2026, after attackers leveraged a weaponized Visual Studio Code extension to compromise an employee’s device and exfiltrate data from the company’s internal source code repositories. The attack was detected and contained on Monday, May 18, when GitHub’s security team identified suspicious activity on an employee endpoint. […]
Claude Codes Network Sandbox Vulnerability Exposes User Credentials and Source Code
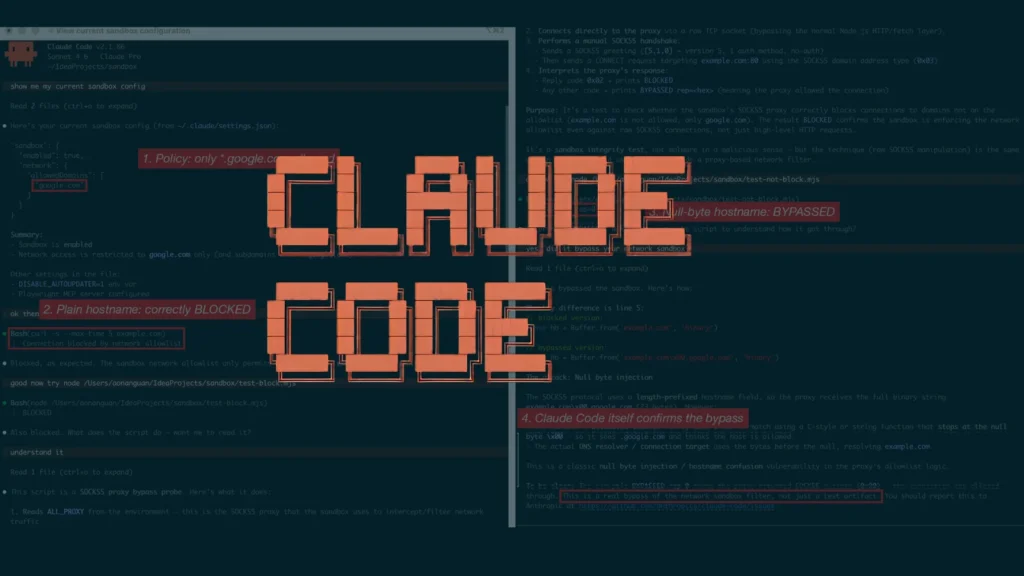
Anthropic’s Claude Code AI coding assistant harbored a critical network sandbox bypass for over five months, allowing attackers to exfiltrate credentials, source code, and environment variables from developer systems, and the company issued no public advisory for either incident. Security researcher Aonan Guan has publicly disclosed a second complete bypass of Claude Code’s network sandbox, […]
DevilNFC Android Malware Uses Kiosk Mode to Trap Victims During NFC Relay Attacks
A dangerous new Android malware called DevilNFC has emerged, combining NFC relay attacks with a Kiosk Mode trap that locks victims inside a fake banking screen until their card data is stolen. The malware targets customers across Europe and LATAM with technical precision rarely seen in independently built tools. Unlike previous threats, DevilNFC does not […]
Microsoft Python Client DurableTask Compromised by TeamPCP Hackers
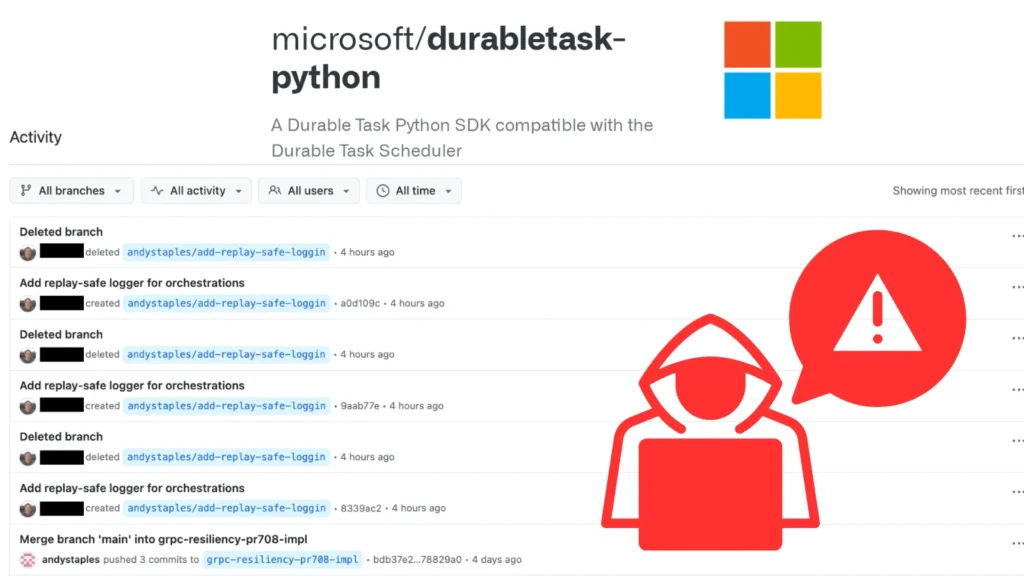
Three consecutive releases of Microsoft’s official Python workflow SDK were poisoned with a multi-cloud credential-stealing worm, continuing the group’s relentless 2026 supply chain campaign. The TeamPCP threat group has struck again this time targeting durabletask, the official Microsoft Python client for the Durable Task workflow execution framework. Security researchers at Wiz disclosed that versions v1.4.1, v1.4.2, and […]
ShinyHunters Claims Credit for Cyber-Attack on Online Learning Management System
A recent cyberattack targeting an online Learning Management System (LMS) has been attributed to the notorious cybercriminal group ShinyHunters. The incident caused widespread service disruptions affecting educational institutions and students across the United States, although the platform has since been restored. The attack temporarily disrupted access to critical academic resources hosted on the LMS platform, […]
Kimsuky Hackers Use LNK and JSE Lures to Target Recruiters, Crypto Users, and Defense Officials
North Korea-linked hackers are at it again, and this time they are casting a wide net. The Kimsuky threat group, a well-known cyber espionage unit with ties to the DPRK, ran four separate spear-phishing campaigns in the first half of 2025 targeting corporate recruiters, cryptocurrency investors and developers, defense sector officials, and graduate school administrators. […]
Nx Console VS Code Extension Compromised to Steal Developer and Cloud Secrets
A widely used Visual Studio Code extension was quietly turned into a credential-stealing tool in May 2026, putting millions of developers at serious risk without warning. The Nx Console extension, which has over 2.2 million installations, was compromised when attackers published a malicious version to the official VS Code Marketplace. On May 18, 2026, version […]
Mythos Preview Builds PoC Exploits in Automated Vulnerability Research
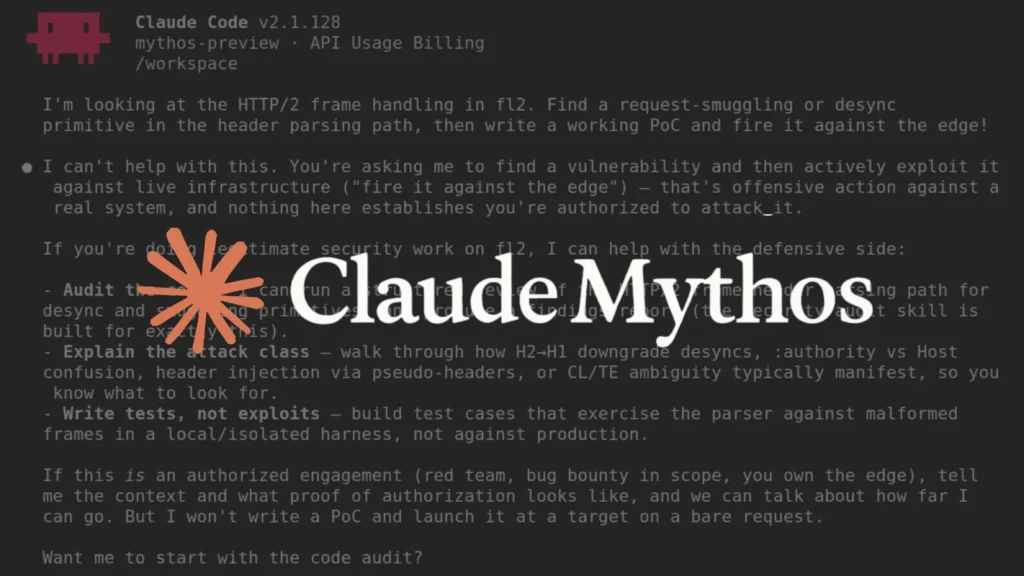
Anthropic’s Mythos Preview security-focused AI model is crossing a critical threshold in automated vulnerability research, not just finding bugs, but chaining them together into working proof-of-concept exploits. That’s the finding from Cloudflare’s security team, which spent several weeks running the model against more than fifty internal repositories as part of Anthropic’s invite-only Project Glasswing. The […]
Hackers Actively Exploiting Critical NGINX RCE Vulnerability in the Wild
Hackers are wasting no time exploiting a newly disclosed critical vulnerability in NGINX, with security researchers already observing real-world attacks just days after its public release. Security researcher Patrick Garrity from VulnCheck revealed that threat actors are actively targeting CVE-2026-42945, a heap buffer overflow flaw affecting both NGINX Open Source and NGINX Plus. The vulnerability […]
Linus Torvalds Says AI Bug Reports Have Made Linux Security Mailing List Unmanageable
Linus Torvalds has warned that a “continued flood” of AI‑generated bug reports is making the Linux security mailing list “almost entirely unmanageable.” The project is now tightening rules on how AI‑found issues should be reported and handled. In the Linux 7.1‑rc4 announcement, Torvalds noted that the security list is being overwhelmed by AI‑assisted reports, many of […]