
New Ivanti EPMM 0-Day Vulnerability Actively Exploited in Attacks
Ivanti has issued a critical security advisory for its Endpoint Manager Mobile (EPMM) product, disclosing multiple actively exploited vulnerabilities, including CVE-2026-6973, and urging all on-premises EPMM customers to apply patches immediately. At the time of disclosure, Ivanti confirmed active exploitation of CVE-2026-6973, a vulnerability that requires admin authentication to succeed. The flaws exclusively affect the […]
CISA Warns of Palo Alto PAN-OS Vulnerability Exploited to Gain Root Access
CISA has issued an urgent warning regarding a critical vulnerability in Palo Alto Networks PAN-OS. Tracked as CVE-2026-0300, this severe security flaw was recently added to CISA’s Known Exploited Vulnerabilities catalog on May 6, 2026. The vulnerability allows unauthenticated threat actors to execute arbitrary code and gain root privileges on affected firewall appliances, prompting immediate […]
Critical Ollama Memory Leak Vulnerability Exposes 300,000 Servers Globally
A major security flaw has placed Ollama, one of the most widely used platforms for running local AI models, at risk of a high-profile exposure event. The issue, dubbed “Bleeding Llama,” allows unauthenticated attackers to access the Ollama process and extract sensitive data directly from memory, putting roughly 300,000 internet-facing servers worldwide at risk. With […]
Darkhub Hacking-for-Hire Portal Advertises Crypto Fraud, Message Interception, and Monitoring
A dark web platform calling itself Darkhub has surfaced on the Tor network, openly advertising hacking-for-hire services to anyone willing to pay. The platform presents itself as a one-stop shop for illegal cyber activity, with offerings ranging from breaking into social media accounts to intercepting private messages and manipulating financial records. What makes Darkhub notable […]
Hackers Use Microsoft Teams to Steal Credentials and Manipulate MFA
Iranian APT group MuddyWater deployed Chaos ransomware as a “false flag” in a sophisticated hybrid espionage campaign targeting Western organizations, bypassing encryption in favor of data theft and long-term persistence. In early 2026, Rapid7 incident responders were called into what initially appeared to be a routine Chaos ransomware intrusion, but forensic analysis quickly revealed something […]
Low Noise, High Confidence:OptimizingSOC Costs with Better Threat Intelligence
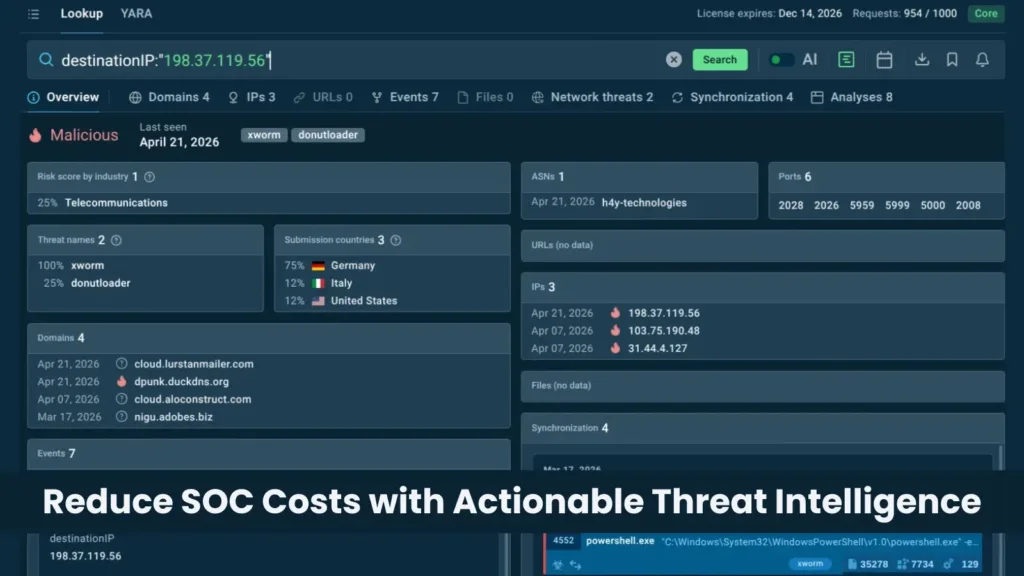
Robust defense systems are built on a clear understanding of current threats and the ability to translate it into consistent decisions and measurable outcomes at optimal cost. High-performing SOCs achieve this by eliminating unnecessary work and operationalizing threat data. At the core of this model lies threat intelligence that is: Relevant to active threats Actionable within existing workflows Curated to reduce false alerts Not all threat data sources meet these criteria. The difference becomes evident in how effectively they reduce investigation […]
New ScarCruft Supply Chain Attack Hits Gaming Platform With Windows and Android Backdoors
A North Korea-aligned threat group known as ScarCruft has been caught running a supply chain attack against a video gaming platform serving ethnic Koreans in China’s Yanbian region. The attackers planted backdoors in both Windows and Android versions of the platform’s games, turning a trusted service into a covert espionage tool. The campaign has likely […]
Critical Android Zero-Click Vulnerability Grants Remote Shell Access
Google has published the May 2026 Android Security Bulletin, alerting the ecosystem to a highly severe remote code execution (RCE) flaw. Tracked as CVE-2026-0073, this critical vulnerability resides deep within the core Android System component. It allows an attacker to gain remote shell access without requiring a single tap, download, or click from the device […]
DigiCert Hacked via Weaponized Screensaver File to Obtain EV Code Signing Certificates
A sophisticated threat actor breached DigiCert’s internal support environment in early April 2026 by tricking support analysts into executing a disguised malicious screensaver file, ultimately obtaining stolen EV Code Signing certificates used to distribute the “Zhong Stealer” malware family. On April 2, 2026, a threat actor contacted DigiCert’s customer support team through a Salesforce-based chat […]
Malicious Tanstack Package Uses Postinstall Script to Steal Developer Environment Files
A malicious npm package impersonating the widely trusted TanStack project was discovered on April 29, 2026, silently stealing developer environment files the moment it was installed. The attacker registered the unscoped “tanstack” package name on npm, dressed it up as a legitimate video player SDK called “TanStackPlayer,” and embedded a credential-harvesting script inside it that […]