
Threat Actors Use AI to Automate 0-Day Discovery and Exploitation at Machine Speed
The way cyberattacks are launched has fundamentally changed. Threat actors are no longer spending months hunting for software flaws by hand. With artificial intelligence in their toolkit, they can now discover and exploit zero-day vulnerabilities in minutes, placing organizations across every sector at serious risk. For years, finding a zero-day required deep technical skill, long […]
Microsoft Defender Mistakenly Flags DigiCert Root Certificates as Malware
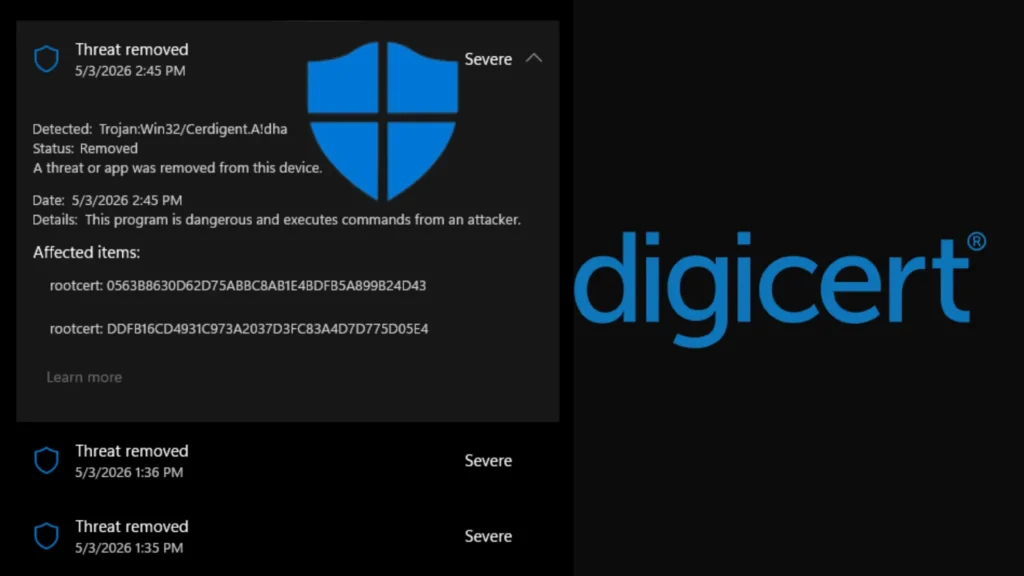
Microsoft Defender triggered widespread false positive alerts after a faulty security update caused it to flag two legitimate DigiCert root certificates as malicious, potentially disrupting SSL/TLS validation and code-signing operations across enterprise environments worldwide. A Defender antimalware signature update released around April 30, 2026, introduced a detection labeled Trojan:Win32/Cerdigent.A!dha, which incorrectly identified registry entries belonging […]
Trellix Source Code Breach Hackers Gain Unauthorized Access to Repository
Cybersecurity giant Trellix has disclosed a significant security incident involving unauthorized access to a portion of its source code repository. The company confirmed the breach in an official statement published on its website, stating it immediately engaged leading forensic experts upon discovering the intrusion. Threat actors gained unauthorized access to part of Trellix’s internal source […]
Hackers Breach Government and Military Servers by Exploiting cPanel Vulnerability
A sophisticated adversarial campaign targeting South-East Asian government and military infrastructure, combining rapid exploitation of a critical cPanel authentication bypass with a custom zero-day exploit chain against an Indonesian defense-sector portal and ultimately pivoting to exfiltrate over 4GB of sensitive Chinese railway documents. The campaign’s initial access vector centered on CVE-2026-41940, a critical CVSS 9.8 […]
Multiple Exim Mail Server Vulnerabilities Leads to Crash with Malicious DNS data
The Exim development team has released version 4.99.2 to address four newly discovered security vulnerabilities affecting their mail server software. These flaws allow attackers to potentially crash servers, corrupt memory, or leak sensitive information. Because Exim is one of the most widely used message transfer agents on the internet, system administrators need to apply this […]
Attackers Deploy AiTM Phishing Pages to Access SharePoint, HubSpot, and Google Workspace
Threat actors are rapidly shifting their intrusion tradecraft toward high-speed, SaaS-centric attacks that completely bypass traditional endpoint security. Since October 2025, security researchers have tracked two distinct adversaries, identified as CORDIAL SPIDER and SNARKY SPIDER, conducting aggressive data theft campaigns. These groups operate almost exclusively within trusted SaaS environments such as SharePoint, HubSpot, and Google […]
Attackers Abuse Google AppSheet, Netlify, and Telegram in Facebook Phishing Campaign
A sophisticated cybercriminal operation dubbed “AccountDumpling” has compromised approximately 30,000 Facebook accounts worldwide. Discovered by Guardio Labs, this Vietnamese-linked campaign abuses Google’s AppSheet platform to bypass traditional email security filters. By routing fully authenticated phishing lures through legitimate channels, the attackers successfully harvest credentials and identity documents. These stolen Facebook Business accounts are subsequently monetized […]
EtherRAT Campaign Uses SEO Poisoning and GitHub Facades to Target Enterprise Admins
A new and well-planned malware campaign has been actively targeting enterprise administrators, DevOps engineers, and security analysts by hijacking their everyday search habits. Rather than using mass phishing or broad spam waves, threat actors behind this operation have carefully crafted a delivery chain that puts dangerous software directly in front of high-privilege IT professionals when […]
Ransomware Victims Jump to 7,831 as AI Crime Tools Scale Global Attacks
The ransomware threat has reached a new and alarming level. According to Fortinet’s newly released 2026 Global Threat Landscape Report, the number of confirmed ransomware victims worldwide jumped to 7,831 in 2025, up from roughly 1,600 victims recorded in the previous year’s report. That is a 389% increase year-over-year, a rise that reflects how deeply […]
Qilin Ransomware Enumerates RDP Authentication History on a Compromised Server
Qilin ransomware is one of the most active and damaging threats in the cyber landscape today. The group has steadily evolved its tactics since it first appeared in 2022, and its latest technique of enumerating Remote Desktop Protocol (RDP) authentication history on compromised servers gives it a fast, quiet way to map out a network […]