
Pentest Agent Suite Bug Bounty Framework for Claude Code and 6 AI Coding Tools
A fully autonomous bug-bounty framework called Pentest Agent Suite has been open-sourced, delivering 50 specialized security agents, 26 slash commands, 19 CLI tools, and a cross-IDE installer across seven major AI coding platforms — Claude Code, OpenAI Codex, Google Gemini, Cursor, Windsurf, VS Code Copilot, and OpenClaw. The project, published on GitHub by researcher H-mmer, […]
PyrsistenceSniper Tool that Detects 117 Persistence Malware Techniques on Windows, Linux, and macOS
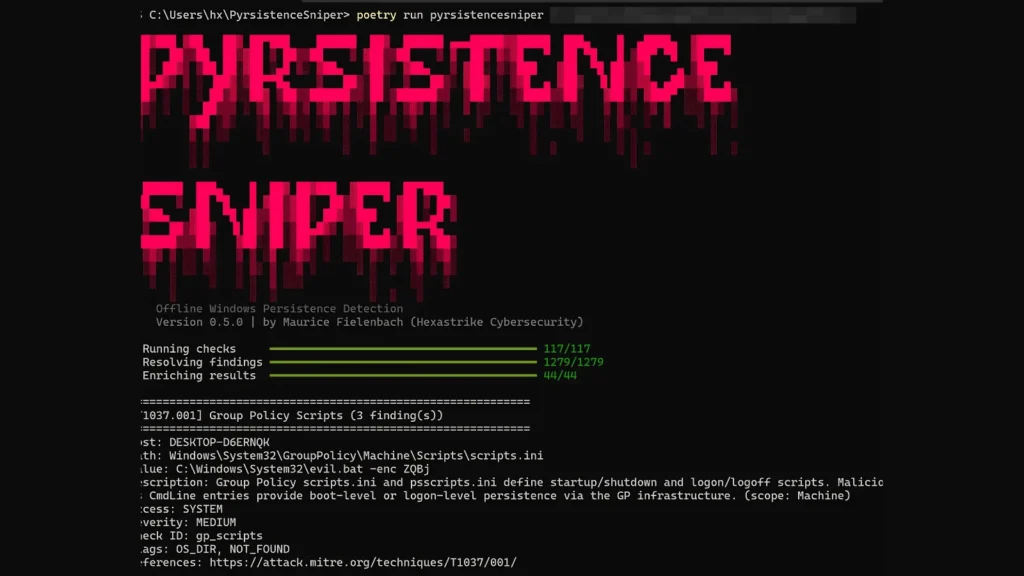
PyrsistenceSniper is an advanced tool for detecting offline persistence, enabling cybersecurity analysts to identify 117 separate persistence mechanisms across Windows, Linux, and macOS platforms. Originally inspired by Autoruns and PersistenceSniper, this Python-based solution developed by Hexastrike enables rapid triage of forensic collections without requiring live system access. According to the Hexastrike GitHub repository, PyrsistenceSniper runs […]
Nginx-poolslip Vulnerability Enables DoS and Code Execution Attacks Patch Now!
A newly disclosed flaw in one of the world’s most widely deployed web servers is forcing administrators into another emergency patch cycle. Tracked as CVE-2026-9256 and publicly nicknamed nginx-poolslip, the vulnerability affects both NGINX Plus and NGINX Open Source, and can be triggered by a remote, unauthenticated attacker over plain HTTP. The vulnerability resides in […]
Hackers Exploit F5 BIG-IP Appliance to Gain SSH Access and Pivot Into Enterprise Linux Networks
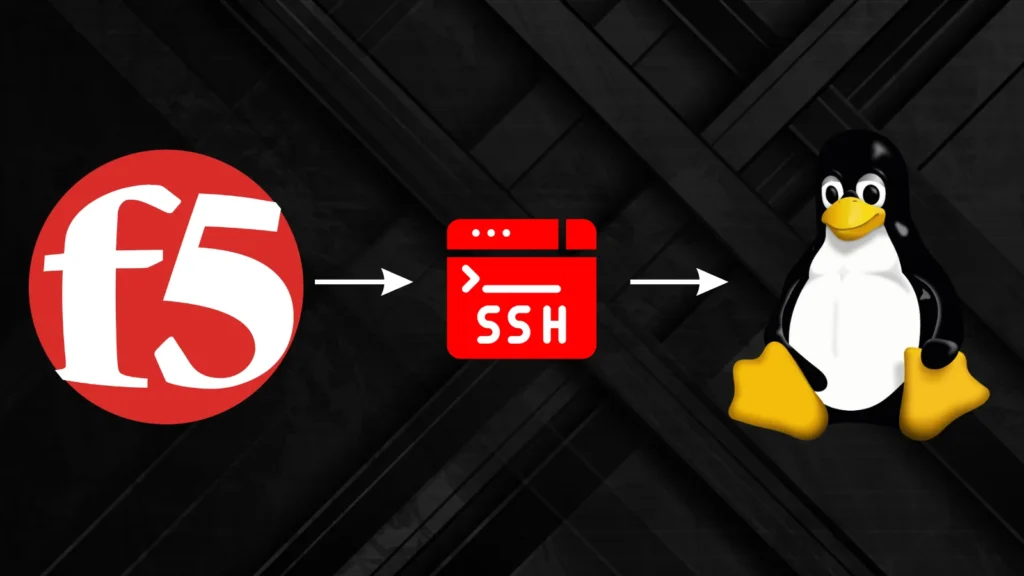
A multi-stage intrusion attack where a threat actor exploited an internet-facing F5 BIG-IP edge appliance as the entry point for a widespread, identity-focused attack that ultimately accessed Active Directory. According to Microsoft’s Defender Security Research, the attack reflects a growing trend in which firewalls, VPN gateways, and load balancer devices traditionally deployed as security boundaries […]
Hackers Compromised 233 Versions of Laravel-Lang Packages by Hacking 700 GitHub Repos
A highly sophisticated supply chain attack has compromised the Laravel-Lang ecosystem, injecting credential-stealing remote code execution backdoors into 233 package versions across 700 GitHub repositories. Discovered in May 2026 by Socket and Aikido, threat actors manipulated GitHub tags to distribute malware through Composer’s autoloader, granting complete remote access to developer environments. The attackers bypassed direct […]
Anthropics Claude Mythos Preview Uncovers 10,000+ 0-Days in Project Glasswing
Anthropic has revealed the staggering initial results of Project Glasswing, a collaborative cybersecurity initiative designed to secure critical infrastructure using advanced AI before malicious actors can exploit it. In its first month, the project leveraged the unreleased Claude Mythos Preview model to autonomously discover over 10,000 high- and critical-severity zero-day vulnerabilities across the world’s most […]
Ubiquiti Patches Critical UniFi OS Vulnerabilities Allowing Remote Privilege Escalation
Ubiquiti Networks has released urgent security updates to address a series of highly critical vulnerabilities affecting its UniFi OS platform. These severe flaws could allow unauthenticated, remote attackers to execute arbitrary code, escalate privileges, and severely compromise enterprise network infrastructure. In total, the hardware vendor patched five distinct security issues, three of which carry a […]
Splunk Patches Multiple Vulnerabilities that Enable DOS Attack and Exposes Sensitive Data
Splunk has released security updates addressing multiple vulnerabilities across Splunk Enterprise, Splunk Cloud Platform, and the Splunk AI Toolkit that could lead to denial-of-service (DoS) conditions and exposure of sensitive data. The issues, disclosed on May 20, 2026, include three tracked vulnerabilities: CVE-2026-20238, CVE-2026-20239, and CVE-2026-20240. Splunk AI Toolkit Access Flaw (CVE-2026-20238) A medium-severity flaw […]
Discord Announces End-to-End Encryption by Default for Video and Voice Messages
Discord has officially rolled out end-to-end encryption (E2EE) for all voice and video communications across its platform, marking a major milestone in secure real-time communication. The feature, now enabled by default as of March 2026, applies to direct messages, group calls, voice channels, and Go Live streams without requiring any user opt-in. At the core […]
Hackers Use Fake Microsoft Teams Downloads to Deploy ValleyRAT Malware
Hackers have been caught running a deceptive campaign that uses fake Microsoft Teams download websites to trick users into installing ValleyRAT, a remote access trojan capable of stealing data, logging keystrokes, and taking remote control of infected machines. The campaign, which first surfaced in mid-April 2026, targets unsuspecting users who believe they are downloading the […]